
Oracle Critical Patch Update April 2019
Released April 2019 · Oracle's advisory ↗ · ← Critical Patch Update, January 2019 · Critical Patch Update, July 2019 →
207 CVEs in this release, one square each
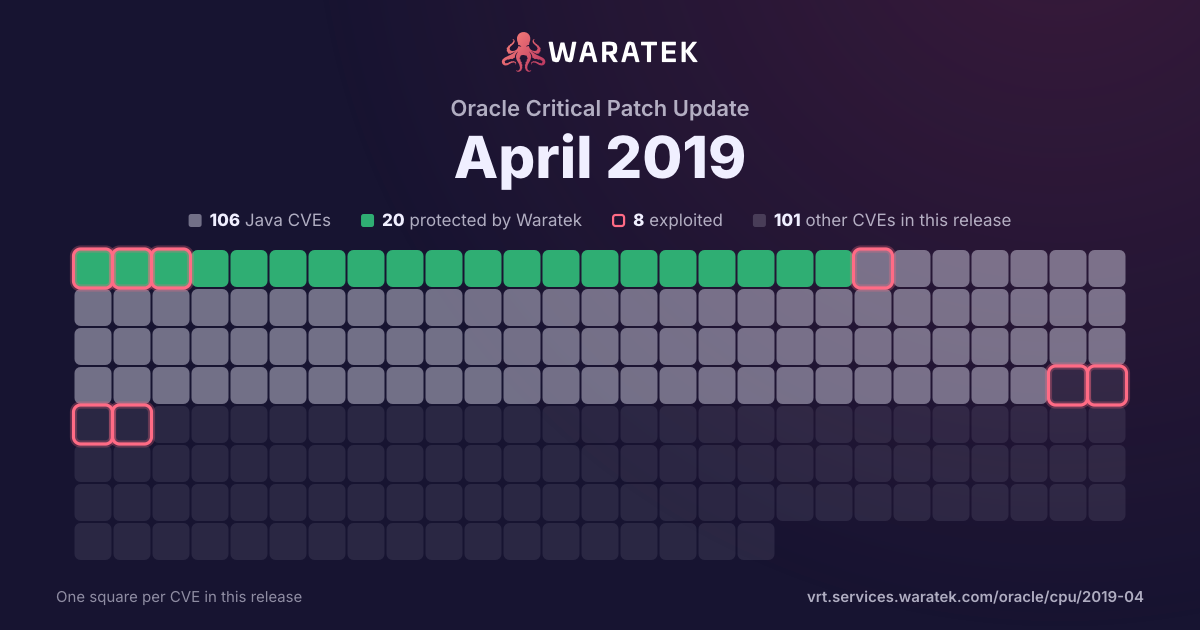
By status
20Protected by Waratek3Mitigation candidate83No exploit published58Outside Waratek scope43Not applicable
8Exploited, marked by the ring
No exploit published. For 80 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 28 matches · 16 in Waratek scope · 9 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
28matches
16in Waratek scope57.1%
9protected32.1%
0exploited0.0%
0CISA KEV0.0%
1public PoC3.6%
1EPSS ≥ 0.53.6%
Protected by Waratek
9
32.1%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
7
25.0%
Outside Waratek scope
5
17.9%
Not applicable
7
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
9
32.1%
partly blocked
0
0.0%
not blocked
19
67.9%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
3.6%
Proof of concept only
1
3.6%
Forecast only
0
0.0%
No public exploit
26
92.9%
split by
peak 8 / quarter
Q3 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 150
Q1 160
Q2 161
No exploit published1
Critical1
not blocked1
No public exploit1
Q3 160
Q4 162
Protected by Waratek1
Outside Waratek scope1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 170
Q2 173
Protected by Waratek1
Not applicable2
Critical3
blocked by ARMR today1
not blocked2
Working exploit published1
No public exploit2
Q3 171
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Q4 173
Not applicable3
Critical3
not blocked3
Proof of concept only1
No public exploit2
Q1 182
Protected by Waratek2
Critical2
blocked by ARMR today2
No public exploit2
Q2 183
Protected by Waratek1
Outside Waratek scope1
Not applicable1
Critical3
blocked by ARMR today1
not blocked2
No public exploit3
Q3 180
Q4 180
Q1 194
Protected by Waratek3
Outside Waratek scope1
Critical4
blocked by ARMR today3
not blocked1
No public exploit4
Q2 198
No exploit published6
Outside Waratek scope1
Not applicable1
Critical8
not blocked8
No public exploit8
Q4 15Q2 16Q4 16Q2 17Q4 17Q2 18Q4 18Q2 19
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2019-2702 | Critical | 2019-04-23 | Not applicable | No public exploit | Vulnerability in the Oracle Hospitality Cruise Dining Room Management component of Oracle Hospitality Applications (subcomponent: Web Service). The supported version that is affected is 8.0.80. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality Cruise Dining Room Management. While the vulnerability is in Oracle Hospitality Cruise Dining Room Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality Cruise Dining Room Management accessible data as well as unauthorized update, insert or delete access to some of Oracle Hospitality Cruise Dining Room Management accessible data. CVSS 3.0 Base Score 9.3 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:H/I:L/A:N). |
| CVE-2019-2699 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Java SE component of Oracle Java SE (subcomponent: Windows DLL). The supported version that is affected is Java SE: 8u202. Difficult to exploit vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise Java SE. While the vulnerability is in Java SE, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Java SE. Note: This vulnerability applies to Java deployments, typically in clients running sandboxed Java Web Start applications or sandboxed Java applets (in Java SE 8), that load and run untrusted code (e.g., code that comes from the internet) and rely on the Java sandbox for security. This vulnerability can also be exploited by using APIs in the specified Component, e.g., through a web service which supplies data to the APIs. CVSS 3.0 Base Score 9.0 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2019-2658 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS Core Components). Supported versions that are affected are 10.3.6.0.0 and 12.1.3.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2646 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: EJB Container). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2645 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle WebLogic Server component of Oracle Fusion Middleware (subcomponent: WLS Core Components). Supported versions that are affected are 10.3.6.0.0, 12.1.3.0.0 and 12.2.1.3.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via T3 to compromise Oracle WebLogic Server. Successful attacks of this vulnerability can result in takeover of Oracle WebLogic Server. CVSS 3.0 Base Score 9.8 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:H). |
| CVE-2019-2638 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle General Ledger component of Oracle E-Business Suite (subcomponent: Consolidation Hierarchy Viewer). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle General Ledger. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle General Ledger accessible data as well as unauthorized access to critical data or complete access to all Oracle General Ledger accessible data. CVSS 3.0 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:L). |
| CVE-2019-2633 | Critical | 2019-04-23 | No exploit published | No public exploit | Vulnerability in the Oracle Work in Process component of Oracle E-Business Suite (subcomponent: Messages). Supported versions that are affected are 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, 12.2.5, 12.2.6, 12.2.7 and 12.2.8. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Work in Process. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Work in Process accessible data as well as unauthorized access to critical data or complete access to all Oracle Work in Process accessible data. CVSS 3.0 Base Score 9.9 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:L). |
| CVE-2019-2517 | Critical | 2019-04-23 | Outside Waratek scope | No public exploit | Vulnerability in the Core RDBMS component of Oracle Database Server. Supported versions that are affected are 12.2.0.1 and 18c. Easily exploitable vulnerability allows high privileged attacker having DBFS_ROLE privilege with network access via Oracle Net to compromise Core RDBMS. While the vulnerability is in Core RDBMS, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in takeover of Core RDBMS. CVSS 3.0 Base Score 9.1 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:N/S:C/C:H/I:H/A:H). |
| CVE-2019-3822 | Critical | 2019-02-06 | Outside Waratek scope | No public exploit | libcurl versions from 7.36.0 to before 7.64.0 are vulnerable to a stack-based buffer overflow. The function creating an outgoing NTLM type-3 header (`lib/vauth/ntlm.c:Curl_auth_create_ntlm_type3_message()`), generates the request HTTP header contents based on previously received data. The check that exists to prevent the local buffer from getting overflowed is implemented wrongly (using unsigned math) and as such it does not prevent the overflow from happening. This output data can grow larger than the local buffer if very large 'nt response' data is extracted from a previous NTLMv2 header provided by the malicious or broken HTTP server. Such a 'large value' needs to be around 1000 bytes or more. The actual payload data copied to the target buffer comes from the NTLMv2 type-2 response header. |
| CVE-2019-3772 | Critical | 2019-01-18 | Protected by Waratek | No public exploit | Spring Integration (spring-integration-xml and spring-integration-ws modules), versions 4.3.18, 5.0.10, 5.1.1, and older unsupported versions, were susceptible to XML External Entity Injection (XXE) when receiving XML data from untrusted sources. |
| CVE-2018-19362 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.8 might allow attackers to have unspecified impact by leveraging failure to block the jboss-common-core class from polymorphic deserialization. |
| CVE-2018-14718 | Critical | 2019-01-02 | Protected by Waratek | No public exploit | FasterXML jackson-databind 2.x before 2.9.7 might allow remote attackers to execute arbitrary code by leveraging failure to block the slf4j-ext class from polymorphic deserialization. |
| CVE-2018-11219 | Critical | 2018-06-17 | Not applicable | No public exploit | An Integer Overflow issue was discovered in the struct library in the Lua subsystem in Redis before 3.2.12, 4.x before 4.0.10, and 5.x before 5.0 RC2, leading to a failure of bounds checking. |
| CVE-2018-8013 | Critical | 2018-05-24 | Protected by Waratek | No public exploit | In Apache Batik 1.x before 1.10, when deserializing subclass of `AbstractDocument`, the class takes a string from the inputStream as the class name which then use it to call the no-arg constructor of the class. Fix was to check the class type before calling newInstance in deserialization. |
| CVE-2018-11236 | Critical | 2018-05-18 | Outside Waratek scope | No public exploit | stdlib/canonicalize.c in the GNU C Library (aka glibc or libc6) 2.27 and earlier, when processing very long pathname arguments to the realpath function, could encounter an integer overflow on 32-bit architectures, leading to a stack-based buffer overflow and, potentially, arbitrary code execution. |
| CVE-2018-8088 | Critical | 2018-03-20 | Protected by Waratek | No public exploit | org.slf4j.ext.EventData in the slf4j-ext module in QOS.CH SLF4J before 1.8.0-beta2 allows remote attackers to bypass intended access restrictions via crafted data. EventData in the slf4j-ext module in QOS.CH SLF4J, has been fixed in SLF4J versions 1.7.26 later and in the 2.0.x series. |
| CVE-2018-7489 | Critical | 2018-02-26 | Protected by Waratek | No public exploit | FasterXML jackson-databind before 2.7.9.3, 2.8.x before 2.8.11.1 and 2.9.x before 2.9.5 allows unauthenticated remote code execution because of an incomplete fix for the CVE-2017-7525 deserialization flaw. This is exploitable by sending maliciously crafted JSON input to the readValue method of the ObjectMapper, bypassing a blacklist that is ineffective if the c3p0 libraries are available in the classpath. |
| CVE-2014-9515 | Critical | 2017-12-29 | Not applicable | Proof of concept only | Dozer improperly uses a reflection-based approach to type conversion, which might allow remote attackers to execute arbitrary code via a crafted serialized object. |
| CVE-2017-5533 | Critical | 2017-11-15 | Not applicable | No public exploit | A vulnerability in the server content cache of TIBCO JasperReports Server, TIBCO JasperReports Server Community Edition, TIBCO JasperReports Server for ActiveMatrix BPM, TIBCO Jaspersoft for AWS with Multi-Tenancy, and TIBCO Jaspersoft Reporting and Analytics for AWS contains a vulnerability which fails to prevent remote access to all the contents of the web application, including key configuration files. Affected releases are TIBCO JasperReports Server 6.4.0, TIBCO JasperReports Server Community Edition 6.4.0, TIBCO JasperReports Server for ActiveMatrix BPM 6.4.0, TIBCO Jaspersoft for AWS with Multi-Tenancy 6.4.0, TIBCO Jaspersoft Reporting and Analytics for AWS 6.4.0. |
| CVE-2017-14952 | Critical | 2017-10-16 | Not applicable | No public exploit | Double free in i18n/zonemeta.cpp in International Components for Unicode (ICU) for C/C++ through 59.1 allows remote attackers to execute arbitrary code via a crafted string, aka a "redundant UVector entry clean up function call" issue. |
| CVE-2016-4000 | Critical | 2017-07-06 | Protected by Waratek | No public exploit | Jython before 2.7.1rc1 allows attackers to execute arbitrary code via a crafted serialized PyFunction object. |
| CVE-2017-8287 | Critical | 2017-04-27 | Not applicable | No public exploit | FreeType 2 before 2017-03-26 has an out-of-bounds write caused by a heap-based buffer overflow related to the t1_builder_close_contour function in psaux/psobjs.c. |
| CVE-2017-8105 | Critical | 2017-04-24 | Not applicable | No public exploit | FreeType 2 before 2017-03-24 has an out-of-bounds write caused by a heap-based buffer overflow related to the t1_decoder_parse_charstrings function in psaux/t1decode.c. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2015-1832 | Critical | 2016-10-03 | Outside Waratek scope | No public exploit | XML external entity (XXE) vulnerability in the SqlXmlUtil code in Apache Derby before 10.12.1.1, when a Java Security Manager is not in place, allows context-dependent attackers to read arbitrary files or cause a denial of service (resource consumption) via vectors involving XmlVTI and the XML datatype. |
| CVE-2016-2141 | Critical | 2016-06-30 | No exploit published | No public exploit | It was found that JGroups did not require necessary headers for encrypt and auth protocols from new nodes joining the cluster. An attacker could use this flaw to bypass security restrictions, and use this vulnerability to send and receive messages within the cluster, leading to information disclosure, message spoofing, or further possible attacks. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |