
Oracle Critical Patch Update April 2019
Released April 2019 · Oracle's advisory ↗ · ← Critical Patch Update, January 2019 · Critical Patch Update, July 2019 →
207 CVEs in this release, one square each
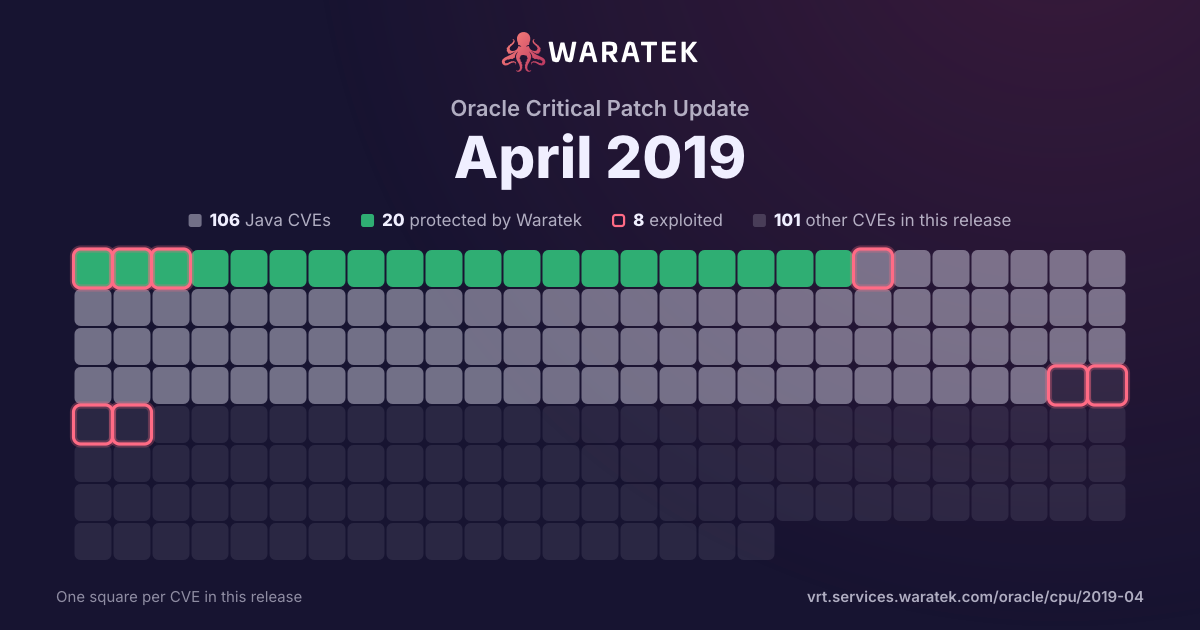
By status
20Protected by Waratek3Mitigation candidate83No exploit published58Outside Waratek scope43Not applicable
8Exploited, marked by the ring
No exploit published. For 80 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 2 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
2
66.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
33.3%
blocked by ARMR today
2
66.7%
partly blocked
0
0.0%
not blocked
1
33.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
33.3%
Forecast only
0
0.0%
No public exploit
2
66.7%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-11761 | High | 2018-09-19 | Protected by Waratek | Proof of concept only | In Apache Tika 0.1 to 1.18, the XML parsers were not configured to limit entity expansion. They were therefore vulnerable to an entity expansion vulnerability which can lead to a denial of service attack. |
| CVE-2018-11775 | High | 2018-09-10 | No exploit published | No public exploit | TLS hostname verification when using the Apache ActiveMQ Client before 5.15.6 was missing which could make the client vulnerable to a MITM attack between a Java application using the ActiveMQ client and the ActiveMQ server. This is now enabled by default. |
| CVE-2018-1656 | High | 2018-08-20 | Protected by Waratek | No public exploit | The IBM Java Runtime Environment's Diagnostic Tooling Framework for Java (DTFJ) (IBM SDK, Java Technology Edition 6.0 , 7.0, and 8.0) does not protect against path traversal attacks when extracting compressed dump files. IBM X-Force ID: 144882. |