
Oracle Critical Patch Update January 2019
Released January 2019 · Oracle's advisory ↗ · ← Critical Patch Update, October 2018 · Critical Patch Update, April 2019 →
198 CVEs in this release, one square each
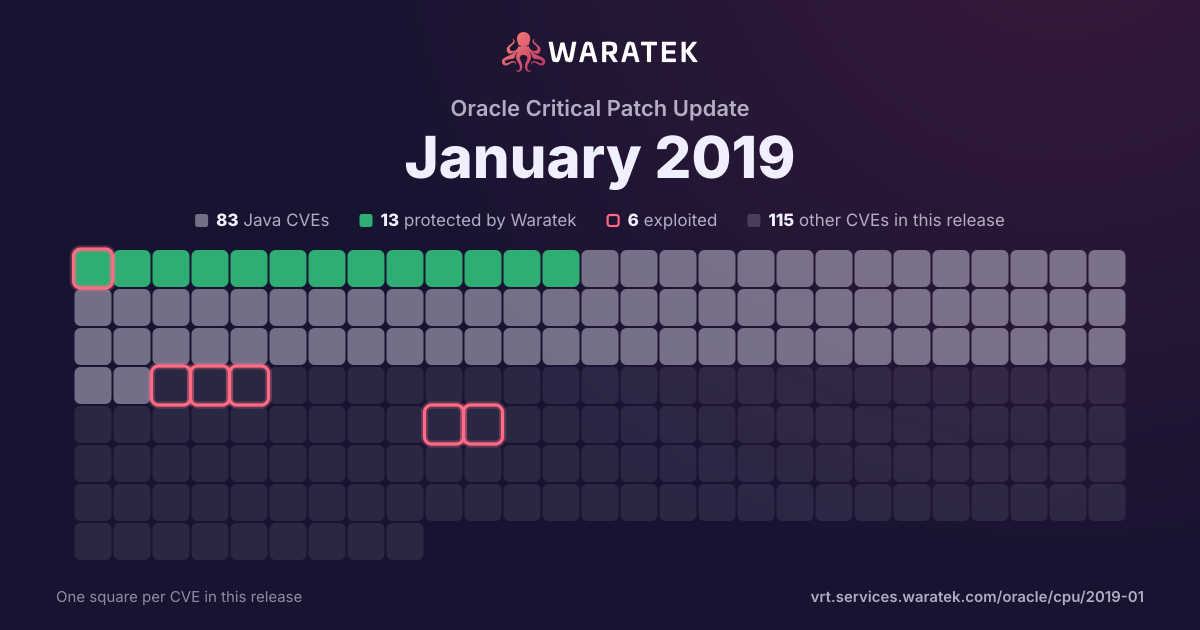
By status
13Protected by Waratek1Mitigation candidate69No exploit published34Outside Waratek scope81Not applicable
6Exploited, marked by the ring
No exploit published. For 67 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 2 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
2
66.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
33.3%
blocked by ARMR today
2
66.7%
partly blocked
0
0.0%
not blocked
1
33.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
100.0%
split by
peak 1 / month
Jul 16Aug 16Sep 16Oct 16Nov 16Dec 16Jan 17Feb 17Mar 17Apr 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-8965 | Critical | 2017-04-06 | No exploit published | No public exploit | Rogue Wave JViews before 8.8 patch 21 and 8.9 before patch 1 allows remote attackers to execute arbitrary Java code that exists in the classpath, such as test code or administration code. The issue exists because the ilog.views.faces.IlvFacesController servlet in jviews-framework-all.jar does not require explicit configuration of servlets that can be called. |
| CVE-2016-1000031 | Critical | 2016-10-25 | Protected by Waratek | No public exploit | Apache Commons FileUpload before 1.3.3 DiskFileItem File Manipulation Remote Code Execution |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |