
Oracle Critical Patch Update October 2018
Released October 2018 · Oracle's advisory ↗ · ← Critical Patch Update, July 2018 · Critical Patch Update, January 2019 →
226 CVEs in this release, one square each
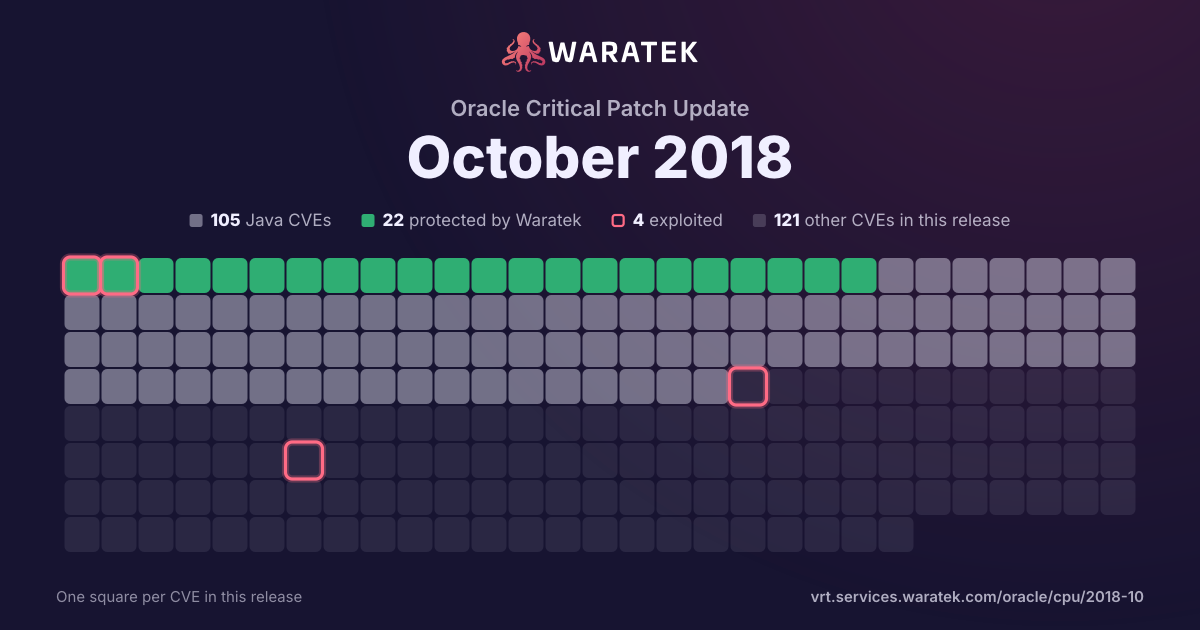
By status
22Protected by Waratek2Mitigation candidate81No exploit published46Outside Waratek scope75Not applicable
4Exploited, marked by the ring
No exploit published. For 81 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 1 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
3matches
1in Waratek scope33.3%
1protected33.3%
0exploited0.0%
0CISA KEV0.0%
1public PoC33.3%
1EPSS ≥ 0.533.3%
Protected by Waratek
1
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
33.3%
Not applicable
1
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
33.3%
partly blocked
0
0.0%
not blocked
2
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
33.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
66.7%
split by
peak 1 / month
Aug 141
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Sep 140
Oct 140
Nov 140
Dec 140
Jan 151
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Feb 150
Mar 150
Apr 150
May 150
Jun 150
Jul 150
Aug 150
Sep 150
Oct 151
Not applicable1
Medium1
not blocked1
No public exploit1
Aug 14Oct 14Dec 14Feb 15Apr 15Jun 15Aug 15Oct 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-6937 | Medium | 2015-10-19 | Not applicable | No public exploit | The __rds_conn_create function in net/rds/connection.c in the Linux kernel through 4.2.3 allows local users to cause a denial of service (NULL pointer dereference and system crash) or possibly have unspecified other impact by using a socket that was not properly bound. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-3490 | High | 2014-08-19 | Protected by Waratek | No public exploit | RESTEasy 2.3.1 before 2.3.8.SP2 and 3.x before 3.0.9, as used in Red Hat JBoss Enterprise Application Platform (EAP) 6.3.0, does not disable external entities when the resteasy.document.expand.entity.references parameter is set to false, which allows remote attackers to read arbitrary files and have other unspecified impact via unspecified vectors, related to an XML External Entity (XXE) issue. NOTE: this vulnerability exists because of an incomplete fix for CVE-2012-0818. |