
Oracle Critical Patch Update October 2018
Released October 2018 · Oracle's advisory ↗ · ← Critical Patch Update, July 2018 · Critical Patch Update, January 2019 →
226 CVEs in this release, one square each
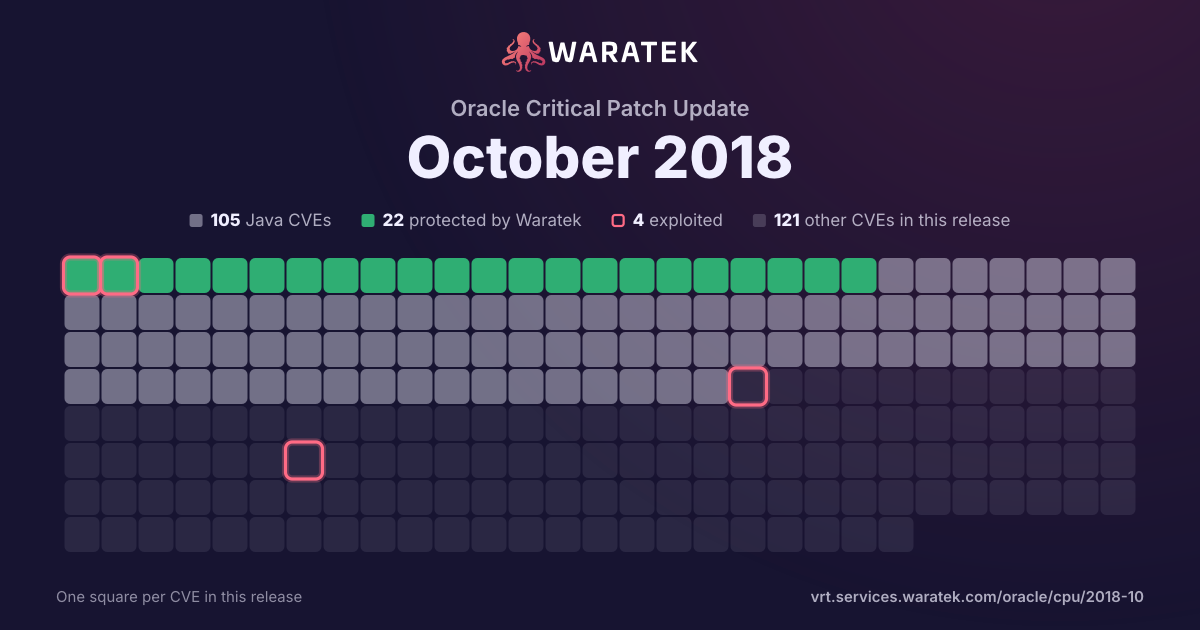
By status
24Protected by Waratek4Mitigation candidate84No exploit published8Outside Waratek scope106Not applicable
4Exploited, marked by the ring
No exploit published. For 82 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 0 protected · 1 exploited · 0 CISA KEV · 3 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
50.0%
No exploit published
3
50.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
6
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 3 / quarter
Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17Q1 18Q2 18
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2018-8014 | Critical | 2018-05-16 | No exploit published | No public exploit | The defaults settings for the CORS filter provided in Apache Tomcat 9.0.0.M1 to 9.0.8, 8.5.0 to 8.5.31, 8.0.0.RC1 to 8.0.52, 7.0.41 to 7.0.88 are insecure and enable 'supportsCredentials' for all origins. It is expected that users of the CORS filter will have configured it appropriately for their environment rather than using it in the default configuration. Therefore, it is expected that most users will not be impacted by this issue. |
| CVE-2018-1258 | High | 2018-05-11 | No exploit published | No public exploit | Spring Framework version 5.0.5 when used in combination with any versions of Spring Security contains an authorization bypass when using method security. An unauthorized malicious user can gain unauthorized access to methods that should be restricted. |
| CVE-2018-1305 | Medium | 2018-02-23 | Mitigation candidate | Proof of concept only | Security constraints defined by annotations of Servlets in Apache Tomcat 9.0.0.M1 to 9.0.4, 8.5.0 to 8.5.27, 8.0.0.RC1 to 8.0.49 and 7.0.0 to 7.0.84 were only applied once a Servlet had been loaded. Because security constraints defined in this way apply to the URL pattern and any URLs below that point, it was possible - depending on the order Servlets were loaded - for some security constraints not to be applied. This could have exposed resources to users who were not authorised to access them. |
| CVE-2015-9251 | Medium | 2018-01-18 | Mitigation candidate | Exploited | jQuery before 3.0.0 is vulnerable to Cross-site Scripting (XSS) attacks when a cross-domain Ajax request is performed without the dataType option, causing text/javascript responses to be executed. |
| CVE-2017-5715 | Medium | 2018-01-04 | Mitigation candidate | Working exploit published | Systems with microprocessors utilizing speculative execution and indirect branch prediction may allow unauthorized disclosure of information to an attacker with local user access via a side-channel analysis. |
| CVE-2016-0635 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |