
Oracle Critical Patch Update July 2018
Released July 2018 · Oracle's advisory ↗ · ← Critical Patch Update, April 2018 · Critical Patch Update, October 2018 →
247 CVEs in this release, one square each
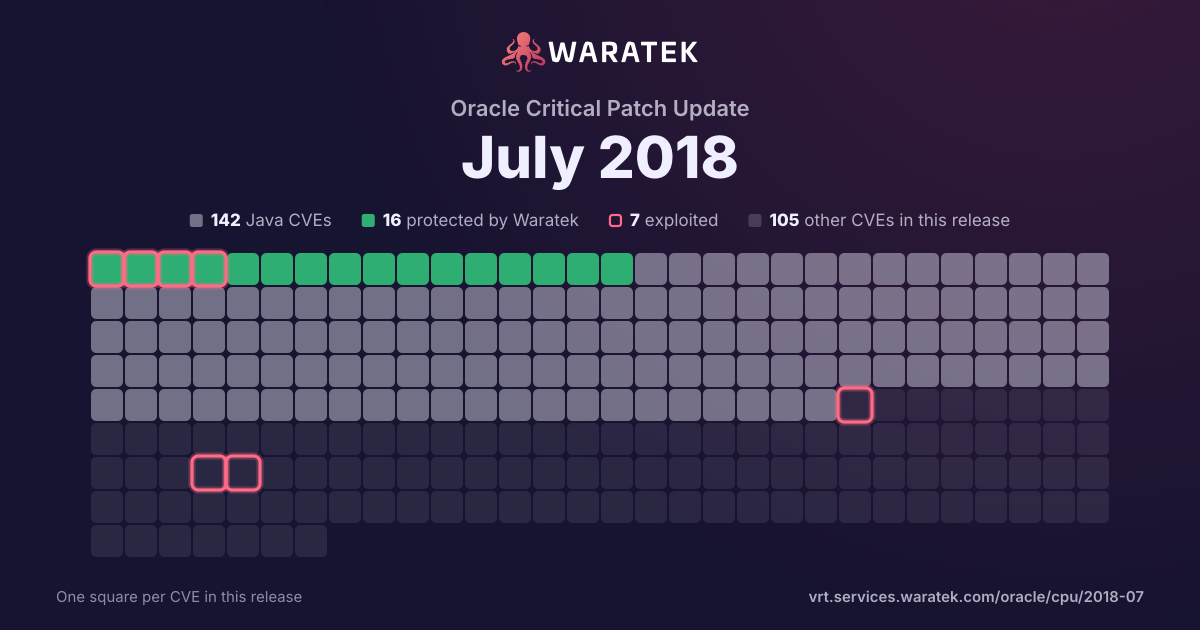
By status
16Protected by Waratek126No exploit published41Outside Waratek scope64Not applicable
7Exploited, marked by the ring
No exploit published. For 125 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 in Waratek scope · 2 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
4matches
2in Waratek scope50.0%
2protected50.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC25.0%
1EPSS ≥ 0.525.0%
Protected by Waratek
2
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
25.0%
Not applicable
1
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
50.0%
partly blocked
0
0.0%
not blocked
2
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
25.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
3
75.0%
split by
peak 1 / month
May 161
Not applicable1
Critical1
not blocked1
No public exploit1
Jun 160
Jul 160
Aug 160
Sep 160
Oct 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Nov 160
Dec 160
Jan 170
Feb 170
Mar 170
Apr 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
May 171
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
May 16Jul 16Sep 16Nov 16Jan 17Mar 17May 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-9843 | Critical | 2017-05-23 | Outside Waratek scope | No public exploit | The crc32_big function in crc32.c in zlib 1.2.8 might allow context-dependent attackers to have unspecified impact via vectors involving big-endian CRC calculation. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |
| CVE-2016-2099 | Critical | 2016-05-13 | Not applicable | No public exploit | Use-after-free vulnerability in validators/DTD/DTDScanner.cpp in Apache Xerces C++ 3.1.3 and earlier allows context-dependent attackers to have unspecified impact via an invalid character in an XML document. |