
Oracle Critical Patch Update April 2018
Released April 2018 · Oracle's advisory ↗ · ← Critical Patch Update, January 2018 · Critical Patch Update, July 2018 →
165 CVEs in this release, one square each
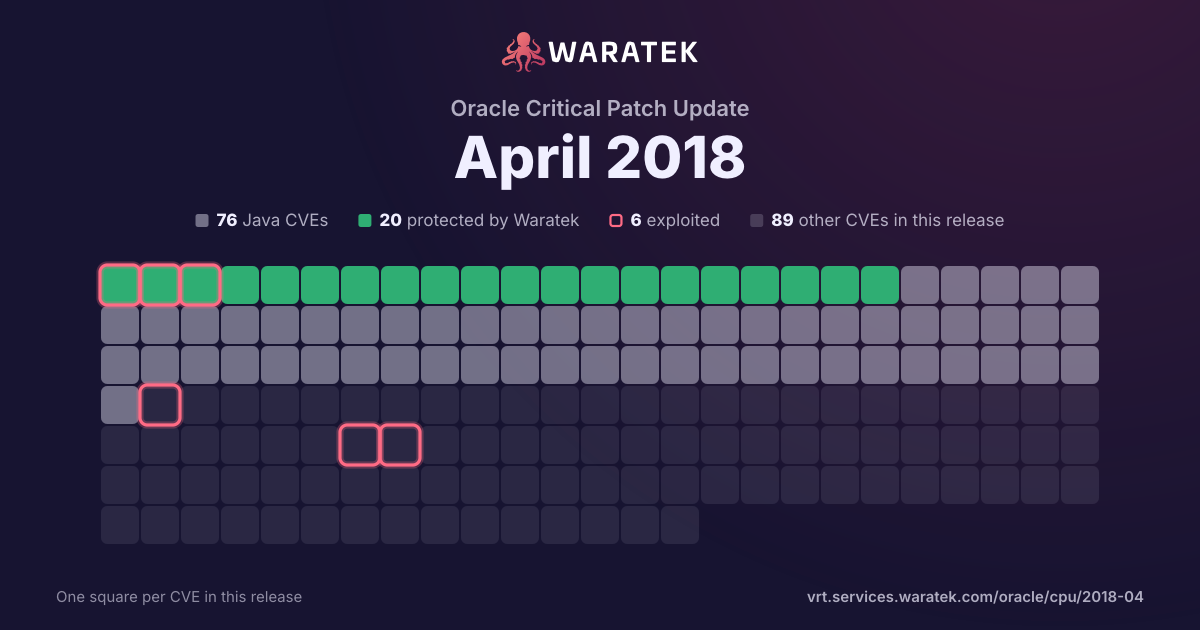
By status
20Protected by Waratek2Mitigation candidate54No exploit published30Outside Waratek scope59Not applicable
6Exploited, marked by the ring
No exploit published. For 52 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 4 protected · 2 exploited · 1 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
Protected by Waratek
5
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
4
80.0%
partly blocked
1
20.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
40.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
40.0%
split by
peak 1 / month
Oct 161
Protected by Waratek1
Critical1
blocked by ARMR today1
No public exploit1
Nov 160
Dec 161
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Jan 170
Feb 170
Mar 170
Apr 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Working exploit published1
May 170
Jun 170
Jul 170
Aug 170
Sep 170
Oct 171
Protected by Waratek1
High1
partly blocked1
Exploited1
Nov 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Nov 16Jan 17Mar 17May 17Jul 17Sep 17Nov 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2017-12617 | High | 2017-10-04 | Protected by Waratek | Exploited | When running Apache Tomcat versions 9.0.0.M1 to 9.0.0, 8.5.0 to 8.5.22, 8.0.0.RC1 to 8.0.46 and 7.0.0 to 7.0.81 with HTTP PUTs enabled (e.g. via setting the readonly initialisation parameter of the Default servlet to false) it was possible to upload a JSP file to the server via a specially crafted request. This JSP could then be requested and any code it contained would be executed by the server. |
| CVE-2017-5645 | Critical | 2017-04-17 | Protected by Waratek | Working exploit published | In Apache Log4j 2.x before 2.8.2, when using the TCP socket server or UDP socket server to receive serialized log events from another application, a specially crafted binary payload can be sent that, when deserialized, can execute arbitrary code. |
| CVE-2016-9878 | High | 2016-12-29 | Protected by Waratek | No public exploit | An issue was discovered in Pivotal Spring Framework before 3.2.18, 4.2.x before 4.2.9, and 4.3.x before 4.3.5. Paths provided to the ResourceServlet were not properly sanitized and as a result exposed to directory traversal attacks. |
| CVE-2016-5019 | Critical | 2016-10-03 | Protected by Waratek | No public exploit | CoreResponseStateManager in Apache MyFaces Trinidad 1.0.0 through 1.0.13, 1.2.x before 1.2.15, 2.0.x before 2.0.2, and 2.1.x before 2.1.2 might allow attackers to conduct deserialization attacks via a crafted serialized view state string. |