
Oracle Critical Patch Update January 2018
Released January 2018 · Oracle's advisory ↗ · ← Critical Patch Update, October 2017 · Critical Patch Update, April 2018 →
197 CVEs in this release, one square each
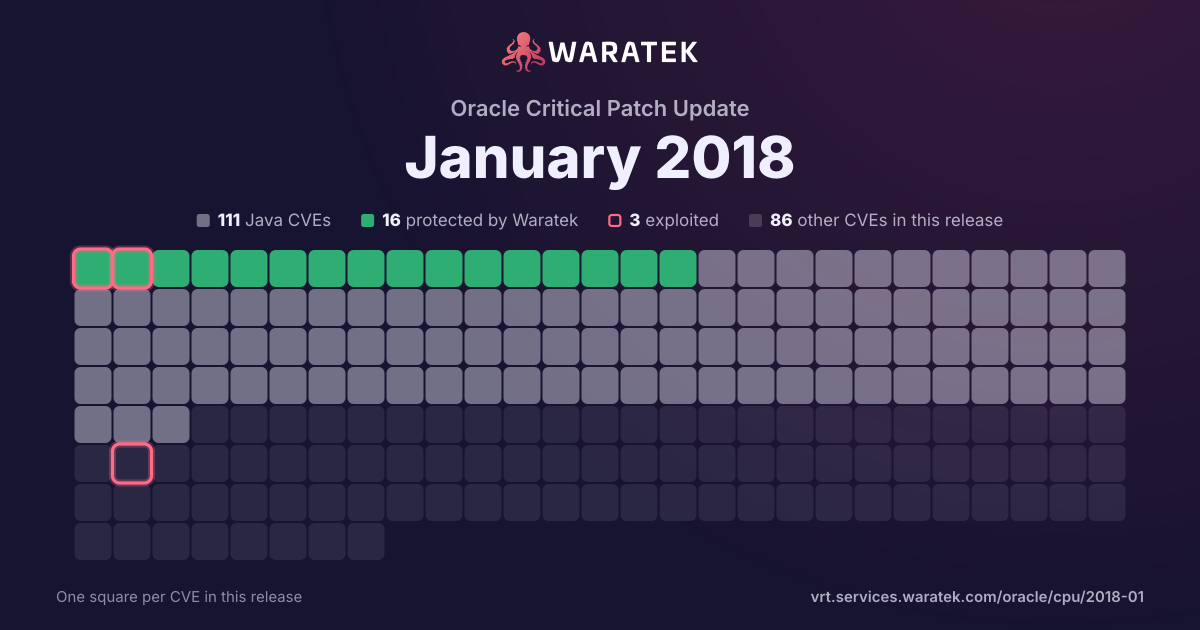
By status
16Protected by Waratek1Mitigation candidate94No exploit published25Outside Waratek scope61Not applicable
3Exploited, marked by the ring
No exploit published. For 94 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 2 in Waratek scope · 2 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
8matches
2in Waratek scope25.0%
2protected25.0%
1exploited12.5%
0CISA KEV0.0%
2public PoC25.0%
2EPSS ≥ 0.525.0%
Protected by Waratek
2
25.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
37.5%
Not applicable
3
37.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
25.0%
partly blocked
0
0.0%
not blocked
6
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
12.5%
Working exploit published
1
12.5%
Proof of concept only
0
0.0%
Forecast only
1
12.5%
No public exploit
5
62.5%
split by
peak 3 / month
Jul 163
Protected by Waratek1
Outside Waratek scope2
High3
blocked by ARMR today1
not blocked2
Forecast only1
No public exploit2
Aug 160
Sep 161
Not applicable1
High1
not blocked1
No public exploit1
Oct 160
Nov 160
Dec 161
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Jan 170
Feb 170
Mar 170
Apr 170
May 170
Jun 171
Outside Waratek scope1
High1
not blocked1
No public exploit1
Jul 170
Aug 170
Sep 172
Not applicable2
High2
not blocked2
Exploited1
Working exploit published1
Jul 16Sep 16Nov 16Jan 17Mar 17May 17Jul 17Sep 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-9798 | High | 2017-09-18 | Not applicable | Exploited | Apache httpd allows remote attackers to read secret data from process memory if the Limit directive can be set in a user's .htaccess file, or if httpd.conf has certain misconfigurations, aka Optionsbleed. This affects the Apache HTTP Server through 2.2.34 and 2.4.x through 2.4.27. The attacker sends an unauthenticated OPTIONS HTTP request when attempting to read secret data. This is a use-after-free issue and thus secret data is not always sent, and the specific data depends on many factors including configuration. Exploitation with .htaccess can be blocked with a patch to the ap_limit_section function in server/core.c. |
| CVE-2017-0781 | High | 2017-09-14 | Not applicable | Working exploit published | A remote code execution vulnerability in the Android system (bluetooth). Product: Android. Versions: 4.4.4, 5.0.2, 5.1.1, 6.0, 6.0.1, 7.0, 7.1.1, 7.1.2, 8.0. Android ID: A-63146105. |
| CVE-2017-5664 | High | 2017-06-06 | Outside Waratek scope | No public exploit | The error page mechanism of the Java Servlet Specification requires that, when an error occurs and an error page is configured for the error that occurred, the original request and response are forwarded to the error page. This means that the request is presented to the error page with the original HTTP method. If the error page is a static file, expected behaviour is to serve content of the file as if processing a GET request, regardless of the actual HTTP method. The Default Servlet in Apache Tomcat 9.0.0.M1 to 9.0.0.M20, 8.5.0 to 8.5.14, 8.0.0.RC1 to 8.0.43 and 7.0.0 to 7.0.77 did not do this. Depending on the original request this could lead to unexpected and undesirable results for static error pages including, if the DefaultServlet is configured to permit writes, the replacement or removal of the custom error page. Notes for other user provided error pages: (1) Unless explicitly coded otherwise, JSPs ignore the HTTP method. JSPs used as error pages must must ensure that they handle any error dispatch as a GET request, regardless of the actual method. (2) By default, the response generated by a Servlet does depend on the HTTP method. Custom Servlets used as error pages must ensure that they handle any error dispatch as a GET request, regardless of the actual method. |
| CVE-2016-9878 | High | 2016-12-29 | Protected by Waratek | No public exploit | An issue was discovered in Pivotal Spring Framework before 3.2.18, 4.2.x before 4.2.9, and 4.3.x before 4.3.5. Paths provided to the ResourceServlet were not properly sanitized and as a result exposed to directory traversal attacks. |
| CVE-2016-2179 | High | 2016-09-16 | Not applicable | No public exploit | The DTLS implementation in OpenSSL before 1.1.0 does not properly restrict the lifetime of queue entries associated with unused out-of-order messages, which allows remote attackers to cause a denial of service (memory consumption) by maintaining many crafted DTLS sessions simultaneously, related to d1_lib.c, statem_dtls.c, statem_lib.c, and statem_srvr.c. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5385 | High | 2016-07-19 | Outside Waratek scope | Forecast only | PHP through 7.0.8 does not attempt to address RFC 3875 section 4.1.18 namespace conflicts and therefore does not protect applications from the presence of untrusted client data in the HTTP_PROXY environment variable, which might allow remote attackers to redirect an application's outbound HTTP traffic to an arbitrary proxy server via a crafted Proxy header in an HTTP request, as demonstrated by (1) an application that makes a getenv('HTTP_PROXY') call or (2) a CGI configuration of PHP, aka an "httpoxy" issue. |
| CVE-2016-1182 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 does not properly restrict the Validator configuration, which allows remote attackers to conduct cross-site scripting (XSS) attacks or cause a denial of service via crafted input, a related issue to CVE-2015-0899. |