
Oracle Critical Patch Update January 2018
Released January 2018 · Oracle's advisory ↗ · ← Critical Patch Update, October 2017 · Critical Patch Update, April 2018 →
197 CVEs in this release, one square each
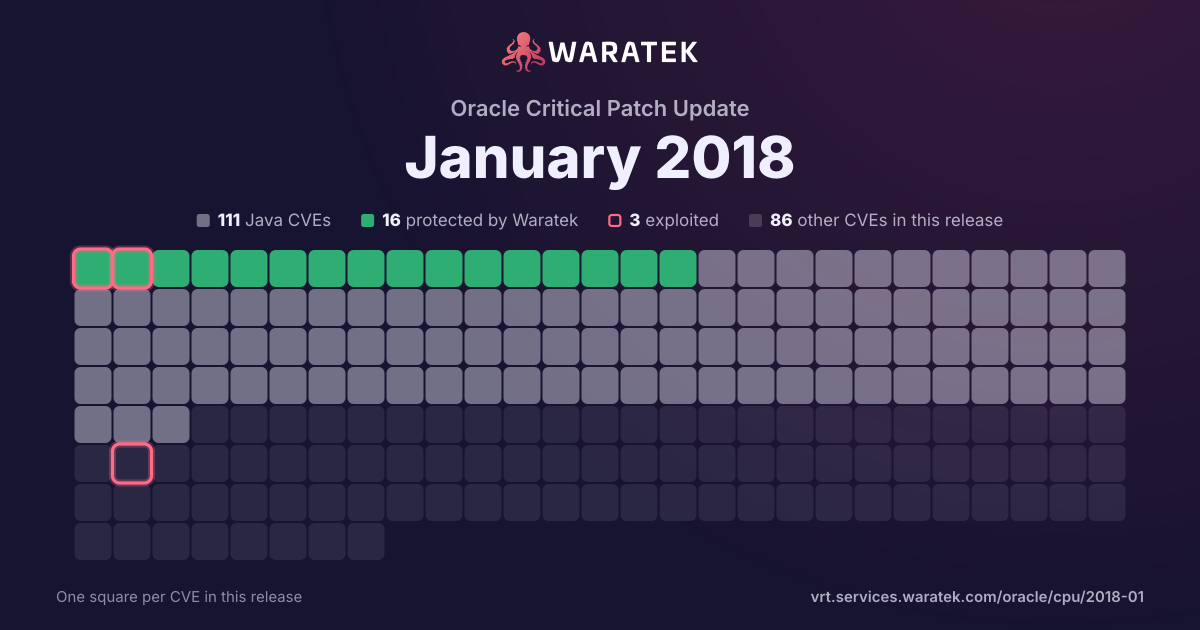
By status
16Protected by Waratek1Mitigation candidate94No exploit published25Outside Waratek scope61Not applicable
3Exploited, marked by the ring
No exploit published. For 94 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 2 EPSS ≥ 0.5
5matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC20.0%
2EPSS ≥ 0.540.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
60.0%
Not applicable
2
40.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
5
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
1
20.0%
No public exploit
3
60.0%
split by
peak 1 / quarter
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 130
Q3 130
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 150
Q2 150
Q3 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 151
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q1 161
Not applicable1
Medium1
not blocked1
No public exploit1
Q2 161
Not applicable1
Medium1
not blocked1
Working exploit published1
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-0704 | Medium | 2016-03-02 | Not applicable | No public exploit | An oracle protection mechanism in the get_client_master_key function in s2_srvr.c in the SSLv2 implementation in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a overwrites incorrect MASTER-KEY bytes during use of export cipher suites, which makes it easier for remote attackers to decrypt TLS ciphertext data by leveraging a Bleichenbacher RSA padding oracle, a related issue to CVE-2016-0800. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |
| CVE-2013-2566 | Medium | 2013-03-15 | Outside Waratek scope | Forecast only | The RC4 algorithm, as used in the TLS protocol and SSL protocol, has many single-byte biases, which makes it easier for remote attackers to conduct plaintext-recovery attacks via statistical analysis of ciphertext in a large number of sessions that use the same plaintext. |