
Oracle Critical Patch Update October 2017
Released October 2017 · Oracle's advisory ↗ · ← Critical Patch Update, July 2017 · Critical Patch Update, January 2018 →
225 CVEs in this release, one square each
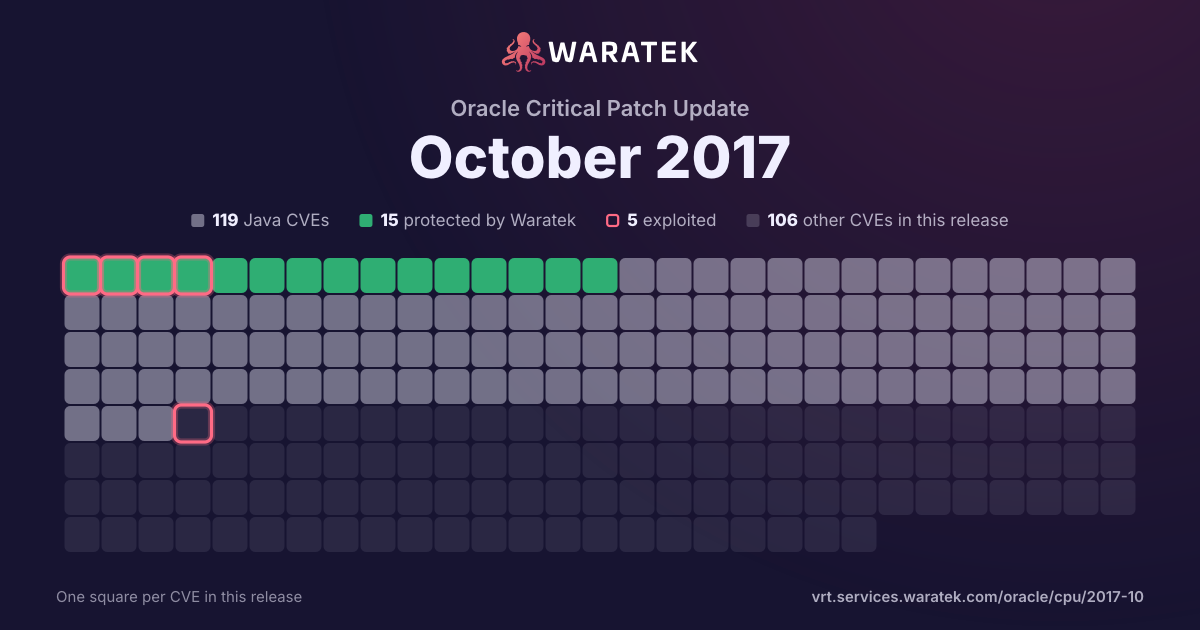
By status
15Protected by Waratek3Mitigation candidate101No exploit published34Outside Waratek scope72Not applicable
5Exploited, marked by the ring
No exploit published. For 100 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 22 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 2 EPSS ≥ 0.5
22matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
2EPSS ≥ 0.59.1%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
22
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
22
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
2
9.1%
No public exploit
20
90.9%
split by
peak 12 / quarter
Q2 131
Not applicable1
High1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 140
Q2 140
Q3 141
Not applicable1
High1
not blocked1
No public exploit1
Q4 140
Q1 150
Q2 150
Q3 150
Q4 150
Q1 160
Q2 162
Not applicable2
High2
not blocked2
No public exploit2
Q3 163
Not applicable3
High3
not blocked3
Forecast only1
No public exploit2
Q4 160
Q1 170
Q2 173
Not applicable3
High3
not blocked3
Forecast only1
No public exploit2
Q3 170
Q4 1712
Not applicable12
High12
not blocked12
No public exploit12
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5706 | High | 2017-11-21 | Not applicable | No public exploit | Multiple buffer overflows in kernel in Intel Server Platform Services Firmware 4.0 allow attacker with local access to the system to execute arbitrary code. |
| CVE-2017-3588 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Solaris Cluster component of Oracle Sun Systems Products Suite (subcomponent: HA for MySQL). Supported versions that are affected are 3.3 and 4.3. Easily exploitable vulnerability allows unauthenticated attacker with logon to the infrastructure where Solaris Cluster executes to compromise Solaris Cluster. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Solaris Cluster accessible data as well as unauthorized access to critical data or complete access to all Solaris Cluster accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Solaris Cluster. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:N/UI:R/S:U/C:H/I:H/A:L). |
| CVE-2017-10408 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). The supported version that is affected is Prior to 5.1.30. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox as well as unauthorized update, insert or delete access to some of Oracle VM VirtualBox accessible data and unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:H). |
| CVE-2017-10407 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). The supported version that is affected is Prior to 5.1.30. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox as well as unauthorized update, insert or delete access to some of Oracle VM VirtualBox accessible data and unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:H). |
| CVE-2017-10401 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Hospitality Cruise Materials Management component of Oracle Hospitality Applications (subcomponent: MMSUpdater). The supported version that is affected is 7.30.564.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Hospitality Cruise Materials Management executes to compromise Oracle Hospitality Cruise Materials Management. While the vulnerability is in Oracle Hospitality Cruise Materials Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Hospitality Cruise Materials Management accessible data as well as unauthorized read access to a subset of Oracle Hospitality Cruise Materials Management accessible data and unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Hospitality Cruise Materials Management. CVSS 3.0 Base Score 8.7 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:L/I:H/A:H). |
| CVE-2017-10398 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Hospitality Cruise Fleet Management component of Oracle Hospitality Applications (subcomponent: BaseMasterPage). The supported version that is affected is 9.0.2.0. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle Hospitality Cruise Fleet Management executes to compromise Oracle Hospitality Cruise Fleet Management. While the vulnerability is in Oracle Hospitality Cruise Fleet Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Hospitality Cruise Fleet Management accessible data as well as unauthorized access to critical data or complete access to all Oracle Hospitality Cruise Fleet Management accessible data. CVSS 3.0 Base Score 8.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:C/C:H/I:H/A:N). |
| CVE-2017-10392 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle VM VirtualBox component of Oracle Virtualization (subcomponent: Core). The supported version that is affected is Prior to 5.1.30. Easily exploitable vulnerability allows high privileged attacker with logon to the infrastructure where Oracle VM VirtualBox executes to compromise Oracle VM VirtualBox. While the vulnerability is in Oracle VM VirtualBox, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle VM VirtualBox as well as unauthorized update, insert or delete access to some of Oracle VM VirtualBox accessible data and unauthorized read access to a subset of Oracle VM VirtualBox accessible data. CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:H/UI:N/S:C/C:L/I:L/A:H). |
| CVE-2017-10353 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Hospitality Hotel Mobile component of Oracle Hospitality Applications (subcomponent: Suite8/RESTAPI). The supported version that is affected is 1.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Hotel Mobile. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality Hotel Mobile accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Hospitality Hotel Mobile. CVSS 3.0 Base Score 7.1 (Confidentiality and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:L). |
| CVE-2017-10265 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Integrated Lights Out Manager (ILOM) component of Oracle Sun Systems Products Suite (subcomponent: System Management). The supported version that is affected is Prior to 3.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Integrated Lights Out Manager (ILOM). Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Integrated Lights Out Manager (ILOM) accessible data as well as unauthorized read access to a subset of Oracle Integrated Lights Out Manager (ILOM) accessible data and unauthorized ability to cause a partial denial of service (partial DOS) of Oracle Integrated Lights Out Manager (ILOM). CVSS 3.0 Base Score 7.3 (Confidentiality, Integrity and Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:L). |
| CVE-2017-10260 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Integrated Lights Out Manager (ILOM) component of Oracle Sun Systems Products Suite (subcomponent: System Management). The supported version that is affected is Prior to 3.2.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Integrated Lights Out Manager (ILOM). Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Integrated Lights Out Manager (ILOM). CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-10155 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the MySQL Server component of Oracle MySQL (subcomponent: Server: Pluggable Auth). Supported versions that are affected are 5.6.37 and earlier and 5.7.19 and earlier. Easily exploitable vulnerability allows unauthenticated attacker with network access via multiple protocols to compromise MySQL Server. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of MySQL Server. CVSS 3.0 Base Score 7.5 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H). |
| CVE-2017-10050 | High | 2017-10-19 | Not applicable | No public exploit | Vulnerability in the Oracle Hospitality Suite8 component of Oracle Hospitality Applications (subcomponent: WebConnect). Supported versions that are affected are 8.10.1 and 8.10.2. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Hospitality Suite8. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Hospitality Suite8, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Hospitality Suite8 accessible data as well as unauthorized update, insert or delete access to some of Oracle Hospitality Suite8 accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-3733 | High | 2017-05-04 | Not applicable | No public exploit | During a renegotiation handshake if the Encrypt-Then-Mac extension is negotiated where it was not in the original handshake (or vice-versa) then this can cause OpenSSL 1.1.0 before 1.1.0e to crash (dependent on ciphersuite). Both clients and servers are affected. |
| CVE-2017-3731 | High | 2017-05-04 | Not applicable | Forecast only | If an SSL/TLS server or client is running on a 32-bit host, and a specific cipher is being used, then a truncated packet can cause that server or client to perform an out-of-bounds read, usually resulting in a crash. For OpenSSL 1.1.0, the crash can be triggered when using CHACHA20/POLY1305; users should upgrade to 1.1.0d. For Openssl 1.0.2, the crash can be triggered when using RC4-MD5; users who have not disabled that algorithm should update to 1.0.2k. |
| CVE-2017-5662 | High | 2017-04-18 | Not applicable | No public exploit | In Apache Batik before 1.9, files lying on the filesystem of the server which uses batik can be revealed to arbitrary users who send maliciously formed SVG files. The file types that can be shown depend on the user context in which the exploitable application is running. If the user is root a full compromise of the server - including confidential or sensitive files - would be possible. XXE can also be used to attack the availability of the server via denial of service as the references within a xml document can trivially trigger an amplification attack. |
| CVE-2016-7052 | High | 2016-09-26 | Not applicable | No public exploit | crypto/x509/x509_vfy.c in OpenSSL 1.0.2i allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) by triggering a CRL operation. |
| CVE-2016-6304 | High | 2016-09-26 | Not applicable | Forecast only | Multiple memory leaks in t1_lib.c in OpenSSL before 1.0.1u, 1.0.2 before 1.0.2i, and 1.1.0 before 1.1.0a allow remote attackers to cause a denial of service (memory consumption) via large OCSP Status Request extensions. |
| CVE-2016-3506 | High | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the JDBC component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2; the Oracle Retail Xstore Point of Service 5.5, 6.0, 6.5, 7.0, 7.1, 15.0, and 16.0; the Oracle Retail Warehouse Management System 14.04, 14.1.3, and 15.0.1; the Oracle Retail Workforce Management 1.60.7, and 1.64.0; the Oracle Retail Clearance Optimization Engine 13.4; the Oracle Retail Markdown Optimization 13.4 and 14.0; and Oracle Retail Merchandising System 16.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-2834 | High | 2016-06-13 | Not applicable | No public exploit | Mozilla Network Security Services (NSS) before 3.23, as used in Mozilla Firefox before 47.0, allows remote attackers to cause a denial of service (memory corruption and application crash) or possibly have unspecified other impact via unknown vectors. |
| CVE-2016-2381 | High | 2016-04-08 | Not applicable | No public exploit | Perl might allow context-dependent attackers to bypass the taint protection mechanism in a child process via duplicate environment variables in envp. |
| CVE-2014-4345 | High | 2014-08-14 | Not applicable | No public exploit | Off-by-one error in the krb5_encode_krbsecretkey function in plugins/kdb/ldap/libkdb_ldap/ldap_principal2.c in the LDAP KDB module in kadmind in MIT Kerberos 5 (aka krb5) 1.6.x through 1.11.x before 1.11.6 and 1.12.x before 1.12.2 allows remote authenticated users to cause a denial of service (buffer overflow) or possibly execute arbitrary code via a series of "cpw -keepold" commands. |
| CVE-2013-1903 | High | 2013-04-04 | Not applicable | No public exploit | PostgreSQL, possibly 9.2.x before 9.2.4, 9.1.x before 9.1.9, 9.0.x before 9.0.13, 8.4.x before 8.4.17, and 8.3.x before 8.3.23 incorrectly provides the superuser password to scripts related to "graphical installers for Linux and Mac OS X," which has unspecified impact and attack vectors. |