
Oracle Critical Patch Update October 2017
Released October 2017 · Oracle's advisory ↗ · ← Critical Patch Update, July 2017 · Critical Patch Update, January 2018 →
225 CVEs in this release, one square each
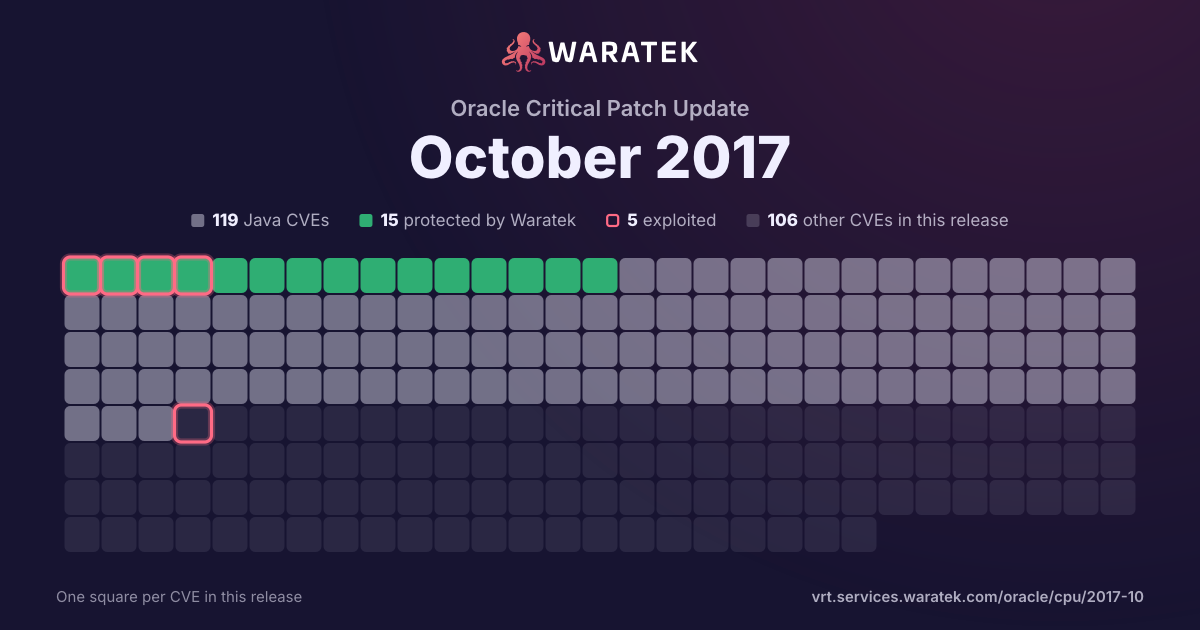
By status
15Protected by Waratek3Mitigation candidate101No exploit published34Outside Waratek scope72Not applicable
5Exploited, marked by the ring
No exploit published. For 100 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 2 in Waratek scope · 2 protected · 2 exploited · 0 CISA KEV · 3 public PoC · 3 EPSS ≥ 0.5
8matches
2in Waratek scope25.0%
2protected25.0%
2exploited25.0%
0CISA KEV0.0%
3public PoC37.5%
3EPSS ≥ 0.537.5%
Protected by Waratek
2
25.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
37.5%
Not applicable
3
37.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
25.0%
partly blocked
0
0.0%
not blocked
6
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
25.0%
Working exploit published
1
12.5%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
62.5%
split by
peak 3 / quarter
Q2 131
Not applicable1
High1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 140
Q2 143
Protected by Waratek2
Outside Waratek scope1
High3
blocked by ARMR today2
not blocked1
Exploited2
No public exploit1
Q3 141
Not applicable1
High1
not blocked1
No public exploit1
Q4 140
Q1 151
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q2 150
Q3 150
Q4 150
Q1 161
Outside Waratek scope1
High1
not blocked1
No public exploit1
Q2 161
Not applicable1
High1
not blocked1
No public exploit1
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-2381 | High | 2016-04-08 | Not applicable | No public exploit | Perl might allow context-dependent attackers to bypass the taint protection mechanism in a child process via duplicate environment variables in envp. |
| CVE-2016-0714 | High | 2016-02-25 | Outside Waratek scope | No public exploit | The session-persistence implementation in Apache Tomcat 6.x before 6.0.45, 7.x before 7.0.68, 8.x before 8.0.31, and 9.x before 9.0.0.M2 mishandles session attributes, which allows remote authenticated users to bypass intended SecurityManager restrictions and execute arbitrary code in a privileged context via a web application that places a crafted object in a session. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2014-4345 | High | 2014-08-14 | Not applicable | No public exploit | Off-by-one error in the krb5_encode_krbsecretkey function in plugins/kdb/ldap/libkdb_ldap/ldap_principal2.c in the LDAP KDB module in kadmind in MIT Kerberos 5 (aka krb5) 1.6.x through 1.11.x before 1.11.6 and 1.12.x before 1.12.2 allows remote authenticated users to cause a denial of service (buffer overflow) or possibly execute arbitrary code via a series of "cpw -keepold" commands. |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2014-0107 | High | 2014-04-15 | Protected by Waratek | No public exploit | The TransformerFactory in Apache Xalan-Java before 2.7.2 does not properly restrict access to certain properties when FEATURE_SECURE_PROCESSING is enabled, which allows remote attackers to bypass expected restrictions and load arbitrary classes or access external resources via a crafted (1) xalan:content-header, (2) xalan:entities, (3) xslt:content-header, or (4) xslt:entities property, or a Java property that is bound to the XSLT 1.0 system-property function. |
| CVE-2013-1903 | High | 2013-04-04 | Not applicable | No public exploit | PostgreSQL, possibly 9.2.x before 9.2.4, 9.1.x before 9.1.9, 9.0.x before 9.0.13, 8.4.x before 8.4.17, and 8.3.x before 8.3.23 incorrectly provides the superuser password to scripts related to "graphical installers for Linux and Mac OS X," which has unspecified impact and attack vectors. |