
Oracle Critical Patch Update October 2017
Released October 2017 · Oracle's advisory ↗ · ← Critical Patch Update, July 2017 · Critical Patch Update, January 2018 →
225 CVEs in this release, one square each
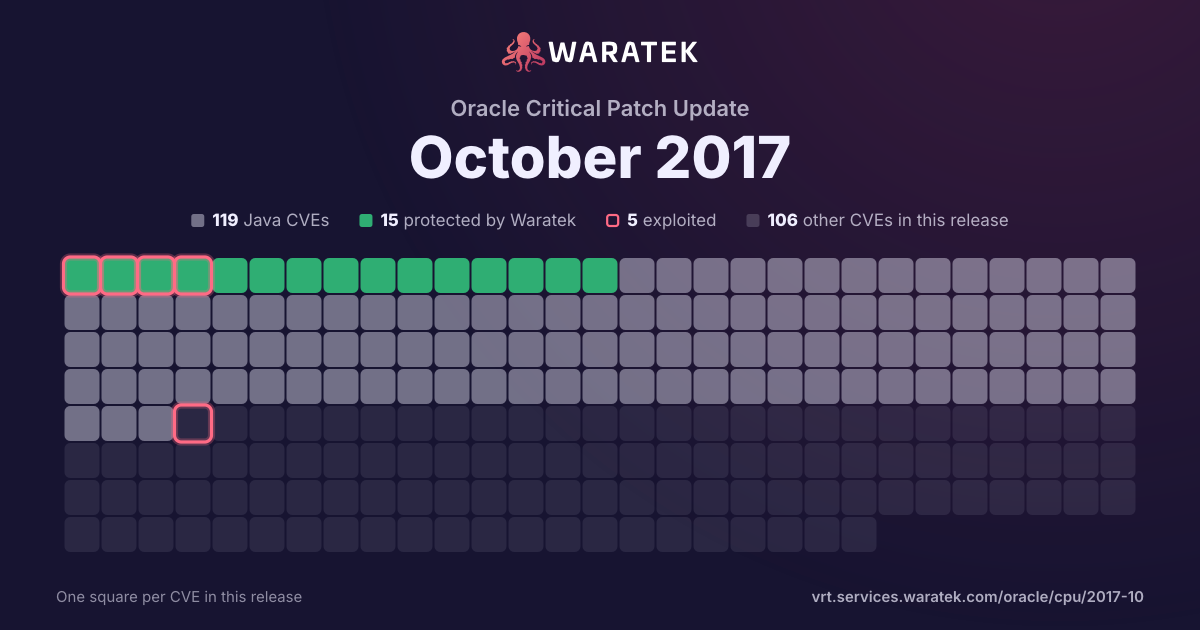
By status
15Protected by Waratek3Mitigation candidate101No exploit published34Outside Waratek scope72Not applicable
5Exploited, marked by the ring
No exploit published. For 100 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 1 in Waratek scope · 1 protected · 1 exploited · 1 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
2matches
1in Waratek scope50.0%
1protected50.0%
1exploited50.0%
1CISA KEV50.0%
1public PoC50.0%
1EPSS ≥ 0.550.0%
Protected by Waratek
1
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
1
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
50.0%
partly blocked
0
0.0%
not blocked
1
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
50.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
50.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-5662 | High | 2017-04-18 | Not applicable | No public exploit | In Apache Batik before 1.9, files lying on the filesystem of the server which uses batik can be revealed to arbitrary users who send maliciously formed SVG files. The file types that can be shown depend on the user context in which the exploitable application is running. If the user is root a full compromise of the server - including confidential or sensitive files - would be possible. XXE can also be used to attack the availability of the server via denial of service as the references within a xml document can trivially trigger an amplification attack. |
| CVE-2016-8735 | Critical | 2017-04-06 | Protected by Waratek | Exploited | Remote code execution is possible with Apache Tomcat before 6.0.48, 7.x before 7.0.73, 8.x before 8.0.39, 8.5.x before 8.5.7, and 9.x before 9.0.0.M12 if JmxRemoteLifecycleListener is used and an attacker can reach JMX ports. The issue exists because this listener wasn't updated for consistency with the CVE-2016-3427 Oracle patch that affected credential types. |