
Oracle Critical Patch Update July 2017
Released July 2017 · Oracle's advisory ↗ · ← Critical Patch Update, April 2017 · Critical Patch Update, October 2017 →
272 CVEs in this release, one square each
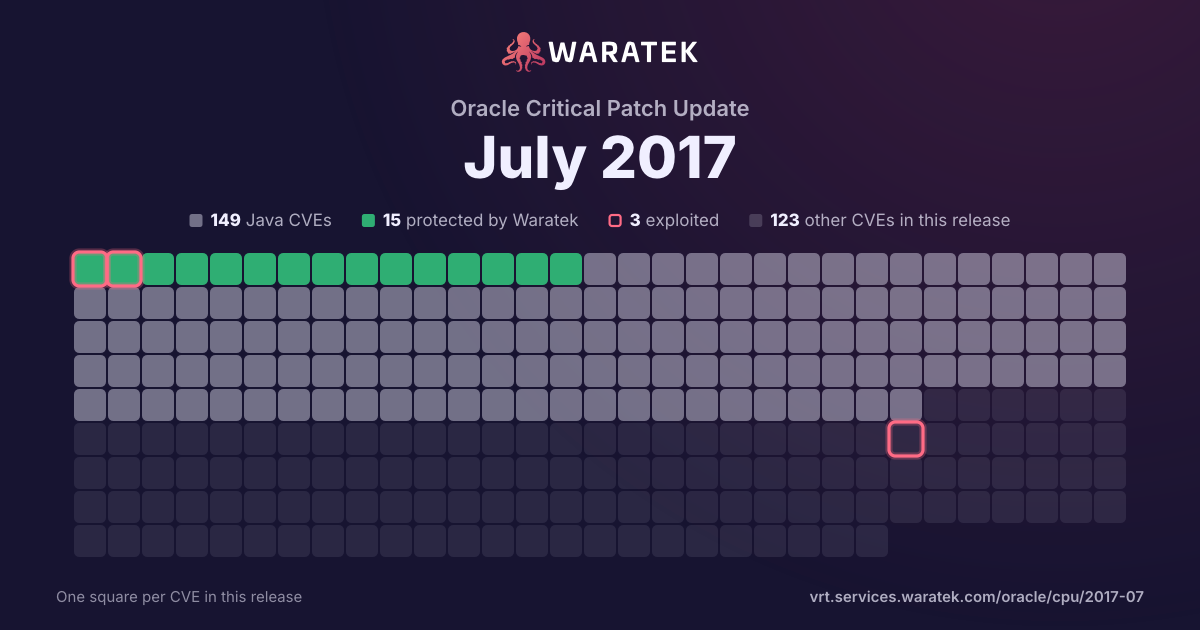
By status
15Protected by Waratek3Mitigation candidate131No exploit published30Outside Waratek scope93Not applicable
3Exploited, marked by the ring
No exploit published. For 126 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 143 matches · 11 protected · 2 exploited · 1 CISA KEV · 5 public PoC · 2 EPSS ≥ 0.5
Protected by Waratek
11
7.7%
Rule in development
0
0.0%
Mitigation candidate
3
2.1%
No exploit published
129
90.2%
blocked by ARMR today
11
7.7%
partly blocked
0
0.0%
not blocked
132
92.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
1.4%
Working exploit published
3
2.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
138
96.5%
split by
peak 139 / month
Mar 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Apr 172
No exploit published2
Critical1
High1
not blocked2
No public exploit2
May 170
Jun 170
Jul 170
Aug 17139
Protected by Waratek9
Mitigation candidate3
No exploit published127
Critical2
High45
Medium90
Low2
blocked by ARMR today9
not blocked130
Working exploit published3
No public exploit136
Sep 170
Oct 170
Nov 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Mar 17Apr 17May 17Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2017-10058 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Business Intelligence Enterprise Edition component of Oracle Fusion Middleware (subcomponent: Analytics Web Administration). Supported versions that are affected are 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0. Easily exploitable vulnerability allows high privileged attacker with network access via HTTP to compromise Oracle Business Intelligence Enterprise Edition. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Business Intelligence Enterprise Edition, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Business Intelligence Enterprise Edition accessible data as well as unauthorized read access to a subset of Oracle Business Intelligence Enterprise Edition accessible data. CVSS 3.0 Base Score 6.9 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:H/UI:R/S:C/C:L/I:H/A:N). |
| CVE-2017-10057 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PRTL Interaction Hub component of Oracle PeopleSoft Products (subcomponent: Discussion Forum). The supported version that is affected is 9.1.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PRTL Interaction Hub. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PRTL Interaction Hub, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PRTL Interaction Hub accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PRTL Interaction Hub accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10052 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: PCMServlet). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Agile PLM accessible data as well as unauthorized read access to a subset of Oracle Agile PLM accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10049 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Siebel Core CRM component of Oracle Siebel CRM (subcomponent: Search). Supported versions that are affected are 16.0 and 17.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Siebel Core CRM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Siebel Core CRM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Siebel Core CRM accessible data as well as unauthorized read access to a subset of Siebel Core CRM accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10048 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Enterprise Repository component of Oracle Fusion Middleware (subcomponent: Web Interface). Supported versions that are affected are 11.1.1.7.0 and 12.1.3.0.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Enterprise Repository. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Enterprise Repository, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Enterprise Repository accessible data as well as unauthorized update, insert or delete access to some of Oracle Enterprise Repository accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10047 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the MICROS BellaVita component of Oracle Hospitality Applications (subcomponent: Interface). The supported version that is affected is 2.7.x. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise MICROS BellaVita. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of MICROS BellaVita accessible data as well as unauthorized read access to a subset of MICROS BellaVita accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10046 | Medium | 2017-08-08 | Mitigation candidate | Working exploit published | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 8.3, 8.4, 15.1, 15.2 and 16.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Primavera P6 Enterprise Project Portfolio Management, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Primavera P6 Enterprise Project Portfolio Management accessible data as well as unauthorized read access to a subset of Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10045 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Integration Broker). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 5.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:H/PR:N/UI:R/S:U/C:H/I:N/A:N). |
| CVE-2017-10044 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Hospitality Applications (subcomponent: Reporting). Supported versions that are affected are 8.5.1 and 9.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Hospitality Reporting and Analytics accessible data as well as unauthorized read access to a subset of Oracle Hospitality Reporting and Analytics accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10043 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). Supported versions that are affected are 11.1.1.7.0 and 11.1.1.9.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10041 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Web Server). Supported versions that are affected are 11.1.1.9.0, 12.2.1.1.0 and 12.2.1.2.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 7.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10040 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle WebCenter Content component of Oracle Fusion Middleware (subcomponent: Content Server). Supported versions that are affected are 11.1.1.9.0 and 12.2.1.1.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle WebCenter Content. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle WebCenter Content, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle WebCenter Content accessible data as well as unauthorized read access to a subset of Oracle WebCenter Content accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:H/A:N). |
| CVE-2017-10039 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Agile PLM component of Oracle Supply Chain Products Suite (subcomponent: Web Client). Supported versions that are affected are 9.3.5 and 9.3.6. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Agile PLM. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle Agile PLM, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Agile PLM accessible data. CVSS 3.0 Base Score 6.8 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:H/I:N/A:N). |
| CVE-2017-10038 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Primavera P6 Enterprise Project Portfolio Management component of Oracle Primavera Products Suite (subcomponent: Web Access). Supported versions that are affected are 15.1, 15.2, 16.1 and 16.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Primavera P6 Enterprise Project Portfolio Management. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Primavera P6 Enterprise Project Portfolio Management accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10035 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Web Server). Supported versions that are affected are 11.1.1.7.0 and 11.1.1.9.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10032 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Transportation Management component of Oracle Supply Chain Products Suite (subcomponent: Access Control List). Supported versions that are affected are 6.3.4.1, 6.3.5.1, 6.3.6.1, 6.3.7.1, 6.4.0, 6.4.1 and 6.4.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Transportation Management. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Transportation Management accessible data as well as unauthorized read access to a subset of Oracle Transportation Management accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10031 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Communications Convergence component of Oracle Communications Applications (subcomponent: Mail Proxy (dojo)). Supported versions that are affected are 3.0 and 3.0.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Communications Convergence. While the vulnerability is in Oracle Communications Convergence, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle Communications Convergence accessible data as well as unauthorized read access to a subset of Oracle Communications Convergence accessible data. CVSS 3.0 Base Score 7.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:C/C:L/I:L/A:N). |
| CVE-2017-10030 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Web Server). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10029 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Web Server). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10028 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Web Server). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10027 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Fluid Homepage & Navigation). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10025 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: BI Publisher Security). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:L/A:N). |
| CVE-2017-10024 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the BI Publisher component of Oracle Fusion Middleware (subcomponent: Layout Tools). The supported version that is affected is 11.1.1.7.0. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise BI Publisher. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in BI Publisher, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all BI Publisher accessible data as well as unauthorized update, insert or delete access to some of BI Publisher accessible data. CVSS 3.0 Base Score 8.2 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:L/A:N). |
| CVE-2017-10023 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Operations). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10022 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Operations). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10021 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: PIA Search). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10020 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Updates Change Assistant). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise PeopleTools executes to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10019 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Integration Broker). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 7.4 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:H/I:N/A:N). |
| CVE-2017-10018 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise FSCM component of Oracle PeopleSoft Products (subcomponent: Strategic Sourcing). The supported version that is affected is 9.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise PeopleSoft Enterprise FSCM. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise FSCM accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-10017 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Workcenter). Supported versions that are affected are 8.54 and 8.55. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise PeopleSoft Enterprise PeopleTools. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in PeopleSoft Enterprise PeopleTools, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of PeopleSoft Enterprise PeopleTools accessible data as well as unauthorized read access to a subset of PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10015 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the PeopleSoft Enterprise PeopleTools component of Oracle PeopleSoft Products (subcomponent: Application Designer). Supported versions that are affected are 8.54 and 8.55. Difficult to exploit vulnerability allows low privileged attacker with logon to the infrastructure where PeopleSoft Enterprise PeopleTools executes to compromise PeopleSoft Enterprise PeopleTools. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all PeopleSoft Enterprise PeopleTools accessible data. CVSS 3.0 Base Score 4.7 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:H/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10012 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Operations). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 5.4 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:L/A:N). |
| CVE-2017-10011 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with logon to the infrastructure where Oracle FLEXCUBE Private Banking executes to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 5.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:L/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N). |
| CVE-2017-10010 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: FileUploads). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks require human interaction from a person other than the attacker. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.6 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:R/S:U/C:L/I:L/A:N). |
| CVE-2017-10009 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.3 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:L/A:N). |
| CVE-2017-10008 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10007 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 4.3 (Confidentiality impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:L/I:N/A:N). |
| CVE-2017-10006 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 6.5 (Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:U/C:N/I:H/A:N). |
| CVE-2017-10005 | Medium | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle FLEXCUBE Private Banking component of Oracle Financial Services Applications (subcomponent: Miscellaneous). Supported versions that are affected are 2.0.0, 2.0.1, 2.2.0 and 12.0.1. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle FLEXCUBE Private Banking. Successful attacks require human interaction from a person other than the attacker and while the vulnerability is in Oracle FLEXCUBE Private Banking, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized update, insert or delete access to some of Oracle FLEXCUBE Private Banking accessible data as well as unauthorized read access to a subset of Oracle FLEXCUBE Private Banking accessible data. CVSS 3.0 Base Score 6.1 (Confidentiality and Integrity impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N). |
| CVE-2017-10000 | High | 2017-08-08 | No exploit published | No public exploit | Vulnerability in the Oracle Hospitality Reporting and Analytics component of Oracle Hospitality Applications (subcomponent: Reporting). Supported versions that are affected are 8.5.1 and 9.0.0. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Hospitality Reporting and Analytics. While the vulnerability is in Oracle Hospitality Reporting and Analytics, attacks may significantly impact additional products. Successful attacks of this vulnerability can result in unauthorized ability to cause a hang or frequently repeatable crash (complete DOS) of Oracle Hospitality Reporting and Analytics. CVSS 3.0 Base Score 7.7 (Availability impacts). CVSS Vector: (CVSS:3.0/AV:N/AC:L/PR:L/UI:N/S:C/C:N/I:N/A:H). |
| CVE-2017-5651 | Critical | 2017-04-17 | No exploit published | No public exploit | In Apache Tomcat 9.0.0.M1 to 9.0.0.M18 and 8.5.0 to 8.5.12, the refactoring of the HTTP connectors introduced a regression in the send file processing. If the send file processing completed quickly, it was possible for the Processor to be added to the processor cache twice. This could result in the same Processor being used for multiple requests which in turn could lead to unexpected errors and/or response mix-up. |
| CVE-2017-5647 | High | 2017-04-17 | No exploit published | No public exploit | A bug in the handling of the pipelined requests in Apache Tomcat 9.0.0.M1 to 9.0.0.M18, 8.5.0 to 8.5.12, 8.0.0.RC1 to 8.0.42, 7.0.0 to 7.0.76, and 6.0.0 to 6.0.52, when send file was used, results in the pipelined request being lost when send file processing of the previous request completed. This could result in responses appearing to be sent for the wrong request. For example, a user agent that sent requests A, B and C could see the correct response for request A, the response for request C for request B and no response for request C. |
| CVE-2017-5638 | Critical | 2017-03-11 | Protected by Waratek | Exploited | The Jakarta Multipart parser in Apache Struts 2 2.3.x before 2.3.32 and 2.5.x before 2.5.10.1 has incorrect exception handling and error-message generation during file-upload attempts, which allows remote attackers to execute arbitrary commands via a crafted Content-Type, Content-Disposition, or Content-Length HTTP header, as exploited in the wild in March 2017 with a Content-Type header containing a #cmd= string. |