
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
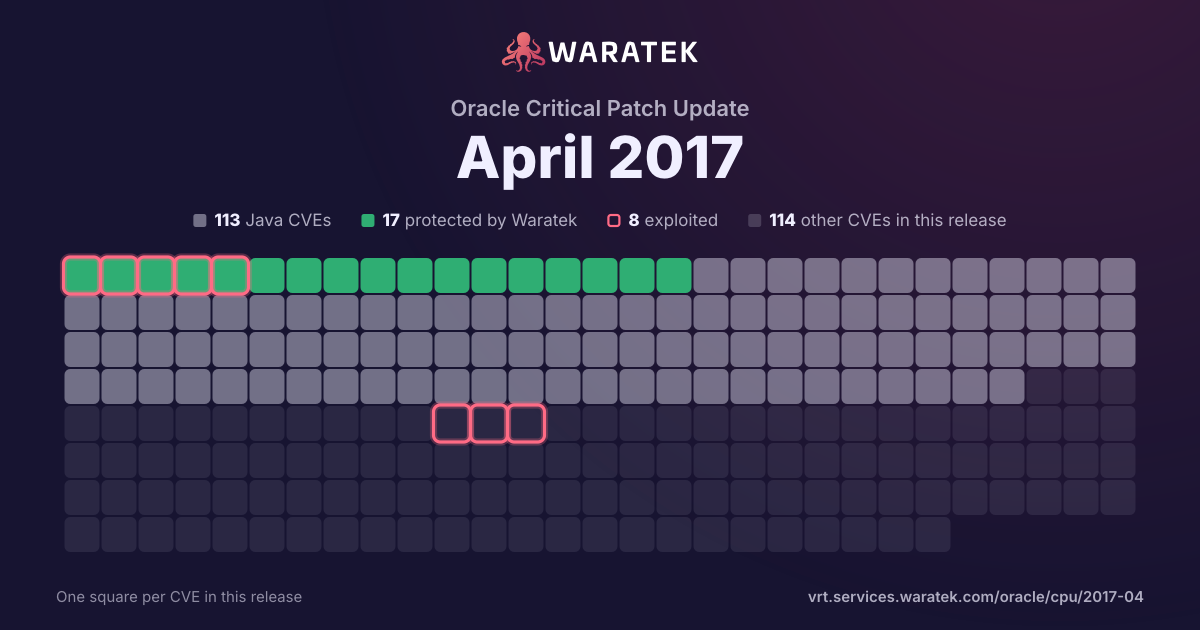
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 8 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
8matches
0in Waratek scope0.0%
0protected0.0%
1exploited12.5%
0CISA KEV0.0%
2public PoC25.0%
1EPSS ≥ 0.512.5%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
8
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
8
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
12.5%
Working exploit published
1
12.5%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
6
75.0%
split by
peak 3 / year
20091
Not applicable1
Critical1
not blocked1
Working exploit published1
20100
20110
20122
Not applicable2
High1
Medium1
not blocked2
No public exploit2
20132
Not applicable2
High1
Medium1
not blocked2
No public exploit2
20140
20153
Not applicable3
High1
Medium2
not blocked3
Exploited1
No public exploit2
2009201020112012201320142015
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-5252 | High | 2015-12-29 | Not applicable | No public exploit | vfs.c in smbd in Samba 3.x and 4.x before 4.1.22, 4.2.x before 4.2.7, and 4.3.x before 4.3.3, when share names with certain substring relationships exist, allows remote attackers to bypass intended file-access restrictions via a symlink that points outside of a share. |
| CVE-2015-3237 | Medium | 2015-06-22 | Not applicable | No public exploit | The smb_request_state function in cURL and libcurl 7.40.0 through 7.42.1 allows remote SMB servers to obtain sensitive information from memory or cause a denial of service (out-of-bounds read and crash) via crafted length and offset values. |
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |
| CVE-2013-5209 | High | 2013-08-29 | Not applicable | No public exploit | The sctp_send_initiate_ack function in sys/netinet/sctp_output.c in the SCTP implementation in the kernel in FreeBSD 8.3 through 9.2-PRERELEASE does not properly initialize the state-cookie data structure, which allows remote attackers to obtain sensitive information from kernel stack memory by reading packet data in INIT-ACK chunks. |
| CVE-2013-1982 | Medium | 2013-06-15 | Not applicable | No public exploit | Multiple integer overflows in X.org libXext 1.3.1 and earlier allow X servers to trigger allocation of insufficient memory and a buffer overflow via vectors related to the (1) XcupGetReservedColormapEntries, (2) XcupStoreColors, (3) XdbeGetVisualInfo, (4) XeviGetVisualInfo, (5) XShapeGetRectangles, and (6) XSyncListSystemCounters functions. |
| CVE-2012-5881 | Medium | 2012-11-16 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in the Flash component infrastructure in YUI 2.4.0 through 2.9.0 allows remote attackers to inject arbitrary web script or HTML via vectors related to charts.swf, a similar issue to CVE-2010-4207. |
| CVE-2012-0920 | High | 2012-06-05 | Not applicable | No public exploit | Use-after-free vulnerability in Dropbear SSH Server 0.52 through 2012.54, when command restriction and public key authentication are enabled, allows remote authenticated users to execute arbitrary code and bypass command restrictions via multiple crafted command requests, related to "channels concurrency." |
| CVE-2004-2761 | Critical | 2009-01-05 | Not applicable | Working exploit published | The MD5 Message-Digest Algorithm is not collision resistant, which makes it easier for context-dependent attackers to conduct spoofing attacks, as demonstrated by attacks on the use of MD5 in the signature algorithm of an X.509 certificate. |