
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
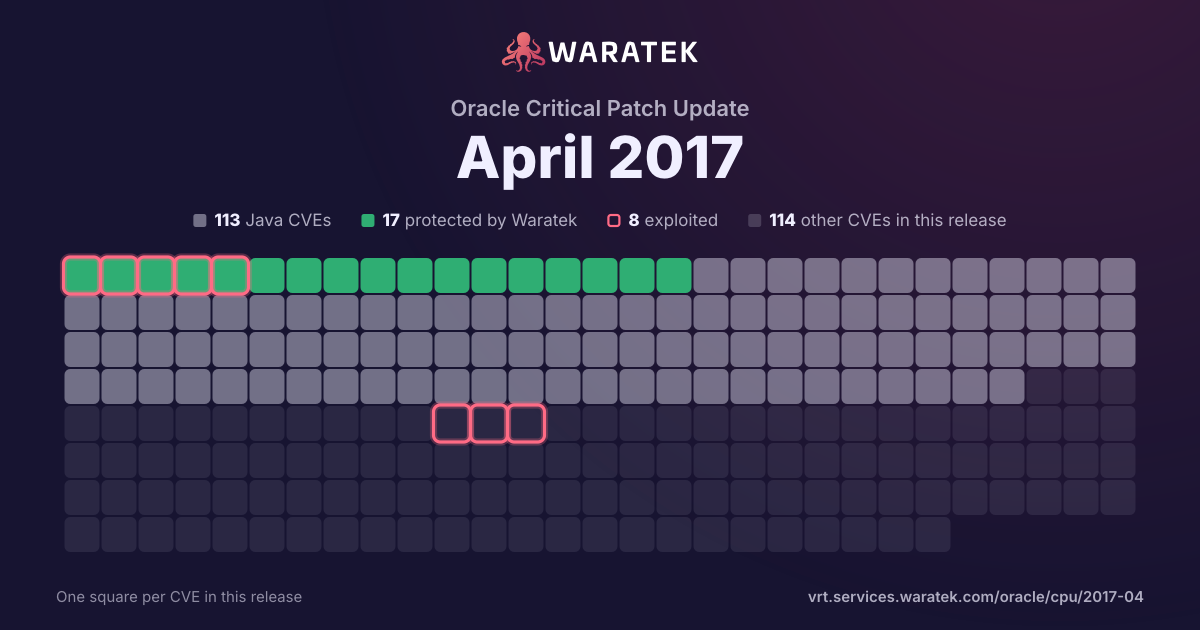
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 1 in Waratek scope · 1 protected · 1 exploited · 0 CISA KEV · 1 public PoC · 2 EPSS ≥ 0.5
5matches
1in Waratek scope20.0%
1protected20.0%
1exploited20.0%
0CISA KEV0.0%
1public PoC20.0%
2EPSS ≥ 0.540.0%
Protected by Waratek
1
20.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
2
40.0%
Not applicable
2
40.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
20.0%
partly blocked
0
0.0%
not blocked
4
80.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
20.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
1
20.0%
No public exploit
3
60.0%
split by
peak 2 / month
May 172
Not applicable2
High1
Medium1
not blocked2
Forecast only1
No public exploit1
Jun 170
Jul 171
Outside Waratek scope1
High1
not blocked1
No public exploit1
Aug 171
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Sep 170
Oct 170
Nov 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
May 17Jun 17Jul 17Aug 17Sep 17Oct 17Nov 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-0762 | Medium | 2017-08-10 | Outside Waratek scope | No public exploit | The Realm implementations in Apache Tomcat versions 9.0.0.M1 to 9.0.0.M9, 8.5.0 to 8.5.4, 8.0.0.RC1 to 8.0.36, 7.0.0 to 7.0.70 and 6.0.0 to 6.0.45 did not process the supplied password if the supplied user name did not exist. This made a timing attack possible to determine valid user names. Note that the default configuration includes the LockOutRealm which makes exploitation of this vulnerability harder. |
| CVE-2016-8743 | High | 2017-07-27 | Outside Waratek scope | No public exploit | Apache HTTP Server, in all releases prior to 2.2.32 and 2.4.25, was liberal in the whitespace accepted from requests and sent in response lines and headers. Accepting these different behaviors represented a security concern when httpd participates in any chain of proxies or interacts with back-end application servers, either through mod_proxy or using conventional CGI mechanisms, and may result in request smuggling, response splitting and cache pollution. |
| CVE-2017-3732 | Medium | 2017-05-04 | Not applicable | No public exploit | There is a carry propagating bug in the x86_64 Montgomery squaring procedure in OpenSSL 1.0.2 before 1.0.2k and 1.1.0 before 1.1.0d. No EC algorithms are affected. Analysis suggests that attacks against RSA and DSA as a result of this defect would be very difficult to perform and are not believed likely. Attacks against DH are considered just feasible (although very difficult) because most of the work necessary to deduce information about a private key may be performed offline. The amount of resources required for such an attack would be very significant and likely only accessible to a limited number of attackers. An attacker would additionally need online access to an unpatched system using the target private key in a scenario with persistent DH parameters and a private key that is shared between multiple clients. For example this can occur by default in OpenSSL DHE based SSL/TLS ciphersuites. Note: This issue is very similar to CVE-2015-3193 but must be treated as a separate problem. |
| CVE-2017-3731 | High | 2017-05-04 | Not applicable | Forecast only | If an SSL/TLS server or client is running on a 32-bit host, and a specific cipher is being used, then a truncated packet can cause that server or client to perform an out-of-bounds read, usually resulting in a crash. For OpenSSL 1.1.0, the crash can be triggered when using CHACHA20/POLY1305; users should upgrade to 1.1.0d. For Openssl 1.0.2, the crash can be triggered when using RC4-MD5; users who have not disabled that algorithm should update to 1.0.2k. |