
Oracle Critical Patch Update April 2017
Released April 2017 · Oracle's advisory ↗ · ← Critical Patch Update, January 2017 · Critical Patch Update, July 2017 →
227 CVEs in this release, one square each
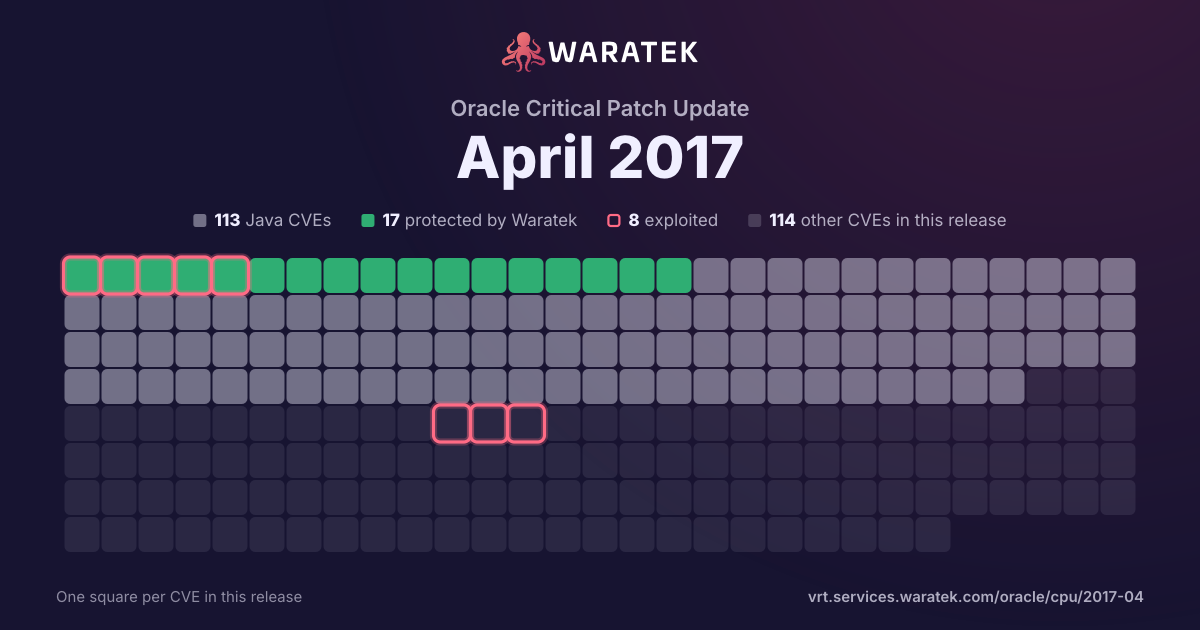
By status
17Protected by Waratek1Mitigation candidate95No exploit published13Outside Waratek scope101Not applicable
8Exploited, marked by the ring
No exploit published. For 93 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 202 matches · 103 in Waratek scope · 8 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
202matches
103in Waratek scope51.0%
8protected4.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
8
4.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
95
47.0%
Outside Waratek scope
12
5.9%
Not applicable
87
43.1%
Withdrawn CVE
0
0.0%
blocked by ARMR today
8
4.0%
partly blocked
0
0.0%
not blocked
194
96.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
202
100.0%
split by
peak 177 / quarter
Q2 121
Not applicable1
High1
not blocked1
No public exploit1
Q3 120
Q4 121
Not applicable1
Medium1
not blocked1
No public exploit1
Q1 130
Q2 131
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 131
Not applicable1
High1
not blocked1
No public exploit1
Q4 130
Q1 140
Q2 140
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 140
Q1 150
Q2 151
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 150
Q4 152
Outside Waratek scope1
Not applicable1
High1
Medium1
not blocked2
No public exploit2
Q1 161
Outside Waratek scope1
High1
not blocked1
No public exploit1
Q2 164
Protected by Waratek1
Not applicable3
Critical1
High2
Medium1
blocked by ARMR today1
not blocked3
No public exploit4
Q3 167
Protected by Waratek1
No exploit published2
Outside Waratek scope1
Not applicable3
Critical3
High4
blocked by ARMR today1
not blocked6
No public exploit7
Q4 162
Protected by Waratek1
Not applicable1
Critical2
blocked by ARMR today1
not blocked1
No public exploit2
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 17177
Protected by Waratek5
No exploit published92
Outside Waratek scope7
Not applicable73
Critical5
High74
Medium80
Low18
blocked by ARMR today5
not blocked172
No public exploit177
Q3 172
Outside Waratek scope2
High1
Medium1
not blocked2
No public exploit2
Q3 12Q1 13Q3 13Q1 14Q3 14Q1 15Q3 15Q1 16Q3 16Q1 17Q3 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2012-5881 | Medium | 2012-11-16 | Not applicable | No public exploit | Cross-site scripting (XSS) vulnerability in the Flash component infrastructure in YUI 2.4.0 through 2.9.0 allows remote attackers to inject arbitrary web script or HTML via vectors related to charts.swf, a similar issue to CVE-2010-4207. |
| CVE-2012-0920 | High | 2012-06-05 | Not applicable | No public exploit | Use-after-free vulnerability in Dropbear SSH Server 0.52 through 2012.54, when command restriction and public key authentication are enabled, allows remote authenticated users to execute arbitrary code and bypass command restrictions via multiple crafted command requests, related to "channels concurrency." |