
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
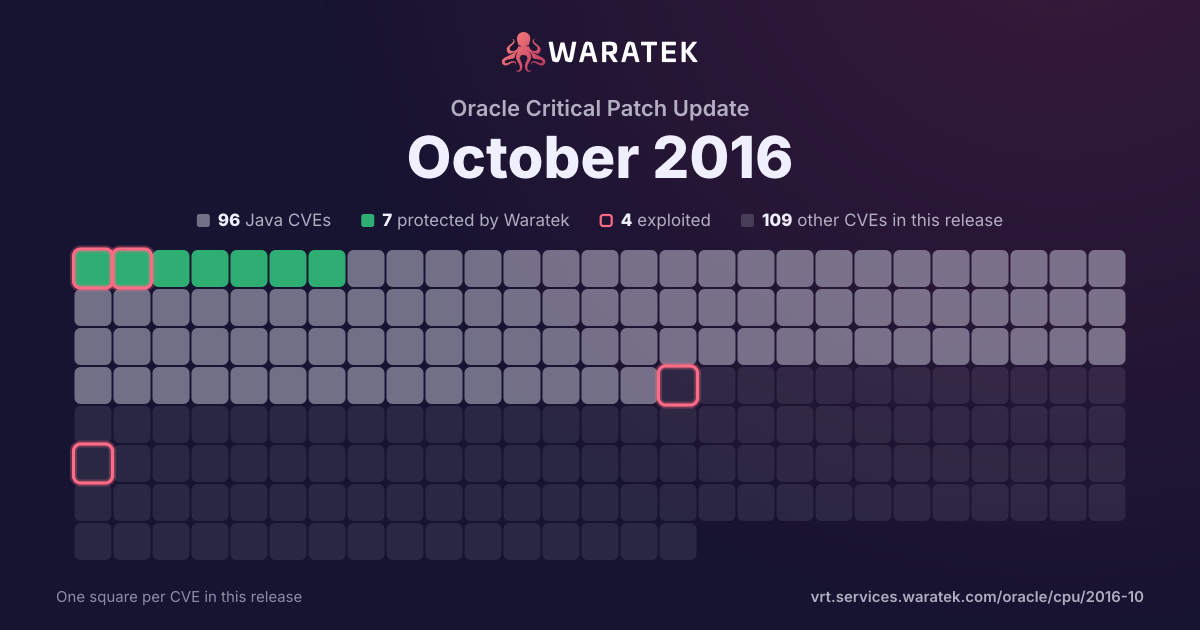
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 170 matches · 88 in Waratek scope · 4 protected · 3 exploited · 1 CISA KEV · 7 public PoC · 5 EPSS ≥ 0.5
170matches
88in Waratek scope51.8%
4protected2.4%
3exploited1.8%
1CISA KEV0.6%
7public PoC4.1%
5EPSS ≥ 0.52.9%
Protected by Waratek
4
2.4%
Rule in development
0
0.0%
Mitigation candidate
1
0.6%
No exploit published
83
48.8%
Outside Waratek scope
17
10.0%
Not applicable
63
37.1%
Withdrawn CVE
2
1.2%
blocked by ARMR today
4
2.4%
partly blocked
0
0.0%
not blocked
166
97.6%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
3
1.8%
Working exploit published
4
2.4%
Proof of concept only
0
0.0%
Forecast only
1
0.6%
No public exploit
162
95.3%
split by
peak 159 / quarter
Q1 161
Outside Waratek scope1
High1
not blocked1
No public exploit1
Q2 163
Protected by Waratek1
Not applicable2
High2
Medium1
blocked by ARMR today1
not blocked2
Exploited1
Working exploit published1
No public exploit1
Q3 165
Protected by Waratek1
Outside Waratek scope1
Not applicable3
Critical1
High4
blocked by ARMR today1
not blocked4
Exploited1
Forecast only1
No public exploit3
Q4 16159
Protected by Waratek1
Mitigation candidate1
No exploit published83
Outside Waratek scope15
Not applicable57
Withdrawn CVE2
Critical10
High45
Medium86
Low16
Unknown2
blocked by ARMR today1
not blocked158
Working exploit published3
No public exploit156
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-5542 | Low | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect integrity via vectors related to Libraries. |
| CVE-2016-5540 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Xstore Payment component in Oracle Retail Applications 1.x allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5539 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Xstore Payment component in Oracle Retail Applications 1.x allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5538 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core, a different vulnerability than CVE-2016-5501. |
| CVE-2016-5537 | Medium | 2016-10-25 | Protected by Waratek | No public exploit | Unspecified vulnerability in the NetBeans component in Oracle Fusion Middleware 8.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the October 2016 CPU. Oracle has not commented on third-party claims that this issue is a directory traversal vulnerability which allows local users with certain permissions to write to arbitrary files and consequently gain privileges via a .. (dot dot) in a archive entry in a ZIP file imported as a project. |
| CVE-2016-5536 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-8281. |
| CVE-2016-5535 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5534 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Apps - Customer Order Management component in Oracle Siebel CRM 16.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5533 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.4, 15.x, and 16.x allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5532 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Shipping Execution component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality via vectors related to Workflow Events. |
| CVE-2016-5531 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS-WebServices. |
| CVE-2016-5530 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5529 and CVE-2016-8293. |
| CVE-2016-5529 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5530 and CVE-2016-8293. |
| CVE-2016-5527 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5524. |
| CVE-2016-5526 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Apache Tomcat. |
| CVE-2016-5525 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 3.3 and 4.3 allows local users to affect integrity via vectors related to Cluster check files. |
| CVE-2016-5524 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5527. |
| CVE-2016-5523 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to AutoVue Java Applet. |
| CVE-2016-5522 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5521 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5512. |
| CVE-2016-5519 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Java Server Faces. |
| CVE-2016-5518 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to webfileservices. |
| CVE-2016-5517 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 allows local users to affect confidentiality via vectors related to AD Utilities. |
| CVE-2016-5516 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Kernel PDB component in Oracle Database Server 12.1.0.2 allows local users to affect availability via unknown vectors. |
| CVE-2016-5515 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to RMIServlet. |
| CVE-2016-5514 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to ExportServlet. |
| CVE-2016-5513 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to File Manager. |
| CVE-2016-5512 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5521. |
| CVE-2016-5511 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 12.2.1.0.0, 12.2.1.1.0, and 12.2.1.2.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2016-5510 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-5508 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Solaris Cluster component in Oracle Sun Systems Products Suite 4.3 allows local users to affect confidentiality via vectors related to Cluster Geo. |
| CVE-2016-5507 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.32 and earlier and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5506 | Low | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Manager component in Oracle Fusion Middleware allows local users to affect confidentiality and integrity via vectors related to App Server. |
| CVE-2016-5505 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Programmable Interface component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows local users to affect confidentiality via unknown vectors. |
| CVE-2016-5504 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Lifecycle Management for Process component in Oracle Supply Chain Products Suite 6.1.0.4, 6.1.1.6, and 6.2.0.0 allows local users to affect confidentiality via vectors related to Supplier Portal. |
| CVE-2016-5503 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality, integrity, and availability via vectors related to Core Services. |
| CVE-2016-5502 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA. |
| CVE-2016-5501 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core, a different vulnerability than CVE-2016-5538. |
| CVE-2016-5500 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to Viewer. |
| CVE-2016-5499 | Low | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows local users to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5498. |
| CVE-2016-5498 | Low | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows local users to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5499. |
| CVE-2016-5497 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5495 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to EUL Code & Schema. |
| CVE-2016-5493 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Private Banking component in Oracle Financial Services Applications 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5492 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality and integrity via vectors related to SMB Users. |
| CVE-2016-5491 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Service Center component in Oracle Commerce 10.0.3.5 and 10.2.0.5 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5490 | Low | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.4.0 allows local users to affect confidentiality via vectors related to INFRA. |
| CVE-2016-5489 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iStore component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via vectors related to Runtime Catalog. |
| CVE-2016-5488 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0 and 12.1.3.0 allows remote attackers to affect availability via vectors related to Web Container, a different vulnerability than CVE-2016-3445. |
| CVE-2016-5487 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5486 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality via vectors related to Core Services. |
| CVE-2016-5482 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Guided Search component in Oracle Commerce 6.2.2, 6.3.0, 6.4.1.2, and 6.5.0 through 6.5.2 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5481 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows remote attackers to affect confidentiality via vectors related to Core Services. |
| CVE-2016-5480 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect integrity via vectors related to Bash. |
| CVE-2016-5479 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, and 12.0.1 allows remote authenticated users to affect confidentiality via vectors related to INFRA. |
| CVE-2016-3562 | Low | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security and SQL*Plus components in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows remote administrators to affect confidentiality via vectors related to DBA. |
| CVE-2016-3551 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Services component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.3.0.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JAXWS Web Services Stack. |
| CVE-2016-3505 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to JavaServer Faces. |
| CVE-2016-3495 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-3492 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-3473 | High | 2016-10-25 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-6304 | High | 2016-09-26 | Not applicable | Forecast only | Multiple memory leaks in t1_lib.c in OpenSSL before 1.0.1u, 1.0.2 before 1.0.2i, and 1.1.0 before 1.1.0a allow remote attackers to cause a denial of service (memory consumption) via large OCSP Status Request extensions. |
| CVE-2016-6662 | Critical | 2016-09-20 | Not applicable | Exploited | Oracle MySQL through 5.5.52, 5.6.x through 5.6.33, and 5.7.x through 5.7.15; MariaDB before 5.5.51, 10.0.x before 10.0.27, and 10.1.x before 10.1.17; and Percona Server before 5.5.51-38.1, 5.6.x before 5.6.32-78.0, and 5.7.x before 5.7.14-7 allow local users to create arbitrary configurations and bypass certain protection mechanisms by setting general_log_file to a my.cnf configuration. NOTE: this can be leveraged to execute arbitrary code with root privileges by setting malloc_lib. NOTE: the affected MySQL version information is from Oracle's October 2016 CPU. Oracle has not commented on third-party claims that the issue was silently patched in MySQL 5.5.52, 5.6.33, and 5.7.15. |
| CVE-2016-0635 | High | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.4, 12.2.2, and 12.3.2; the Oracle Health Sciences Information Manager component in Oracle Health Sciences Applications 1.2.8.3, 2.0.2.3, and 3.0.1.0; the Oracle Healthcare Master Person Index component in Oracle Health Sciences Applications 2.0.12, 3.0.0, and 4.0.1; the Oracle Documaker component in Oracle Insurance Applications before 12.5; the Oracle Insurance Calculation Engine component in Oracle Insurance Applications 9.7.1, 10.1.2, and 10.2.2; the Oracle Insurance Policy Administration J2EE and Oracle Insurance Rules Palette components in Oracle Insurance Applications 9.6.1, 9.7.1, 10.0.1, 10.1.2, 10.2.0, and 10.2.2; the Oracle Retail Integration Bus component in Oracle Retail Applications 15.0; the Oracle Retail Order Broker component in Oracle Retail Applications 5.1, 5.2, and 15.0; the Primavera Contract Management component in Oracle Primavera Products Suite 14.2; the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.2, 8.3, 8.4, 15.1, 15.2, and 16.1; the Oracle Financial Services Analytical Applications Infrastructure component in Oracle Financial Services Applications 8.0.0, 8.0.1, 8.0.2, and 8.0.3; the Oracle Commerce Guided Search / Oracle Commerce Experience Manager component in Oracle Commerce 3.1.1, 3.1.2, 11.0, 11.1, and 11.2; the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5; the Oracle Communications BRM - Elastic Charging Engine 11.2.0.0.0 and 11.3.0.0.0; the Oracle Enterprise Repository Enterprise Repository 12.1.3.0.0; the Oracle Financial Services Behavior Detection Platform 8.0.1 and 8.0.2; the Oracle Hyperion Essbase 12.2.1.1; the Oracle Tuxedo System and Applications Monitor (TSAM) 11.1.1.2.0, 11.1.1.2.1, 11.1.1.2.1, 12.1.1.1.0, 12.1.3.0.0, and 12.2.2.0.0; the Oracle Communications WebRTC Session Controller component of Oracle Communications Applications (subcomponent: Security (Spring)) 7.0, 7.1 and 7.2; the Oracle Endeca Information Discovery Integrator 3.2; the Converged Commerce component of Oracle Retail Applications 16.0.1; the Oracle Identity Manager 11.1.2.3.0; Oracle Enterprise Manager for MySQL Database 12.1.0.4; Oracle Retail Invoice Matching 12.0, 13.0, 13.1, 13.2, 14.0, and 14.1; Oracle Communications Performance Intelligence Center (PIC) Software Prior to 10.2.1 and the Oracle Knowledge component of Oracle Siebel CRM (subcomponent: AnswerFlow (Spring Framework)) version 8.5.1.0 - 8.5.1.7 and 8.6.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-4979 | High | 2016-07-06 | Not applicable | No public exploit | The Apache HTTP Server 2.4.18 through 2.4.20, when mod_http2 and mod_ssl are enabled, does not properly recognize the "SSLVerifyClient require" directive for HTTP/2 request authorization, which allows remote attackers to bypass intended access restrictions by leveraging the ability to send multiple requests over a single connection and aborting a renegotiation. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2016-2176 | High | 2016-05-05 | Not applicable | No public exploit | The X509_NAME_oneline function in crypto/x509/x509_obj.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to obtain sensitive information from process stack memory or cause a denial of service (buffer over-read) via crafted EBCDIC ASN.1 data. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-3081 | High | 2016-04-26 | Protected by Waratek | Exploited | Apache Struts 2.3.19 to 2.3.20.2, 2.3.21 to 2.3.24.1, and 2.3.25 to 2.3.28, when Dynamic Method Invocation is enabled, allow remote attackers to execute arbitrary code via method: prefix, related to chained expressions. |
| CVE-2016-1950 | High | 2016-03-13 | Outside Waratek scope | No public exploit | Heap-based buffer overflow in Mozilla Network Security Services (NSS) before 3.19.2.3 and 3.20.x and 3.21.x before 3.21.1, as used in Mozilla Firefox before 45.0 and Firefox ESR 38.x before 38.7, allows remote attackers to execute arbitrary code via crafted ASN.1 data in an X.509 certificate. |