
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
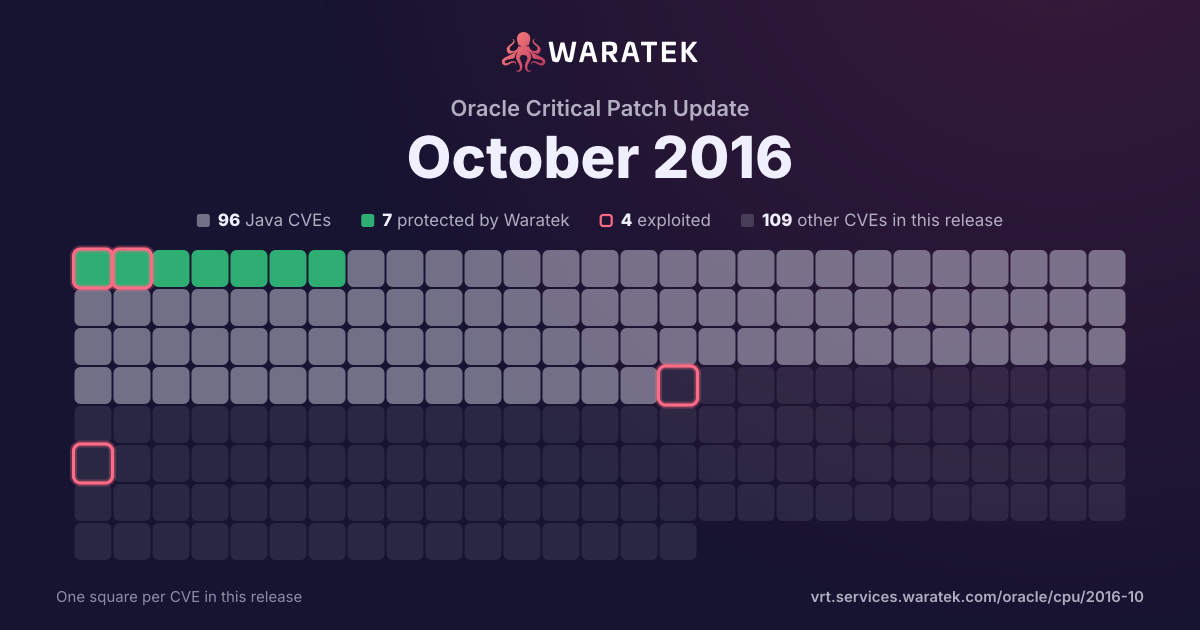
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 205 matches · 96 in Waratek scope · 7 protected · 4 exploited · 1 CISA KEV · 11 public PoC · 10 EPSS ≥ 0.5
205matches
96in Waratek scope46.8%
7protected3.4%
4exploited2.0%
1CISA KEV0.5%
11public PoC5.4%
10EPSS ≥ 0.54.9%
Protected by Waratek
7
3.4%
Rule in development
0
0.0%
Mitigation candidate
2
1.0%
No exploit published
87
42.4%
Outside Waratek scope
39
19.0%
Not applicable
68
33.2%
Withdrawn CVE
2
1.0%
blocked by ARMR today
7
3.4%
partly blocked
0
0.0%
not blocked
198
96.6%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
4
2.0%
Working exploit published
7
3.4%
Proof of concept only
0
0.0%
Forecast only
2
1.0%
No public exploit
192
93.7%
split by
peak 159 / quarter
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 131
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 144
Protected by Waratek1
No exploit published1
Outside Waratek scope2
Medium4
blocked by ARMR today1
not blocked3
No public exploit4
Q2 146
Protected by Waratek2
Mitigation candidate1
No exploit published2
Outside Waratek scope1
High2
Medium4
blocked by ARMR today2
not blocked4
Exploited1
Working exploit published1
No public exploit4
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 142
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
No public exploit2
Q1 159
Outside Waratek scope6
Not applicable3
High3
Medium6
not blocked9
Working exploit published1
No public exploit8
Q2 155
Outside Waratek scope4
Not applicable1
Medium5
not blocked5
No public exploit5
Q3 152
Outside Waratek scope2
Critical1
Medium1
not blocked2
Working exploit published1
No public exploit1
Q4 152
Outside Waratek scope2
Medium2
not blocked2
No public exploit2
Q1 163
Outside Waratek scope3
High2
Medium1
not blocked3
No public exploit3
Q2 163
Protected by Waratek1
Not applicable2
High2
Medium1
blocked by ARMR today1
not blocked2
Exploited1
Working exploit published1
No public exploit1
Q3 165
Protected by Waratek1
Outside Waratek scope1
Not applicable3
Critical1
High4
blocked by ARMR today1
not blocked4
Exploited1
Forecast only1
No public exploit3
Q4 16159
Protected by Waratek1
Mitigation candidate1
No exploit published83
Outside Waratek scope15
Not applicable57
Withdrawn CVE2
Critical10
High45
Medium86
Low16
Unknown2
blocked by ARMR today1
not blocked158
Working exploit published3
No public exploit156
Q1 171
Not applicable1
High1
not blocked1
No public exploit1
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16Q2 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-1881 | High | 2017-02-15 | Not applicable | No public exploit | The kernel in FreeBSD 9.3, 10.1, and 10.2 allows local users to cause a denial of service (crash) or potentially gain privilege via a crafted Linux compatibility layer setgroups system call. |
| CVE-2016-7440 | Medium | 2016-12-13 | Not applicable | No public exploit | The C software implementation of AES Encryption and Decryption in wolfSSL (formerly CyaSSL) before 3.9.10 makes it easier for local users to discover AES keys by leveraging cache-bank timing differences. |
| CVE-2016-8296 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to LDAP. |
| CVE-2016-8295 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-8294 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-8293 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5529 and CVE-2016-5530. |
| CVE-2016-8292 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to Talent Acquisition Manager. |
| CVE-2016-8291 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Mobile Application Platform. |
| CVE-2016-8290 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-5633. |
| CVE-2016-8289 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows local users to affect integrity and availability via vectors related to Server: InnoDB. |
| CVE-2016-8288 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.30 and earlier and 5.7.12 and earlier allows remote authenticated users to affect integrity via vectors related to Server: InnoDB Plugin. |
| CVE-2016-8287 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Replication. |
| CVE-2016-8286 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows remote authenticated users to affect confidentiality via vectors related to Server: Security: Privileges. |
| CVE-2016-8285 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote administrators to affect confidentiality and integrity via vectors related to Candidate Gateway. |
| CVE-2016-8284 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows local users to affect availability via vectors related to Server: Replication. |
| CVE-2016-8283 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Types. |
| CVE-2016-8281 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-5536. |
| CVE-2016-5635 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Security: Audit. |
| CVE-2016-5634 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to RBR. |
| CVE-2016-5633 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-8290. |
| CVE-2016-5632 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-5631 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Memcached. |
| CVE-2016-5630 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5629 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Federated. |
| CVE-2016-5628 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: DML. |
| CVE-2016-5627 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5626 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to GIS. |
| CVE-2016-5625 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows local users to affect confidentiality, integrity, and availability via vectors related to Server: Packaging. |
| CVE-2016-5624 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5622 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote attackers to affect confidentiality and integrity via vectors related to INFRA. |
| CVE-2016-5621 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 and 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality via vectors related to INFRA, a different vulnerability than CVE-2016-5603. |
| CVE-2016-5620 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA, a different vulnerability than CVE-2016-5619. |
| CVE-2016-5619 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA, a different vulnerability than CVE-2016-5620. |
| CVE-2016-5618 | Low | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.2.0.0, 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality via vectors related to Code Generation Engine. |
| CVE-2016-5617 | Unknown | 2016-10-25 | Withdrawn CVE | Working exploit published | Rejected reason: DO NOT USE THIS CANDIDATE NUMBER. ConsultIDs: CVE-2016-6664. Reason: This candidate is a reservation duplicate of CVE-2016-6664. Notes: All CVE users should reference CVE-2016-6664 instead of this candidate. All references and descriptions in this candidate have been removed to prevent accidental usage |
| CVE-2016-5616 | Unknown | 2016-10-25 | Withdrawn CVE | Working exploit published | Rejected reason: DO NOT USE THIS CANDIDATE NUMBER. ConsultIDs: CVE-2016-6663. Reason: This candidate is a reservation duplicate of CVE-2016-6663. Notes: All CVE users should reference CVE-2016-6663 instead of this candidate. All references and descriptions in this candidate have been removed to prevent accidental usage |
| CVE-2016-5615 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Lynx. |
| CVE-2016-5613 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5608. |
| CVE-2016-5612 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.50 and earlier, 5.6.31 and earlier, and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5611 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality via vectors related to Core. |
| CVE-2016-5610 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core. |
| CVE-2016-5609 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5608 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5613. |
| CVE-2016-5607 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to INFRA. |
| CVE-2016-5606 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect integrity and availability via vectors related to Kernel Zones. |
| CVE-2016-5605 | Critical | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.1.4 in Oracle Virtualization allows remote attackers to affect confidentiality and integrity via vectors related to VRDE. |
| CVE-2016-5604 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 12.1.0.5 allows local users to affect confidentiality and integrity via vectors related to Security Framework, a different vulnerability than CVE-2016-3563. |
| CVE-2016-5603 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality via vectors related to INFRA, a different vulnerability than CVE-2016-5621. |
| CVE-2016-5602 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality via vectors related to Code Generation Engine. |
| CVE-2016-5601 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows local users to affect confidentiality and integrity via vectors related to CIE Related Components. |
| CVE-2016-5600 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM Services Procurement component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5599 | Critical | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Supply Chain Planning component in Oracle Supply Chain Products Suite 12.2.3 through 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to MscObieeSrvlt. |
| CVE-2016-5598 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Connector component 2.1.3 and earlier and 2.0.4 and earlier in Oracle MySQL allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Connector/Python. |
| CVE-2016-5597 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect confidentiality via vectors related to Networking. |
| CVE-2016-5596 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5595 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5592. |
| CVE-2016-5594 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, and 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality via vectors related to INFRA. |
| CVE-2016-5593 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5587 and CVE-2016-5591. |
| CVE-2016-5592 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5595. |
| CVE-2016-5591 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5587 and CVE-2016-5593. |
| CVE-2016-5589 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5588 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, and CVE-2016-5579. |
| CVE-2016-5587 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5591 and CVE-2016-5593. |
| CVE-2016-5586 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Email Center component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5585 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Interaction Center Intelligence component in Oracle E-Business Suite 12.1.1 through 12.1.3 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5584 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.52 and earlier, 5.6.33 and earlier, and 5.7.15 and earlier allows remote administrators to affect confidentiality via vectors related to Server: Security: Encryption. |
| CVE-2016-5583 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle One-to-One Fulfillment component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2016-5582 | Critical | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Hotspot, a different vulnerability than CVE-2016-5573. |
| CVE-2016-5581 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iRecruitment component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5580 | Critical | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Secure Global Desktop component in Oracle Virtualization 4.7 and 5.2 allows remote authenticated users to affect confidentiality and availability via vectors through Web Services. |
| CVE-2016-5579 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, and CVE-2016-5588. |
| CVE-2016-5578 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5577, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5577 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5574, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5576 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Kernel Zones. |
| CVE-2016-5575 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality via vectors related to Resources Module. |
| CVE-2016-5574 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5558, CVE-2016-5577, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5573 | High | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Hotspot, a different vulnerability than CVE-2016-5582. |
| CVE-2016-5572 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Kernel PDB component in Oracle Database Server 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5571 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 and 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities, a different vulnerability than CVE-2016-5567. |
| CVE-2016-5570 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities. |
| CVE-2016-5569 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component in Oracle Financial Services Applications 12.0.0 and 12.1.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5568 | Critical | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, and 8u102 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to AWT. |
| CVE-2016-5567 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 and 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities, a different vulnerability than CVE-2016-5571. |
| CVE-2016-5566 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-5565 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote authenticated users to affect confidentiality via vectors related to OPERA. |
| CVE-2016-5564 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to OPERA. |
| CVE-2016-5563 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote administrators to affect confidentiality, integrity, and availability via vectors related to OPERA. |
| CVE-2016-5562 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iProcurement component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5561 | Low | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect availability via vectors related to IKE. |
| CVE-2016-5560 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 16.1 allows remote authenticated users to affect confidentiality and integrity via vectors related to OpenUI. |
| CVE-2016-5559 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect integrity via vectors related to Kernel. |
| CVE-2016-5558 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.5.1 through 8.5.3 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Outside In Filters, a different vulnerability than CVE-2016-5574, CVE-2016-5577, CVE-2016-5578, CVE-2016-5579, and CVE-2016-5588. |
| CVE-2016-5557 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Pricing component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5556 | Critical | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, and 8u102 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to 2D. |
| CVE-2016-5555 | Critical | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the OJVM component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows remote administrators to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5554 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect integrity via vectors related to JMX. |
| CVE-2016-5553 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect availability via unknown vectors. |
| CVE-2016-5544 | High | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect confidentiality, integrity, and availability via vectors related to Kernel/X86. |
| CVE-2016-5543 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component in Oracle Financial Services Applications 12.0.0 and 12.1.0 allows remote attackers to affect confidentiality and integrity via vectors related to INFRA. |