
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
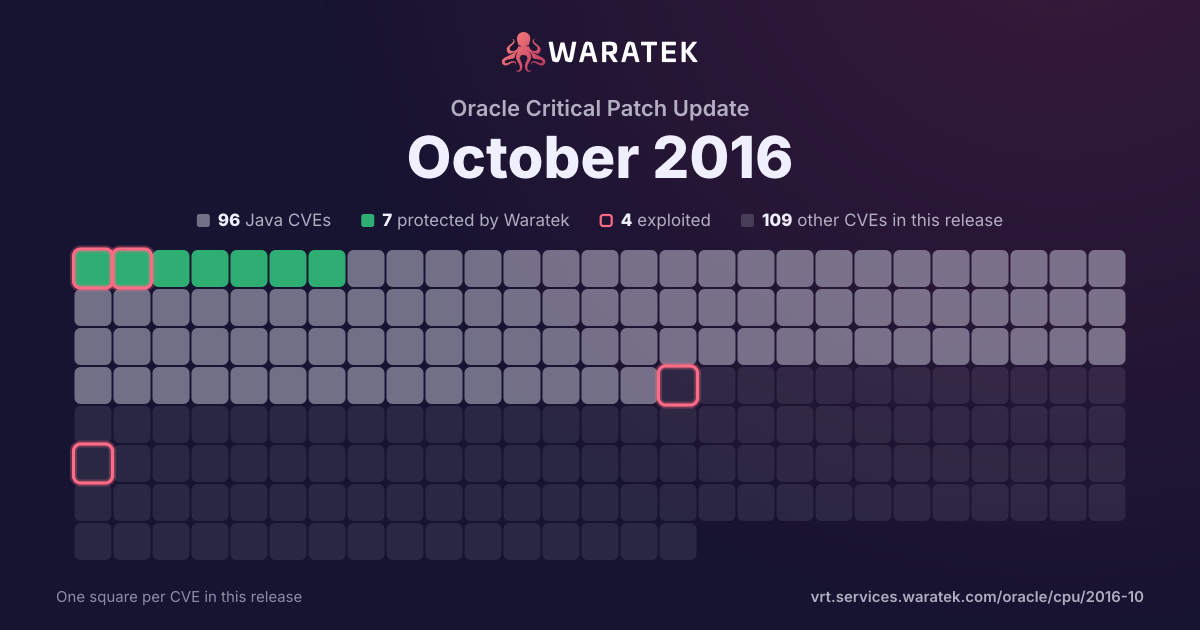
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
5matches
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
5
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
5
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
5
100.0%
split by
peak 2 / quarter
Q1 141
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q2 142
Protected by Waratek2
Medium2
blocked by ARMR today2
No public exploit2
Q3 140
Q4 140
Q1 150
Q2 150
Q3 150
Q4 150
Q1 160
Q2 160
Q3 161
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Q4 161
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Q1 14Q2 14Q3 14Q4 14Q1 15Q2 15Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-5537 | Medium | 2016-10-25 | Protected by Waratek | No public exploit | Unspecified vulnerability in the NetBeans component in Oracle Fusion Middleware 8.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the October 2016 CPU. Oracle has not commented on third-party claims that this issue is a directory traversal vulnerability which allows local users with certain permissions to write to arbitrary files and consequently gain privileges via a .. (dot dot) in a archive entry in a ZIP file imported as a project. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |
| CVE-2014-0119 | Medium | 2014-05-31 | Protected by Waratek | No public exploit | Apache Tomcat before 6.0.40, 7.x before 7.0.54, and 8.x before 8.0.6 does not properly constrain the class loader that accesses the XML parser used with an XSLT stylesheet, which allows remote attackers to (1) read arbitrary files via a crafted web application that provides an XML external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue, or (2) read files associated with different web applications on a single Tomcat instance via a crafted web application. |
| CVE-2014-0096 | Medium | 2014-05-31 | Protected by Waratek | No public exploit | java/org/apache/catalina/servlets/DefaultServlet.java in the default servlet in Apache Tomcat before 6.0.40, 7.x before 7.0.53, and 8.x before 8.0.4 does not properly restrict XSLT stylesheets, which allows remote attackers to bypass security-manager restrictions and read arbitrary files via a crafted web application that provides an XML external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue. |
| CVE-2013-4590 | Medium | 2014-02-26 | Protected by Waratek | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.50, and 8.x before 8.0.0-RC10 allows attackers to obtain "Tomcat internals" information by leveraging the presence of an untrusted web application with a context.xml, web.xml, *.jspx, *.tagx, or *.tld XML document containing an external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue. |