
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
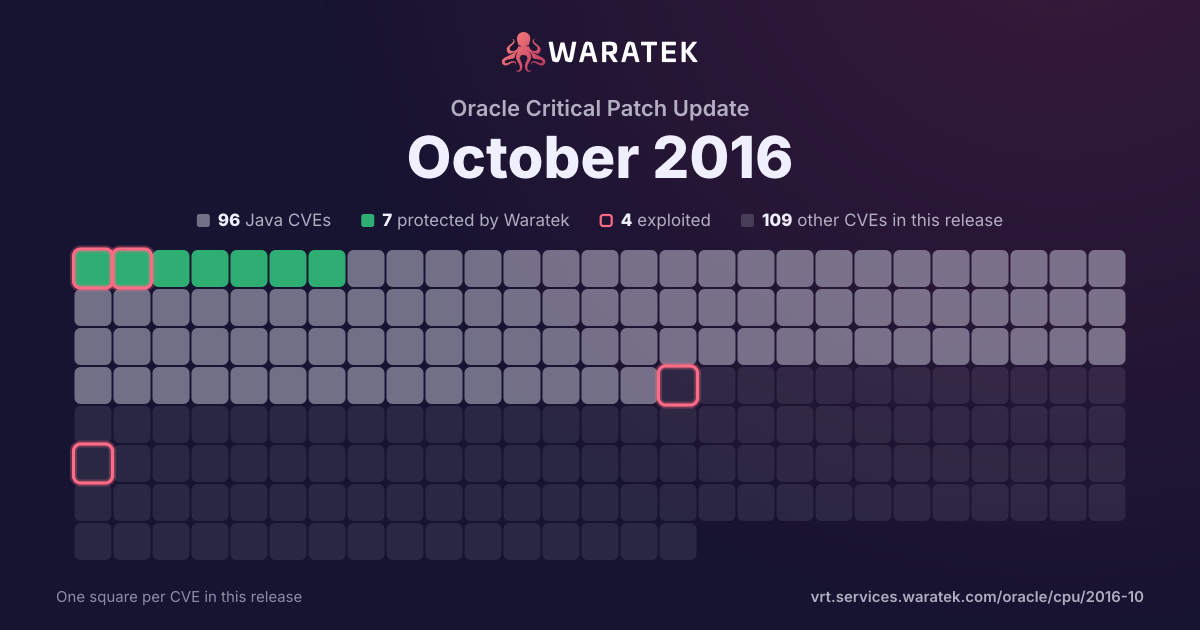
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 115 matches · 52 in Waratek scope · 4 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 3 EPSS ≥ 0.5
115matches
52in Waratek scope45.2%
4protected3.5%
0exploited0.0%
0CISA KEV0.0%
2public PoC1.7%
3EPSS ≥ 0.52.6%
Protected by Waratek
4
3.5%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
48
41.7%
Outside Waratek scope
23
20.0%
Not applicable
40
34.8%
Withdrawn CVE
0
0.0%
blocked by ARMR today
4
3.5%
partly blocked
0
0.0%
not blocked
111
96.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
1.7%
Proof of concept only
0
0.0%
Forecast only
1
0.9%
No public exploit
112
97.4%
split by
peak 86 / quarter
Q1 131
Outside Waratek scope1
Medium1
not blocked1
Forecast only1
Q2 131
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 144
Protected by Waratek1
No exploit published1
Outside Waratek scope2
Medium4
blocked by ARMR today1
not blocked3
No public exploit4
Q2 144
Protected by Waratek2
No exploit published2
Medium4
blocked by ARMR today2
not blocked2
No public exploit4
Q3 141
No exploit published1
Medium1
not blocked1
No public exploit1
Q4 142
Outside Waratek scope1
Not applicable1
Medium2
not blocked2
No public exploit2
Q1 156
Outside Waratek scope4
Not applicable2
Medium6
not blocked6
No public exploit6
Q2 155
Outside Waratek scope4
Not applicable1
Medium5
not blocked5
No public exploit5
Q3 151
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Q4 152
Outside Waratek scope2
Medium2
not blocked2
No public exploit2
Q1 161
Outside Waratek scope1
Medium1
not blocked1
No public exploit1
Q2 161
Not applicable1
Medium1
not blocked1
Working exploit published1
Q3 160
Q4 1686
Protected by Waratek1
No exploit published44
Outside Waratek scope6
Not applicable35
Medium86
blocked by ARMR today1
not blocked85
No public exploit86
Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16Q4 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-7440 | Medium | 2016-12-13 | Not applicable | No public exploit | The C software implementation of AES Encryption and Decryption in wolfSSL (formerly CyaSSL) before 3.9.10 makes it easier for local users to discover AES keys by leveraging cache-bank timing differences. |
| CVE-2016-8295 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-8294 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-8292 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality and integrity via vectors related to Talent Acquisition Manager. |
| CVE-2016-8290 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-5633. |
| CVE-2016-8289 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows local users to affect integrity and availability via vectors related to Server: InnoDB. |
| CVE-2016-8287 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Replication. |
| CVE-2016-8285 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM component in Oracle PeopleSoft Products 9.2 allows remote administrators to affect confidentiality and integrity via vectors related to Candidate Gateway. |
| CVE-2016-8283 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Types. |
| CVE-2016-5635 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Security: Audit. |
| CVE-2016-5634 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to RBR. |
| CVE-2016-5633 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Performance Schema, a different vulnerability than CVE-2016-8290. |
| CVE-2016-5632 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-5631 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: Memcached. |
| CVE-2016-5630 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5629 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: Federated. |
| CVE-2016-5628 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: DML. |
| CVE-2016-5627 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5626 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to GIS. |
| CVE-2016-5624 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5622 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote attackers to affect confidentiality and integrity via vectors related to INFRA. |
| CVE-2016-5621 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 and 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality via vectors related to INFRA, a different vulnerability than CVE-2016-5603. |
| CVE-2016-5620 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA, a different vulnerability than CVE-2016-5619. |
| CVE-2016-5613 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5608. |
| CVE-2016-5612 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.50 and earlier, 5.6.31 and earlier, and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5611 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality via vectors related to Core. |
| CVE-2016-5610 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core. |
| CVE-2016-5609 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.31 and earlier and 5.7.13 and earlier allows remote authenticated users to affect availability via vectors related to DML. |
| CVE-2016-5608 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect availability via vectors related to Core, a different vulnerability than CVE-2016-5613. |
| CVE-2016-5606 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect integrity and availability via vectors related to Kernel Zones. |
| CVE-2016-5604 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control 12.1.0.5 allows local users to affect confidentiality and integrity via vectors related to Security Framework, a different vulnerability than CVE-2016-3563. |
| CVE-2016-5603 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality via vectors related to INFRA, a different vulnerability than CVE-2016-5621. |
| CVE-2016-5602 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality via vectors related to Code Generation Engine. |
| CVE-2016-5601 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0, 12.2.1.0, and 12.2.1.1 allows local users to affect confidentiality and integrity via vectors related to CIE Related Components. |
| CVE-2016-5600 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM Services Procurement component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5598 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Connector component 2.1.3 and earlier and 2.0.4 and earlier in Oracle MySQL allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Connector/Python. |
| CVE-2016-5597 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect confidentiality via vectors related to Networking. |
| CVE-2016-5596 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5594 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, and 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality via vectors related to INFRA. |
| CVE-2016-5585 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Interaction Center Intelligence component in Oracle E-Business Suite 12.1.1 through 12.1.3 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5584 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.52 and earlier, 5.6.33 and earlier, and 5.7.15 and earlier allows remote administrators to affect confidentiality via vectors related to Server: Security: Encryption. |
| CVE-2016-5583 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle One-to-One Fulfillment component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2016-5581 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iRecruitment component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5576 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect availability via vectors related to Kernel Zones. |
| CVE-2016-5575 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality via vectors related to Resources Module. |
| CVE-2016-5572 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Kernel PDB component in Oracle Database Server 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5571 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 and 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities, a different vulnerability than CVE-2016-5567. |
| CVE-2016-5570 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities. |
| CVE-2016-5569 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component in Oracle Financial Services Applications 12.0.0 and 12.1.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5567 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 and 12.2.3 through 12.2.6 allows remote administrators to affect confidentiality and integrity via vectors related to AD Utilities, a different vulnerability than CVE-2016-5571. |
| CVE-2016-5566 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-5560 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 16.1 allows remote authenticated users to affect confidentiality and integrity via vectors related to OpenUI. |
| CVE-2016-5559 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect integrity via vectors related to Kernel. |
| CVE-2016-5554 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u121, 7u111, 8u102; and Java SE Embedded 8u101 allows remote attackers to affect integrity via vectors related to JMX. |
| CVE-2016-5553 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.3 allows local users to affect availability via unknown vectors. |
| CVE-2016-5543 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Enterprise Limits and Collateral Management component in Oracle Financial Services Applications 12.0.0 and 12.1.0 allows remote attackers to affect confidentiality and integrity via vectors related to INFRA. |
| CVE-2016-5540 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Xstore Payment component in Oracle Retail Applications 1.x allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5538 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component before 5.0.28 and 5.1.x before 5.1.8 in Oracle Virtualization allows local users to affect confidentiality, integrity, and availability via vectors related to Core, a different vulnerability than CVE-2016-5501. |
| CVE-2016-5537 | Medium | 2016-10-25 | Protected by Waratek | No public exploit | Unspecified vulnerability in the NetBeans component in Oracle Fusion Middleware 8.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors. NOTE: the previous information is from the October 2016 CPU. Oracle has not commented on third-party claims that this issue is a directory traversal vulnerability which allows local users with certain permissions to write to arbitrary files and consequently gain privileges via a .. (dot dot) in a archive entry in a ZIP file imported as a project. |
| CVE-2016-5534 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Apps - Customer Order Management component in Oracle Siebel CRM 16.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5533 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.4, 15.x, and 16.x allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5532 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Shipping Execution component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality via vectors related to Workflow Events. |
| CVE-2016-5530 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5529 and CVE-2016-8293. |
| CVE-2016-5529 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5530 and CVE-2016-8293. |
| CVE-2016-5527 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5524. |
| CVE-2016-5524 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors, a different vulnerability than CVE-2016-5527. |
| CVE-2016-5522 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-5521 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5512. |
| CVE-2016-5517 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.1.3 allows local users to affect confidentiality via vectors related to AD Utilities. |
| CVE-2016-5516 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Kernel PDB component in Oracle Database Server 12.1.0.2 allows local users to affect availability via unknown vectors. |
| CVE-2016-5513 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to File Manager. |
| CVE-2016-5512 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5521. |
| CVE-2016-5511 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 12.2.1.0.0, 12.2.1.1.0, and 12.2.1.2.0 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2016-5510 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2016-5507 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.32 and earlier and 5.7.14 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-5505 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Programmable Interface component in Oracle Database Server 11.2.0.4 and 12.1.0.2 allows local users to affect confidentiality via unknown vectors. |
| CVE-2016-5504 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Lifecycle Management for Process component in Oracle Supply Chain Products Suite 6.1.0.4, 6.1.1.6, and 6.2.0.0 allows local users to affect confidentiality via vectors related to Supplier Portal. |
| CVE-2016-5502 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA. |
| CVE-2016-5497 | Medium | 2016-10-25 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Security component in Oracle Database Server 12.1.0.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5493 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Private Banking component in Oracle Financial Services Applications 12.0.1 through 12.0.3 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5488 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0 and 12.1.3.0 allows remote attackers to affect availability via vectors related to Web Container, a different vulnerability than CVE-2016-3445. |
| CVE-2016-5487 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5486 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in the Sun ZFS Storage Appliance Kit (AK) component in Oracle Sun Systems Products Suite AK 2013 allows local users to affect confidentiality via vectors related to Core Services. |
| CVE-2016-5479 | Medium | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, and 12.0.1 allows remote authenticated users to affect confidentiality via vectors related to INFRA. |
| CVE-2016-3495 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.7.13 and earlier allows remote administrators to affect availability via vectors related to Server: InnoDB. |
| CVE-2016-3492 | Medium | 2016-10-25 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.51 and earlier, 5.6.32 and earlier, and 5.7.14 and earlier allows remote authenticated users to affect availability via vectors related to Server: Optimizer. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2015-3197 | Medium | 2016-02-15 | Outside Waratek scope | No public exploit | ssl/s2_srvr.c in OpenSSL 1.0.1 before 1.0.1r and 1.0.2 before 1.0.2f does not prevent use of disabled ciphers, which makes it easier for man-in-the-middle attackers to defeat cryptographic protection mechanisms by performing computations on SSLv2 traffic, related to the get_client_master_key and get_client_hello functions. |
| CVE-2015-3195 | Medium | 2015-12-06 | Outside Waratek scope | No public exploit | The ASN1_TFLG_COMBINE implementation in crypto/asn1/tasn_dec.c in OpenSSL before 0.9.8zh, 1.0.0 before 1.0.0t, 1.0.1 before 1.0.1q, and 1.0.2 before 1.0.2e mishandles errors caused by malformed X509_ATTRIBUTE data, which allows remote attackers to obtain sensitive information from process memory by triggering a decoding failure in a PKCS#7 or CMS application. |
| CVE-2015-7940 | Medium | 2015-11-09 | Outside Waratek scope | No public exploit | The Bouncy Castle Java library before 1.51 does not validate a point is withing the elliptic curve, which makes it easier for remote attackers to obtain private keys via a series of crafted elliptic curve Diffie Hellman (ECDH) key exchanges, aka an "invalid curve attack." |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |
| CVE-2015-2568 | Medium | 2015-04-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.41 and earlier, and 5.6.22 and earlier, allows remote attackers to affect availability via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-0500 | Medium | 2015-04-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.23 and earlier allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2015-0433 | Medium | 2015-04-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.41 and earlier, and 5.6.22 and earlier, allows remote authenticated users to affect availability via vectors related to InnoDB : DML. |
| CVE-2015-0423 | Medium | 2015-04-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.22 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2015-0286 | Medium | 2015-03-19 | Not applicable | No public exploit | The ASN1_TYPE_cmp function in crypto/asn1/a_type.c in OpenSSL before 0.9.8zf, 1.0.0 before 1.0.0r, 1.0.1 before 1.0.1m, and 1.0.2 before 1.0.2a does not properly perform boolean-type comparisons, which allows remote attackers to cause a denial of service (invalid read operation and application crash) via a crafted X.509 certificate to an endpoint that uses the certificate-verification feature. |
| CVE-2014-0227 | Medium | 2015-02-16 | Outside Waratek scope | No public exploit | java/org/apache/coyote/http11/filters/ChunkedInputFilter.java in Apache Tomcat 6.x before 6.0.42, 7.x before 7.0.55, and 8.x before 8.0.9 does not properly handle attempts to continue reading data after an error has occurred, which allows remote attackers to conduct HTTP request smuggling attacks or cause a denial of service (resource consumption) by streaming data with malformed chunked transfer coding. |
| CVE-2015-0409 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.21 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2015-0382 | Medium | 2015-01-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.40 and earlier and 5.6.21 and earlier allows remote attackers to affect availability via unknown vectors related to Server : Replication, a different vulnerability than CVE-2015-0381. |