
Oracle Critical Patch Update October 2016
Released October 2016 · Oracle's advisory ↗ · ← Critical Patch Update, July 2016 · Critical Patch Update, January 2017 →
205 CVEs in this release, one square each
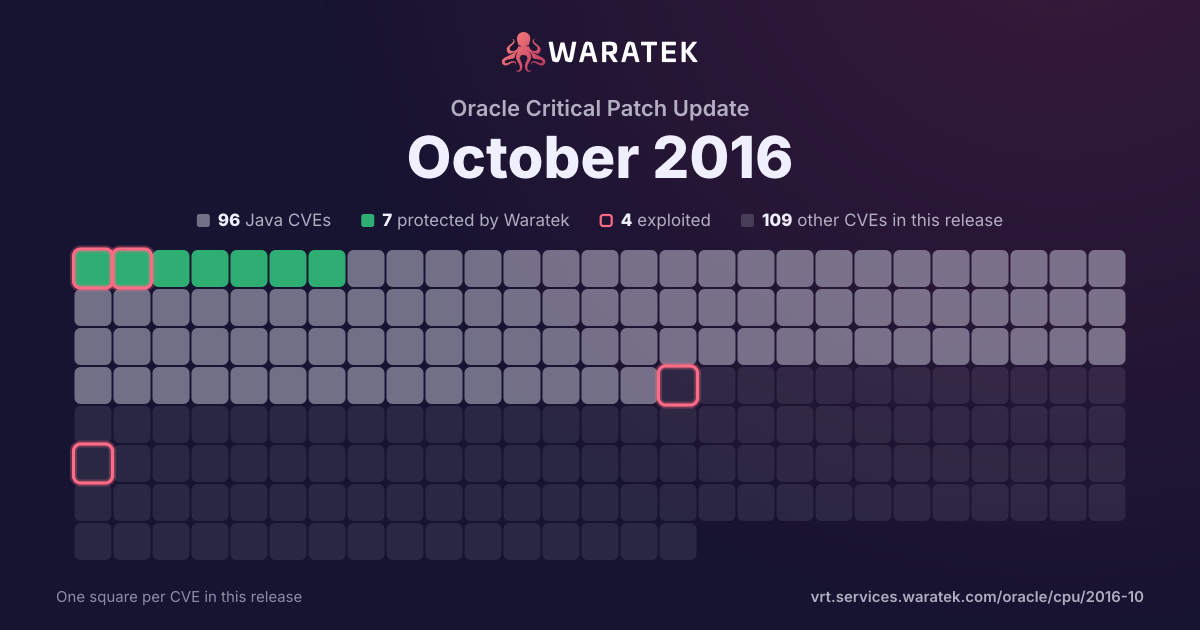
By status
7Protected by Waratek2Mitigation candidate87No exploit published39Outside Waratek scope68Not applicable2Withdrawn CVE
4Exploited, marked by the ring
No exploit published. For 83 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 34 matches · 1 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
1
2.9%
Rule in development
0
0.0%
Mitigation candidate
1
2.9%
No exploit published
32
94.1%
blocked by ARMR today
1
2.9%
partly blocked
0
0.0%
not blocked
33
97.1%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
2.9%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
33
97.1%
split by
peak 33 / month
Jul 16Aug 16Sep 16Oct 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-8296 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote authenticated users to affect confidentiality and integrity via vectors related to LDAP. |
| CVE-2016-8293 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Integration Broker, a different vulnerability than CVE-2016-5529 and CVE-2016-5530. |
| CVE-2016-8291 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.54 and 8.55 allows remote attackers to affect confidentiality and integrity via vectors related to Mobile Application Platform. |
| CVE-2016-8281 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-5536. |
| CVE-2016-5619 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality and integrity via vectors related to INFRA, a different vulnerability than CVE-2016-5620. |
| CVE-2016-5607 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle FLEXCUBE Universal Banking component in Oracle Financial Services Applications 11.3.0, 11.4.0, 12.0.1 through 12.0.3, 12.1.0, and 12.2.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to INFRA. |
| CVE-2016-5595 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5592. |
| CVE-2016-5593 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5587 and CVE-2016-5591. |
| CVE-2016-5592 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5595. |
| CVE-2016-5591 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5587 and CVE-2016-5593. |
| CVE-2016-5589 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5587 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors, a different vulnerability than CVE-2016-5591 and CVE-2016-5593. |
| CVE-2016-5586 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Email Center component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5565 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote authenticated users to affect confidentiality via vectors related to OPERA. |
| CVE-2016-5564 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to OPERA. |
| CVE-2016-5563 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Hospitality OPERA 5 Property Services component in Oracle Hospitality Applications 5.4.0.0 through 5.4.3.0, 5.5.0.0, and 5.5.1.0 allows remote administrators to affect confidentiality, integrity, and availability via vectors related to OPERA. |
| CVE-2016-5562 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iProcurement component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5557 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Pricing component in Oracle E-Business Suite 12.1.1 through 12.1.3 and 12.2.3 through 12.2.6 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5539 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Xstore Payment component in Oracle Retail Applications 1.x allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-5536 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Platform Security for Java component in Oracle Fusion Middleware 12.1.3.0.0, 12.2.1.0.0, and 12.2.1.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2016-8281. |
| CVE-2016-5526 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Apache Tomcat. |
| CVE-2016-5523 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to AutoVue Java Applet. |
| CVE-2016-5519 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to Java Server Faces. |
| CVE-2016-5518 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to webfileservices. |
| CVE-2016-5515 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to RMIServlet. |
| CVE-2016-5514 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to ExportServlet. |
| CVE-2016-5500 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to Viewer. |
| CVE-2016-5495 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Discoverer component in Oracle Fusion Middleware 11.1.1.7.0 allows remote attackers to affect confidentiality via vectors related to EUL Code & Schema. |
| CVE-2016-5491 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Service Center component in Oracle Commerce 10.0.3.5 and 10.2.0.5 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-5489 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iStore component in Oracle E-Business Suite 12.1.1 through 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via vectors related to Runtime Catalog. |
| CVE-2016-5482 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Commerce Guided Search component in Oracle Commerce 6.2.2, 6.3.0, 6.4.1.2, and 6.5.0 through 6.5.2 allows remote attackers to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3505 | High | 2016-10-25 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to JavaServer Faces. |
| CVE-2016-3473 | High | 2016-10-25 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2016-1181 | High | 2016-07-04 | Protected by Waratek | No public exploit | ActionServlet.java in Apache Struts 1 1.x through 1.3.10 mishandles multithreaded access to an ActionForm instance, which allows remote attackers to execute arbitrary code or cause a denial of service (unexpected memory access) via a multipart request, a related issue to CVE-2015-0899. |