
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
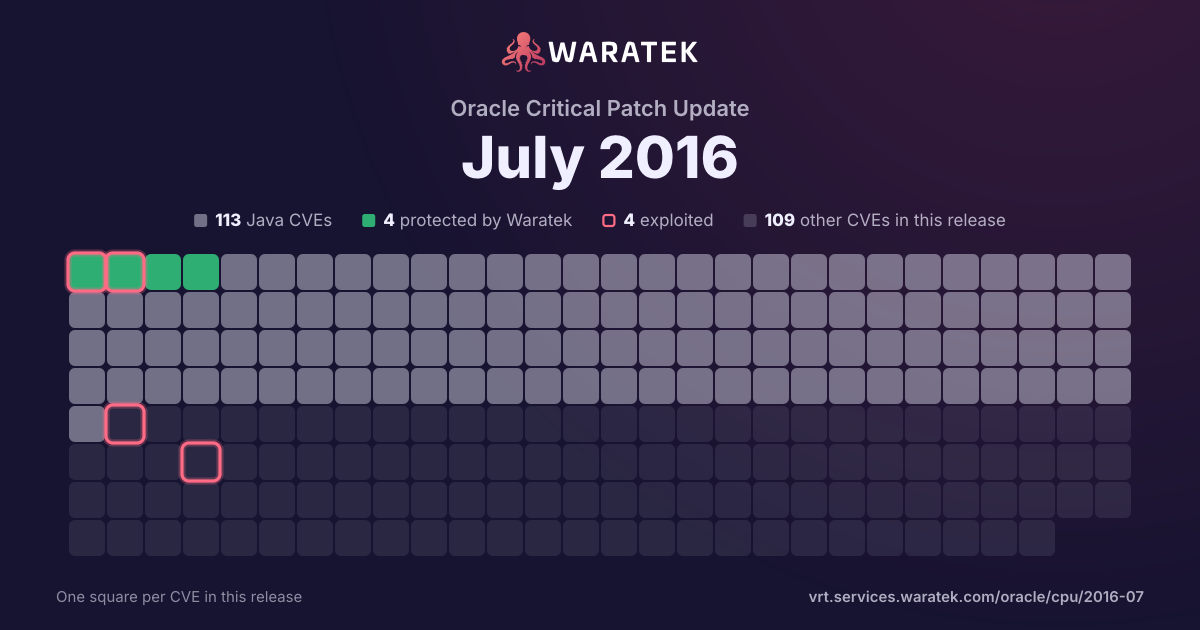
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 14 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 3 public PoC · 4 EPSS ≥ 0.5
14matches
0in Waratek scope0.0%
0protected0.0%
1exploited7.1%
0CISA KEV0.0%
3public PoC21.4%
4EPSS ≥ 0.528.6%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
14
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
14
100.0%
not established
0
0.0%
unrecorded
0
0.0%
split by
peak 3 / quarter
Q3 121
Not applicable1
Medium1
not blocked1
No public exploit1
Q4 120
Q1 130
Q2 131
Not applicable1
Medium1
not blocked1
No public exploit1
Q3 130
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 153
Not applicable3
Medium3
not blocked3
Exploited1
No public exploit2
Q2 152
Not applicable2
Medium2
not blocked2
No public exploit2
Q3 152
Not applicable2
High1
Medium1
not blocked2
Forecast only1
No public exploit1
Q4 151
Not applicable1
Critical1
not blocked1
No public exploit1
Q1 162
Not applicable2
Medium2
not blocked2
Proof of concept only1
No public exploit1
Q2 162
Not applicable2
High1
Medium1
not blocked2
Working exploit published1
No public exploit1
Q4 12Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15Q2 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2016-2105 | High | 2016-05-05 | Not applicable | No public exploit | Integer overflow in the EVP_EncodeUpdate function in crypto/evp/encode.c in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h allows remote attackers to cause a denial of service (heap memory corruption) via a large amount of binary data. |
| CVE-2016-0702 | Medium | 2016-03-03 | Not applicable | No public exploit | The MOD_EXP_CTIME_COPY_FROM_PREBUF function in crypto/bn/bn_exp.c in OpenSSL 1.0.1 before 1.0.1s and 1.0.2 before 1.0.2g does not properly consider cache-bank access times during modular exponentiation, which makes it easier for local users to discover RSA keys by running a crafted application on the same Intel Sandy Bridge CPU core as a victim and leveraging cache-bank conflicts, aka a "CacheBleed" attack. |
| CVE-2016-0800 | Medium | 2016-03-01 | Not applicable | Proof of concept only | The SSLv2 protocol, as used in OpenSSL before 1.0.1s and 1.0.2 before 1.0.2g and other products, requires a server to send a ServerVerify message before establishing that a client possesses certain plaintext RSA data, which makes it easier for remote attackers to decrypt TLS ciphertext data by leveraging a Bleichenbacher RSA padding oracle, aka a "DROWN" attack. |
| CVE-2015-8104 | Critical | 2015-11-16 | Not applicable | No public exploit | The KVM subsystem in the Linux kernel through 4.2.6, and Xen 4.3.x through 4.6.x, allows guest OS users to cause a denial of service (host OS panic or hang) by triggering many #DB (aka Debug) exceptions, related to svm.c. |
| CVE-2015-5600 | High | 2015-08-03 | Not applicable | No public exploit | The kbdint_next_device function in auth2-chall.c in sshd in OpenSSH through 6.9 does not properly restrict the processing of keyboard-interactive devices within a single connection, which makes it easier for remote attackers to conduct brute-force attacks or cause a denial of service (CPU consumption) via a long and duplicative list in the ssh -oKbdInteractiveDevices option, as demonstrated by a modified client that provides a different password for each pam element on this list. |
| CVE-2015-3183 | Medium | 2015-07-20 | Not applicable | Forecast only | The chunked transfer coding implementation in the Apache HTTP Server before 2.4.14 does not properly parse chunk headers, which allows remote attackers to conduct HTTP request smuggling attacks via a crafted request, related to mishandling of large chunk-size values and invalid chunk-extension characters in modules/http/http_filters.c. |
| CVE-2015-3237 | Medium | 2015-06-22 | Not applicable | No public exploit | The smb_request_state function in cURL and libcurl 7.40.0 through 7.42.1 allows remote SMB servers to obtain sensitive information from memory or cause a denial of service (out-of-bounds read and crash) via crafted length and offset values. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |
| CVE-2015-0228 | Medium | 2015-03-08 | Not applicable | No public exploit | The lua_websocket_read function in lua_request.c in the mod_lua module in the Apache HTTP Server through 2.4.12 allows remote attackers to cause a denial of service (child-process crash) by sending a crafted WebSocket Ping frame after a Lua script has called the wsupgrade function. |
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |
| CVE-2014-3571 | Medium | 2015-01-09 | Not applicable | No public exploit | OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote attackers to cause a denial of service (NULL pointer dereference and application crash) via a crafted DTLS message that is processed with a different read operation for the handshake header than for the handshake body, related to the dtls1_get_record function in d1_pkt.c and the ssl3_read_n function in s3_pkt.c. |
| CVE-2013-2064 | Medium | 2013-06-15 | Not applicable | No public exploit | Integer overflow in X.org libxcb 1.9 and earlier allows X servers to trigger allocation of insufficient memory and a buffer overflow via vectors related to the read_packet function. |
| CVE-2012-3410 | Medium | 2012-08-27 | Not applicable | No public exploit | Stack-based buffer overflow in lib/sh/eaccess.c in GNU Bash before 4.2 patch 33 might allow local users to bypass intended restricted shell access via a long filename in /dev/fd, which is not properly handled when expanding the /dev/fd prefix. |