
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
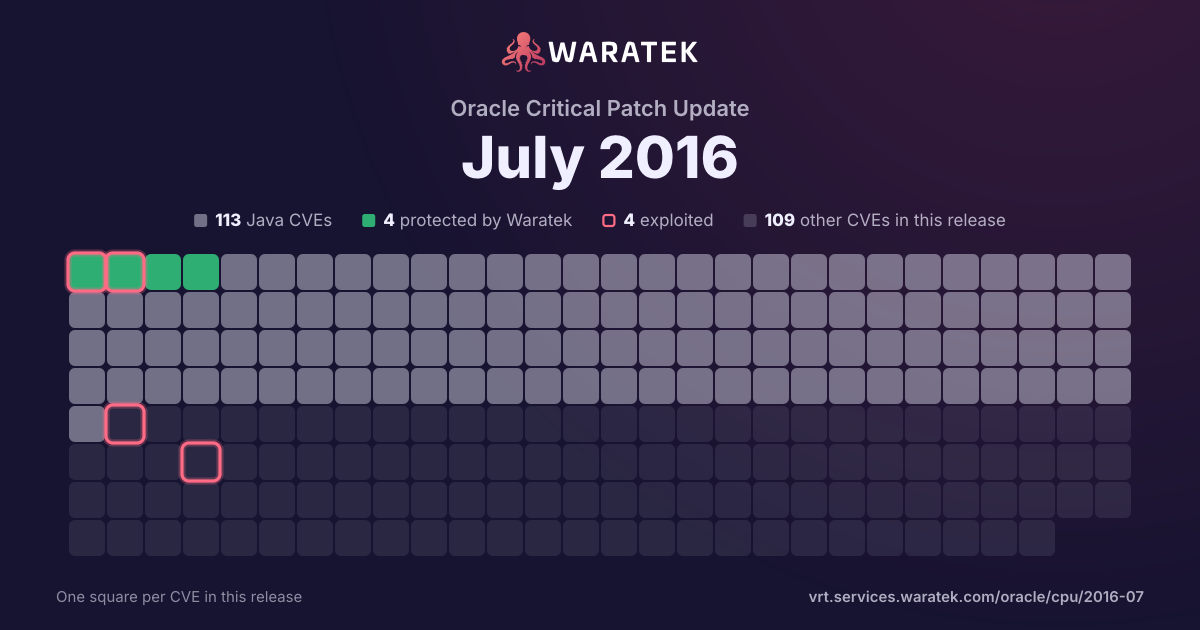
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 6 matches · 2 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 4 EPSS ≥ 0.5
Protected by Waratek
1
16.7%
Rule in development
0
0.0%
Mitigation candidate
1
16.7%
No exploit published
0
0.0%
Outside Waratek scope
3
50.0%
Not applicable
1
16.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
16.7%
partly blocked
0
0.0%
not blocked
5
83.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
6
100.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 2 / quarter
Q3 121
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Q4 120
Q1 130
Q2 130
Q3 130
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 151
Outside Waratek scope1
High1
not blocked1
Working exploit published1
Q2 150
Q3 151
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Q4 150
Q1 160
Q2 161
Not applicable1
Medium1
not blocked1
Working exploit published1
Q3 162
Protected by Waratek1
Mitigation candidate1
Critical1
Medium1
blocked by ARMR today1
not blocked1
Working exploit published2
Q3 12Q1 13Q3 13Q1 14Q3 14Q1 15Q3 15Q1 16Q3 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3542 | Medium | 2016-07-21 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Knowledge Management component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote administrators to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3510 | Critical | 2016-07-21 | Protected by Waratek | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components, a different vulnerability than CVE-2016-3586. |
| CVE-2016-2107 | Medium | 2016-05-05 | Not applicable | Working exploit published | The AES-NI implementation in OpenSSL before 1.0.1t and 1.0.2 before 1.0.2h does not consider memory allocation during a certain padding check, which allows remote attackers to obtain sensitive cleartext information via a padding-oracle attack against an AES CBC session. NOTE: this vulnerability exists because of an incorrect fix for CVE-2013-0169. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2012-3137 | Medium | 2012-09-21 | Outside Waratek scope | Working exploit published | The authentication protocol in Oracle Database Server 10.2.0.3, 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.2, and 11.2.0.3 allows remote attackers to obtain the session key and salt for arbitrary users, which leaks information about the cryptographic hash and makes it easier to conduct brute force password guessing attacks, aka "stealth password cracking vulnerability." |