
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
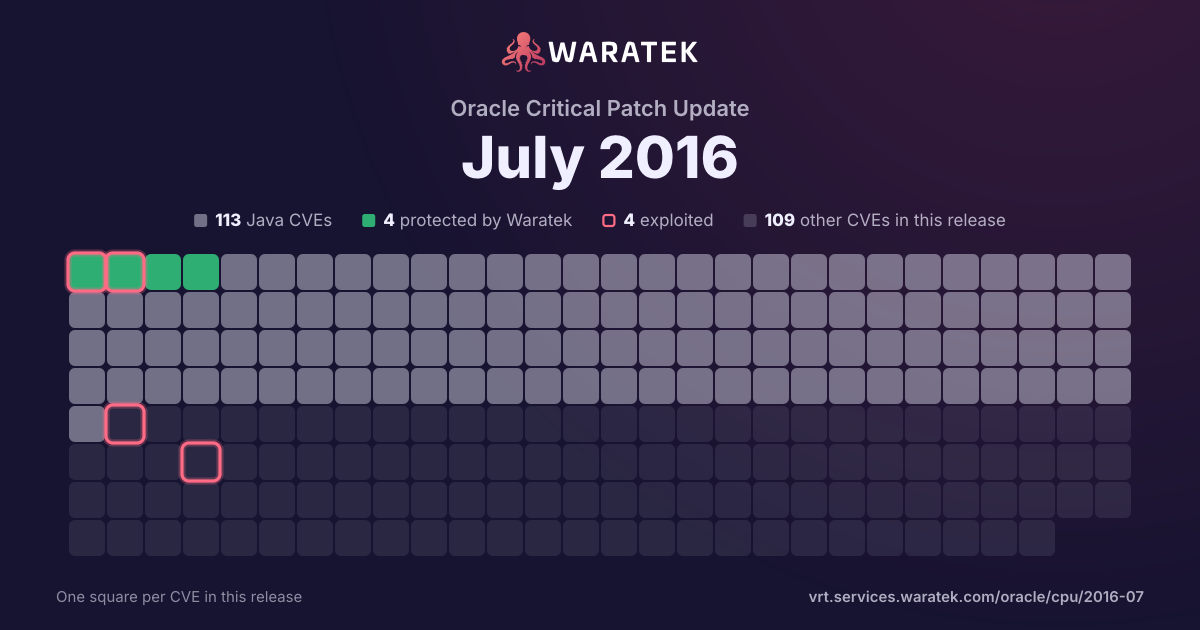
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 15 matches · 10 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
15matches
10in Waratek scope66.7%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
10
66.7%
Outside Waratek scope
2
13.3%
Not applicable
3
20.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
15
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
15
100.0%
split by
peak 15 / month
Jul 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-5473 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to File Folders / Attachment, a different vulnerability than CVE-2016-3537. |
| CVE-2016-5466 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote attackers to affect confidentiality via vectors related to Services, a different vulnerability than CVE-2016-3450 and CVE-2016-5460. |
| CVE-2016-5462 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote administrators to affect confidentiality via vectors related to Workspaces. |
| CVE-2016-5460 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote attackers to affect confidentiality via vectors related to Services, a different vulnerability than CVE-2016-3450 and CVE-2016-5466. |
| CVE-2016-5444 | Low | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.11 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows remote attackers to affect confidentiality via vectors related to Server: Connection. |
| CVE-2016-3531 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote authenticated users to affect confidentiality via vectors related to PC / Notification. |
| CVE-2016-3516 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Enterprise Communications Broker component in Oracle Communications Applications before PCz 2.0.0m4p1 allows remote authenticated users to affect confidentiality via vectors related to GUI, a different vulnerability than CVE-2016-3514. |
| CVE-2016-3490 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.3.0, 6.3.1, 6.3.2, 6.3.3, 6.3.4, 6.3.5, 6.3.6, 6.3.7, 6.4.0, and 6.4.1 allows remote authenticated users to affect confidentiality via vectors related to Database. |
| CVE-2016-3485 | Low | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u115, 7u101, and 8u92; Java SE Embedded 8u91; and JRockit R28.3.10 allows local users to affect integrity via vectors related to Networking. |
| CVE-2016-3484 | Low | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Database Vault component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows local users to affect confidentiality and integrity via unknown vectors. |
| CVE-2016-3482 | Low | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.9 and 12.1.3.0 allows remote attackers to affect confidentiality via vectors related to SSL/TLS Module. |
| CVE-2016-3474 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher (formerly XML Publisher) component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality via vectors related to Security. |
| CVE-2016-3469 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows local users to affect confidentiality via vectors related to Services. |
| CVE-2016-3452 | Low | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.5.48 and earlier, 5.6.29 and earlier, and 5.7.10 and earlier and MariaDB before 5.5.49, 10.0.x before 10.0.25, and 10.1.x before 10.1.14 allows remote attackers to affect confidentiality via vectors related to Server: Security: Encryption. |
| CVE-2016-3450 | Low | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server Framework component in Oracle Siebel CRM 8.1.1, 8.2.2, IP2014, IP2015, and IP2016 allows remote attackers to affect confidentiality via vectors related to Services, a different vulnerability than CVE-2016-5460 and CVE-2016-5466. |