
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
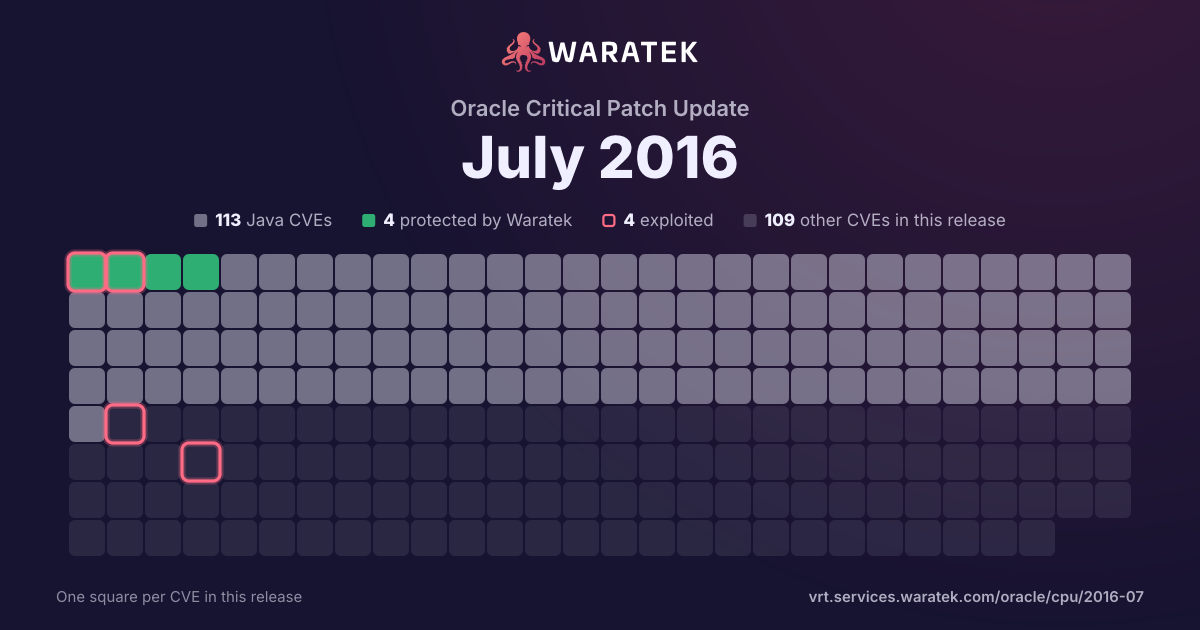
By status
5Protected by Waratek1Mitigation candidate116No exploit published16Outside Waratek scope84Not applicable
4Exploited, marked by the ring
No exploit published. For 112 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 13 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
13matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
13
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
13
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
13
100.0%
split by
peak 12 / month
Aug 15Sep 15Oct 15Nov 15Dec 15Jan 16Feb 16Mar 16Apr 16May 16Jun 16Jul 16
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3607 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3586 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components, a different vulnerability than CVE-2016-3510. |
| CVE-2016-3556 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to EM Integration. |
| CVE-2016-3546 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Collections component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Report JSPs. |
| CVE-2016-3543 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Tasks. |
| CVE-2016-3541 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Notes. |
| CVE-2016-3527 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Demand Planning component in Oracle Supply Chain Products Suite 12.1 and 12.2 allows remote attackers to affect confidentiality and integrity via vectors related to ODPDA Servlet. |
| CVE-2016-3504 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 11.1.2.4.0, 12.1.3.0.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to ADF Faces. |
| CVE-2016-3499 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0 and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3493 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Financial Reporting component in Oracle Hyperion 11.1.2.4 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Security Models. |
| CVE-2016-3468 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3444 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Integration Bus component in Oracle Retail Applications 13.0, 13.1, 13.2, 14.0, 14.1, and 15.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2015-3253 | Critical | 2015-08-13 | No exploit published | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |