
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
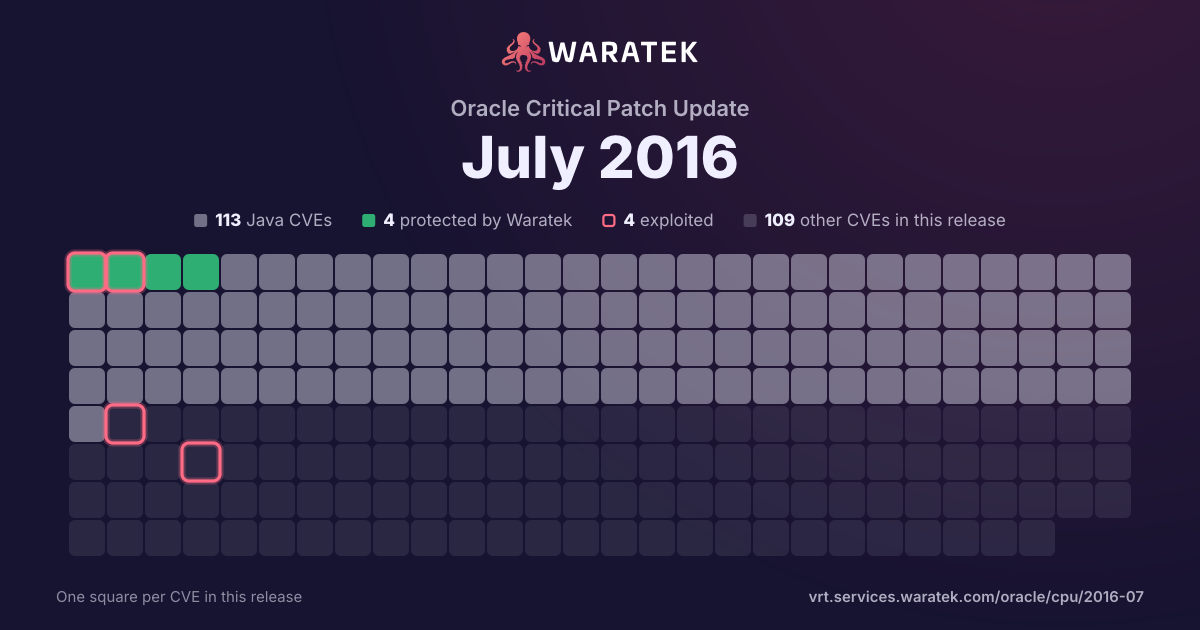
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 7 matches · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
7matches
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
7
100.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
7
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
7
100.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2016-3536 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Marketing component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Deliverables. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3535 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Remote Launch. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3532 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Inbound Telephony component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to SDK client integration. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue involves multiple cross-site scripting (XSS) vulnerabilities, which allow remote attackers to inject arbitrary web script or HTML via unspecified vectors. |
| CVE-2016-3528 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Internet Expenses component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect availability via vectors related to Expenses Admin Utilities. |
| CVE-2016-3522 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Applications Desktop Integrator component in Oracle E-Business Suite 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Application Service. |
| CVE-2016-3512 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Customer Interaction History component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Function Security. |
| CVE-2016-3491 | High | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle CRM Technical Foundation component in Oracle E-Business Suite 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Wireless Framework. NOTE: the previous information is from the July 2016 CPU. Oracle has not commented on third-party claims that this issue is a cross-site scripting (XSS) vulnerability, which allows remote attackers to inject arbitrary web script or HTML via unspecified vectors. |