
Oracle Critical Patch Update July 2016
Released July 2016 · Oracle's advisory ↗ · ← Critical Patch Update, April 2016 · Critical Patch Update, October 2016 →
222 CVEs in this release, one square each
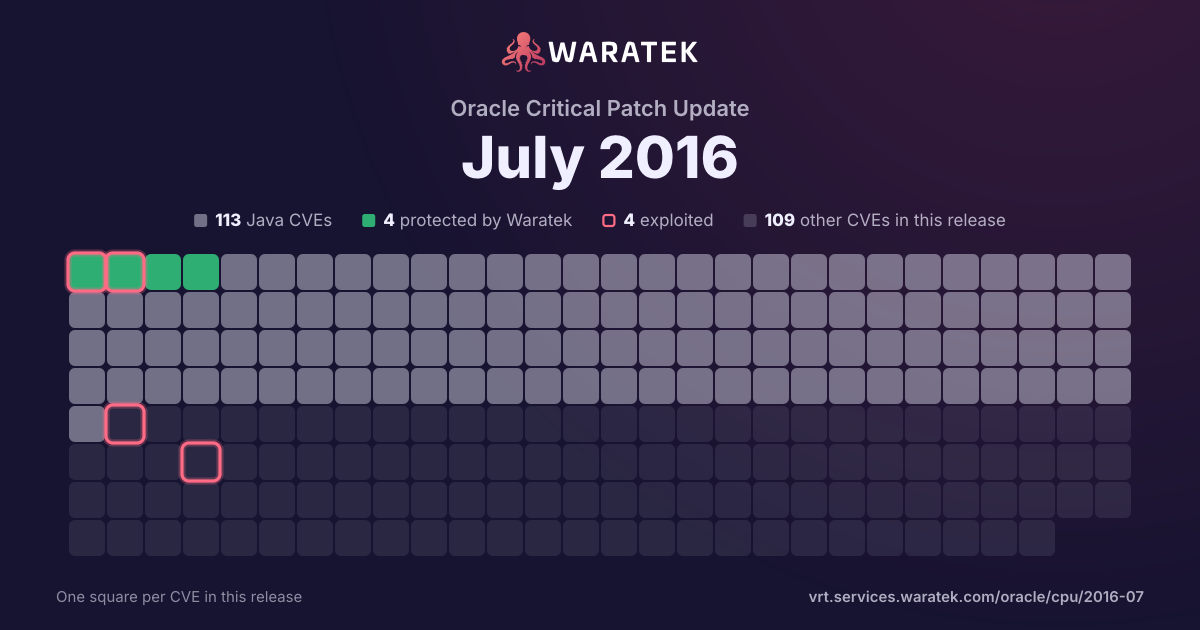
By status
4Protected by Waratek1Mitigation candidate108No exploit published30Outside Waratek scope79Not applicable
4Exploited, marked by the ring
No exploit published. For 108 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 24 matches · 14 in Waratek scope · 2 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
24matches
14in Waratek scope58.3%
2protected8.3%
1exploited4.2%
0CISA KEV0.0%
2public PoC8.3%
2EPSS ≥ 0.58.3%
Protected by Waratek
2
8.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
12
50.0%
Outside Waratek scope
7
29.2%
Not applicable
3
12.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
8.3%
partly blocked
0
0.0%
not blocked
22
91.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
4.2%
Working exploit published
1
4.2%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
22
91.7%
split by
peak 20 / quarter
Q3 151
Outside Waratek scope1
Critical1
not blocked1
No public exploit1
Q4 152
Outside Waratek scope1
Not applicable1
Critical2
not blocked2
No public exploit2
Q1 160
Q2 160
Q3 1620
Protected by Waratek1
No exploit published12
Outside Waratek scope5
Not applicable2
Critical20
blocked by ARMR today1
not blocked19
Working exploit published1
No public exploit19
Q4 160
Q1 170
Q2 170
Q3 170
Q4 171
Protected by Waratek1
Critical1
blocked by ARMR today1
Exploited1
Q3 15Q4 15Q1 16Q2 16Q3 16Q4 16Q1 17Q2 17Q3 17Q4 17
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-7501 | Critical | 2017-11-09 | Protected by Waratek | Exploited | Red Hat JBoss A-MQ 6.x; BPM Suite (BPMS) 6.x; BRMS 6.x and 5.x; Data Grid (JDG) 6.x; Data Virtualization (JDV) 6.x and 5.x; Enterprise Application Platform 6.x, 5.x, and 4.3.x; Fuse 6.x; Fuse Service Works (FSW) 6.x; Operations Network (JBoss ON) 3.x; Portal 6.x; SOA Platform (SOA-P) 5.x; Web Server (JWS) 3.x; Red Hat OpenShift/xPAAS 3.x; and Red Hat Subscription Asset Manager 1.3 allow remote attackers to execute arbitrary commands via a crafted serialized Java object, related to the Apache Commons Collections (ACC) library. |
| CVE-2016-5453 | Critical | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the ILOM component in Oracle Sun Systems Products Suite 3.0, 3.1, and 3.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to IPMI. |
| CVE-2016-3613 | Critical | 2016-07-21 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop component in Oracle Virtualization 4.63, 4.71, and 5.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to OpenSSL. |
| CVE-2016-3610 | Critical | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u92 and Java SE Embedded 8u91 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Libraries, a different vulnerability than CVE-2016-3598. |
| CVE-2016-3609 | Critical | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the OJVM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2016-3607 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 3.0.1 and 3.1.2 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3606 | Critical | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u101 and 8u92 and Java SE Embedded 8u91 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Hotspot. |
| CVE-2016-3598 | Critical | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u92 and Java SE Embedded 8u91 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Libraries, a different vulnerability than CVE-2016-3610. |
| CVE-2016-3587 | Critical | 2016-07-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u92 and Java SE Embedded 8u91 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Hotspot. |
| CVE-2016-3586 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components, a different vulnerability than CVE-2016-3510. |
| CVE-2016-3556 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.4 and 9.3.5 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to EM Integration. |
| CVE-2016-3546 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Advanced Collections component in Oracle E-Business Suite 12.1.1, 12.1.2, and 12.1.3 allows remote attackers to affect confidentiality and integrity via vectors related to Report JSPs. |
| CVE-2016-3543 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Tasks. |
| CVE-2016-3541 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Common Applications Calendar component in Oracle E-Business Suite 12.1.1, 12.1.2, 12.1.3, 12.2.3, 12.2.4, and 12.2.5 allows remote attackers to affect confidentiality and integrity via vectors related to Notes. |
| CVE-2016-3527 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Demand Planning component in Oracle Supply Chain Products Suite 12.1 and 12.2 allows remote attackers to affect confidentiality and integrity via vectors related to ODPDA Servlet. |
| CVE-2016-3510 | Critical | 2016-07-21 | Protected by Waratek | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.3.0, and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components, a different vulnerability than CVE-2016-3586. |
| CVE-2016-3504 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.1.9.0, 11.1.2.4.0, 12.1.3.0.0, and 12.2.1.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to ADF Faces. |
| CVE-2016-3499 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 12.1.3.0 and 12.2.1.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Web Container. |
| CVE-2016-3493 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Financial Reporting component in Oracle Hyperion 11.1.2.4 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Security Models. |
| CVE-2016-3468 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Engineering Data Management component in Oracle Supply Chain Products Suite 6.1.3.0 and 6.2.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2016-3444 | Critical | 2016-07-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Integration Bus component in Oracle Retail Applications 13.0, 13.1, 13.2, 14.0, 14.1, and 15.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to Install. |
| CVE-2015-8104 | Critical | 2015-11-16 | Not applicable | No public exploit | The KVM subsystem in the Linux kernel through 4.2.6, and Xen 4.3.x through 4.6.x, allows guest OS users to cause a denial of service (host OS panic or hang) by triggering many #DB (aka Debug) exceptions, related to svm.c. |
| CVE-2015-7182 | Critical | 2015-11-05 | Outside Waratek scope | No public exploit | Heap-based buffer overflow in the ASN.1 decoder in Mozilla Network Security Services (NSS) before 3.19.2.1 and 3.20.x before 3.20.1, as used in Firefox before 42.0 and Firefox ESR 38.x before 38.4 and other products, allows remote attackers to cause a denial of service (application crash) or possibly execute arbitrary code via crafted OCTET STRING data. |
| CVE-2015-3253 | Critical | 2015-08-13 | Outside Waratek scope | No public exploit | The MethodClosure class in runtime/MethodClosure.java in Apache Groovy 1.7.0 through 2.4.3 allows remote attackers to execute arbitrary code or cause a denial of service via a crafted serialized object. |