
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
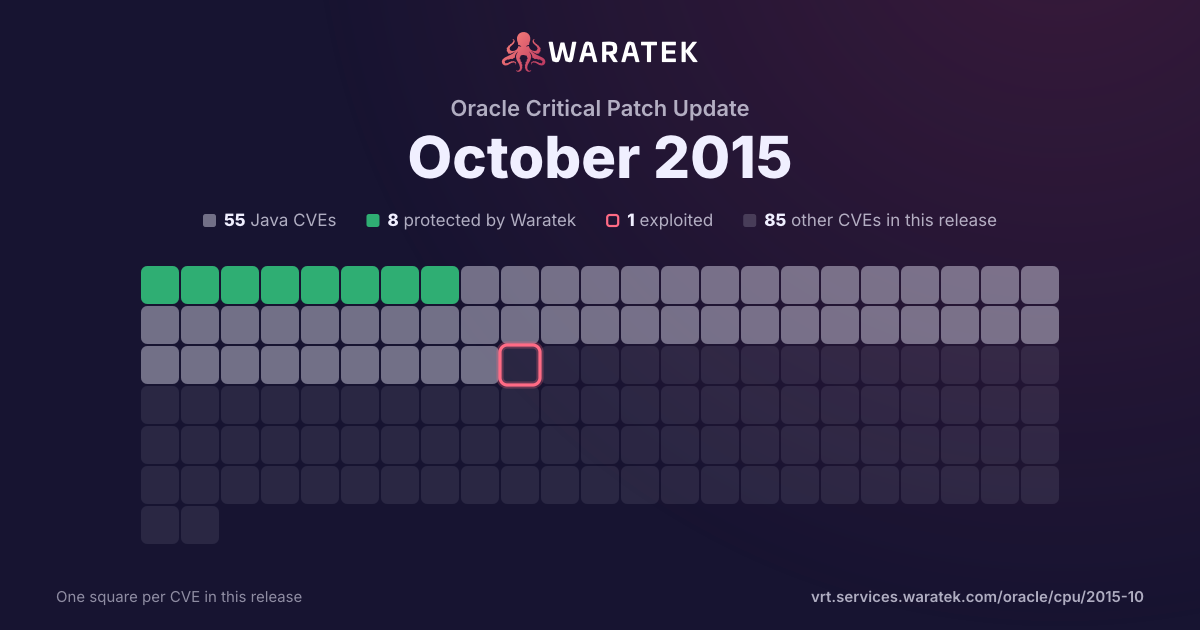
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 2 matches · 1 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
2matches
1in Waratek scope50.0%
1protected50.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC50.0%
1EPSS ≥ 0.550.0%
Protected by Waratek
1
50.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
50.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
50.0%
partly blocked
0
0.0%
not blocked
1
50.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
50.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
50.0%
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-3576 | High | 2015-08-14 | Protected by Waratek | No public exploit | The processControlCommand function in broker/TransportConnection.java in Apache ActiveMQ before 5.11.0 allows remote attackers to cause a denial of service (shutdown) via a shutdown command. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |