
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
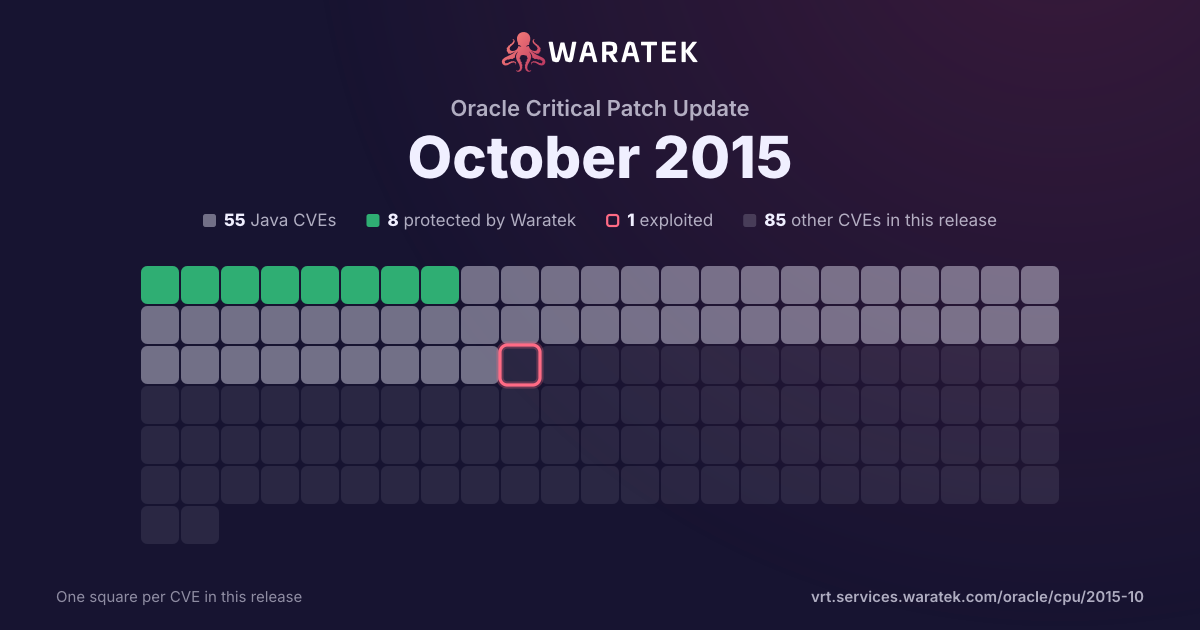
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 129 matches · 53 in Waratek scope · 7 protected · 1 exploited · 1 CISA KEV · 4 public PoC · 1 EPSS ≥ 0.5
129matches
53in Waratek scope41.1%
7protected5.4%
1exploited0.8%
1CISA KEV0.8%
4public PoC3.1%
1EPSS ≥ 0.50.8%
Protected by Waratek
7
5.4%
Rule in development
0
0.0%
Mitigation candidate
2
1.6%
No exploit published
44
34.1%
Outside Waratek scope
31
24.0%
Not applicable
45
34.9%
Withdrawn CVE
0
0.0%
blocked by ARMR today
7
5.4%
partly blocked
0
0.0%
not blocked
122
94.6%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
0.8%
Working exploit published
4
3.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
124
96.1%
split by
peak 126 / month
Jun 151
Not applicable1
Medium1
not blocked1
No public exploit1
Jul 151
Outside Waratek scope1
Medium1
not blocked1
Working exploit published1
Aug 151
Protected by Waratek1
High1
blocked by ARMR today1
No public exploit1
Sep 150
Oct 15126
Protected by Waratek6
Mitigation candidate2
No exploit published44
Outside Waratek scope30
Not applicable44
High20
Medium76
Low30
blocked by ARMR today6
not blocked120
Exploited1
Working exploit published3
No public exploit122
Jun 15Jul 15Aug 15Sep 15Oct 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4809 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.5.0, 8.5.1, and 8.5.2 allows local users to affect availability via vectors related to Outside In PDF Export SDK, a different vulnerability than CVE-2015-4811. |
| CVE-2015-4807 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier, when running on Windows, allows remote authenticated users to affect availability via unknown vectors related to Server : Query Cache. |
| CVE-2015-4806 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality and integrity via unknown vectors related to Libraries. |
| CVE-2015-4805 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Serialization. |
| CVE-2015-4804 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HCM Talent Acquisition Management component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2015-4803 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60; Java SE Embedded 8u51; and JRockit R28.3.7 allows remote attackers to affect availability via vectors related to JAXP, a different vulnerability than CVE-2015-4893 and CVE-2015-4911. |
| CVE-2015-4802 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Partition, a different vulnerability than CVE-2015-4792. |
| CVE-2015-4801 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 11.2 allows local users to affect confidentiality via unknown vectors related to Solaris Kernel Zones. |
| CVE-2015-4800 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Optimizer. |
| CVE-2015-4799 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Sites component in Oracle Fusion Middleware 7.6.2, 11.1.1.6.1, and 11.1.1.8.0 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2015-4798 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology Stack component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to DB Listener, a different vulnerability than CVE-2015-4839. |
| CVE-2015-4797 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM component in Oracle Supply Chain Products Suite 9.3.3 allows remote authenticated users to affect integrity via unknown vectors related to Security. |
| CVE-2015-4796 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2, when running on Windows, allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2015-4888. |
| CVE-2015-4795 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Utilities Work and Asset Management component in Oracle Industry Applications 1.9.1.1.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Add-On Applications. |
| CVE-2015-4794 | High | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java VM component in Oracle Database Server 11.2.0.4, 12.1.0.1, and 12.1.0.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2015-4793 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Communications Convergence component in Oracle Communications Applications 2.0 and 3.0.1 allows remote attackers to affect confidentiality via unknown vectors related to Mail Proxy. |
| CVE-2015-4792 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.5.45 and earlier and 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Partition, a different vulnerability than CVE-2015-4802. |
| CVE-2015-4791 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.26 and earlier allows remote authenticated users to affect availability via unknown vectors related to Server : Security : Privileges. |
| CVE-2015-4766 | Low | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.25 and earlier allows local users to affect availability via unknown vectors related to Server : Security : Firewall. |
| CVE-2015-4762 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications DBA component in Oracle E-Business Suite 12.2.3 and 12.2.4 allows remote authenticated users to affect confidentiality via unknown vectors related to Online patching. |
| CVE-2015-4734 | Medium | 2015-10-21 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85 and 8u60, and Java SE Embedded 8u51, allows remote attackers to affect confidentiality via vectors related to JGSS. |
| CVE-2015-4730 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL 5.6.20 and earlier allows remote authenticated users to affect availability via unknown vectors related to Types. |
| CVE-2015-2642 | Medium | 2015-10-21 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 and 11.2 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Gzip. |
| CVE-2015-2633 | Low | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Ops Center component in Oracle Enterprise Manager Grid Control 12.1.0.1 and 12.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Ops Center. |
| CVE-2015-2608 | High | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in (1) the Oracle Communications Diameter Signaling Router (DSR) component in Oracle Communications Applications 4.1.6 and earlier, 5.1.0 and earlier, 6.0.2 and earlier, and 7.1.0 and earlier; (2) the Oracle Communications Performance Intelligence Center Software component in Oracle Communications Applications 9.0.3 and earlier and 10.1.5 and earlier; (3) the Oracle Communications Policy Management component in Oracle Communications Applications 9.9.0 and earlier, 10.5.0 and earlier, 11.5.0 and earlier, and 12.1.0 and earlier; and (4) the Oracle Communications Tekelec HLR Router component in Oracle Communications Applications 4.0.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to PMAC. |
| CVE-2015-1829 | Medium | 2015-10-21 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 10.1.3.5, 11.1.1.7, 11.1.1.9, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect availability via unknown vectors related to Web Listener. |
| CVE-2014-3576 | High | 2015-08-14 | Protected by Waratek | No public exploit | The processControlCommand function in broker/TransportConnection.java in Apache ActiveMQ before 5.11.0 allows remote attackers to cause a denial of service (shutdown) via a shutdown command. |
| CVE-2015-1793 | Medium | 2015-07-09 | Outside Waratek scope | Working exploit published | The X509_verify_cert function in crypto/x509/x509_vfy.c in OpenSSL 1.0.1n, 1.0.1o, 1.0.2b, and 1.0.2c does not properly process X.509 Basic Constraints cA values during identification of alternative certificate chains, which allows remote attackers to spoof a Certification Authority role and trigger unintended certificate verifications via a valid leaf certificate. |
| CVE-2015-1791 | Medium | 2015-06-12 | Not applicable | No public exploit | Race condition in the ssl3_get_new_session_ticket function in ssl/s3_clnt.c in OpenSSL before 0.9.8zg, 1.0.0 before 1.0.0s, 1.0.1 before 1.0.1n, and 1.0.2 before 1.0.2b, when used for a multi-threaded client, allows remote attackers to cause a denial of service (double free and application crash) or possibly have unspecified other impact by providing a NewSessionTicket during an attempt to reuse a ticket that had been obtained earlier. |