
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
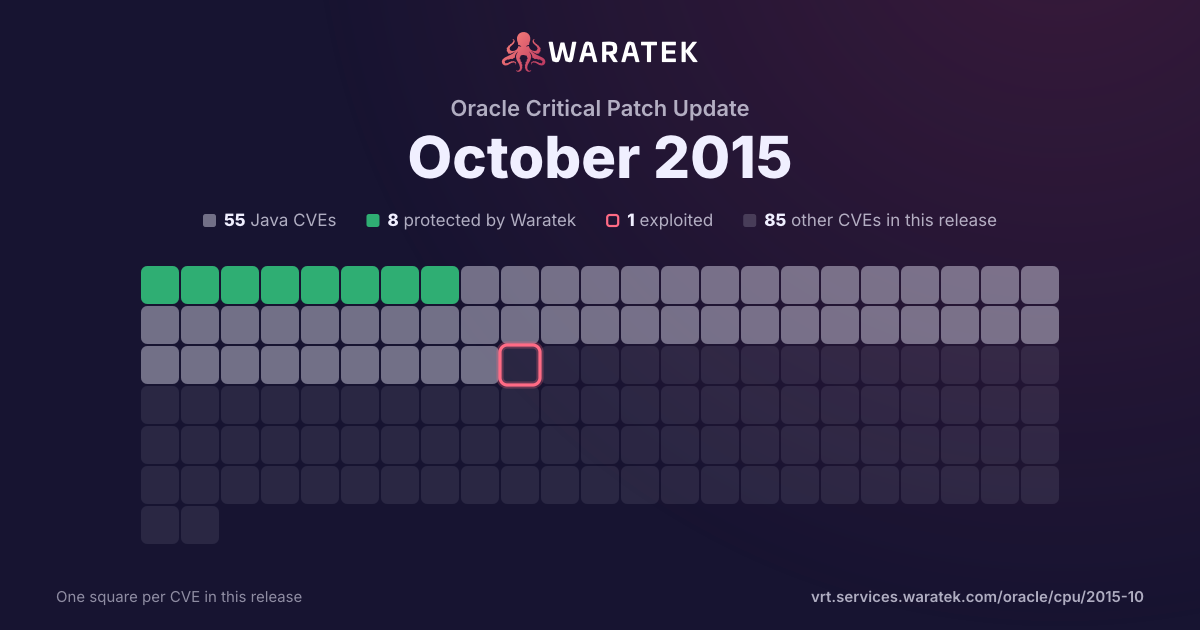
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 2 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
4matches
2in Waratek scope50.0%
1protected25.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC50.0%
2EPSS ≥ 0.550.0%
Protected by Waratek
1
25.0%
Rule in development
0
0.0%
Mitigation candidate
1
25.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
25.0%
partly blocked
0
0.0%
not blocked
3
75.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
50.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
2
50.0%
split by
peak 2 / year
19991
Not applicable1
Medium1
not blocked1
No public exploit1
20000
20010
20020
20030
20040
20050
20060
20070
20080
20090
20101
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
20110
20120
20130
20142
Mitigation candidate1
Not applicable1
High2
not blocked2
Working exploit published1
No public exploit1
20002002200420062008201020122014
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-1569 | High | 2014-12-15 | Not applicable | No public exploit | The definite_length_decoder function in lib/util/quickder.c in Mozilla Network Security Services (NSS) before 3.16.2.4 and 3.17.x before 3.17.3 does not ensure that the DER encoding of an ASN.1 length is properly formed, which allows remote attackers to conduct data-smuggling attacks by using a long byte sequence for an encoding, as demonstrated by the SEC_QuickDERDecodeItem function's improper handling of an arbitrary-length encoding of 0x00. |
| CVE-2014-0050 | High | 2014-04-01 | Mitigation candidate | Working exploit published | MultipartStream.java in Apache Commons FileUpload before 1.3.1, as used in Apache Tomcat, JBoss Web, and other products, allows remote attackers to cause a denial of service (infinite loop and CPU consumption) via a crafted Content-Type header that bypasses a loop's intended exit conditions. |
| CVE-2010-1622 | Medium | 2010-06-21 | Protected by Waratek | Working exploit published | SpringSource Spring Framework 2.5.x before 2.5.6.SEC02, 2.5.7 before 2.5.7.SR01, and 3.0.x before 3.0.3 allows remote attackers to execute arbitrary code via an HTTP request containing class.classLoader.URLs[0]=jar: followed by a URL of a crafted .jar file. |
| CVE-1999-0377 | Medium | 1999-02-22 | Not applicable | No public exploit | Process table attack in Unix systems allows a remote attacker to perform a denial of service by filling a machine's process tables through multiple connections to network services. |