
Oracle Critical Patch Update October 2015
Released October 2015 · Oracle's advisory ↗ · ← Critical Patch Update, July 2015 · Critical Patch Update, January 2016 →
140 CVEs in this release, one square each
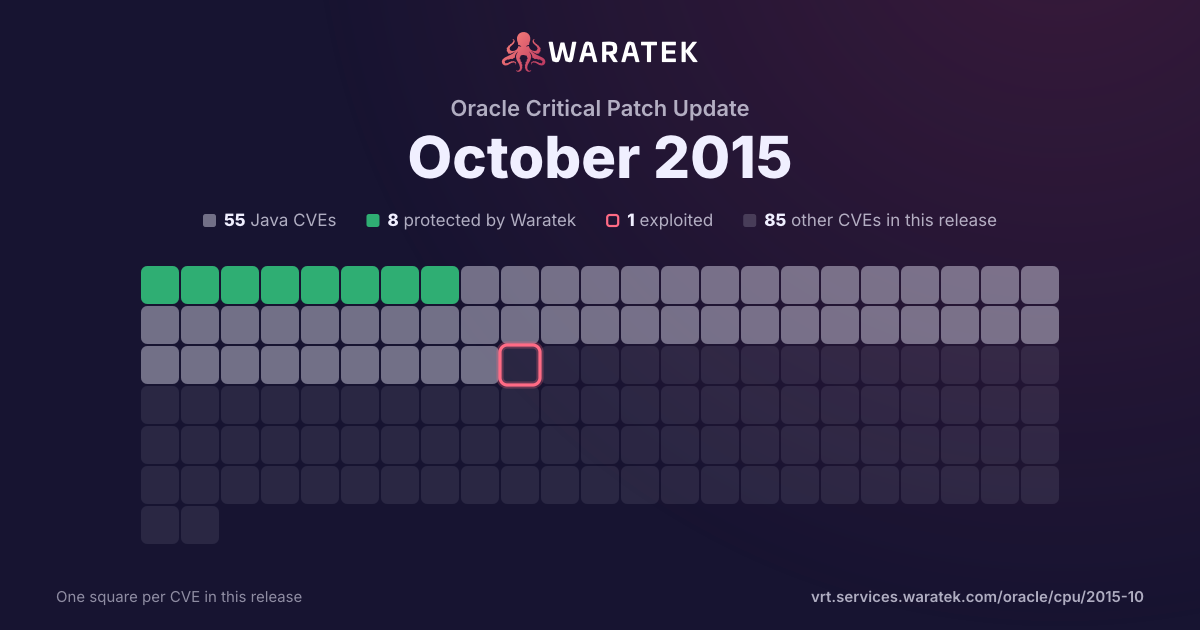
By status
8Protected by Waratek3Mitigation candidate44No exploit published34Outside Waratek scope51Not applicable
1Exploited, marked by the ring
No exploit published. For 44 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 5 matches · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
5
100.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
blocked by ARMR today
5
100.0%
partly blocked
0
0.0%
not blocked
0
0.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
20.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
4
80.0%
split by
peak 4 / quarter
Q2 101
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
Q3 100
Q4 100
Q1 110
Q2 110
Q3 110
Q4 110
Q1 120
Q2 120
Q3 120
Q4 120
Q1 130
Q2 130
Q3 130
Q4 130
Q1 140
Q2 140
Q3 140
Q4 140
Q1 150
Q2 150
Q3 150
Q4 154
Protected by Waratek4
Medium4
blocked by ARMR today4
No public exploit4
Q2 10Q4 10Q2 11Q4 11Q2 12Q4 12Q2 13Q4 13Q2 14Q4 14Q2 15Q4 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-4886 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Report Manager component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Reports Security. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to read arbitrary files, cause a denial of service, or conduct SMB Relay attacks via a crafted DTD in an XML request involving the OA_HTML/copxml servlet. |
| CVE-2015-4872 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u101, 7u85, and 8u60; Java SE Embedded 8u51; and JRockit R28.3.7 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2015-4851 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle iSupplier Portal component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to XML input. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to read arbitrary files, cause a denial of service, or conduct SMB Relay attacks via a crafted DTD in an XML request to OA_HTML/oramipp_lpr. |
| CVE-2015-4849 | Medium | 2015-10-21 | Protected by Waratek | No public exploit | Unspecified vulnerability in the Oracle Payments component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Punch-in. NOTE: the previous information is from the October 2015 CPU. Oracle has not commented on third-party claims that this issue is an XML External Entity (XXE) vulnerability, which allows remote attackers to cause a denial of service or conduct SMB Relay attacks via a crafted DTD in an XML request to OA_HTML/IspPunchInServlet. |
| CVE-2010-1622 | Medium | 2010-06-21 | Protected by Waratek | Working exploit published | SpringSource Spring Framework 2.5.x before 2.5.6.SEC02, 2.5.7 before 2.5.7.SR01, and 3.0.x before 3.0.3 allows remote attackers to execute arbitrary code via an HTTP request containing class.classLoader.URLs[0]=jar: followed by a URL of a crafted .jar file. |