
Oracle Critical Patch Update April 2015
Released April 2015 · Oracle's advisory ↗ · ← Critical Patch Update, January 2015 · Critical Patch Update, July 2015 →
93 CVEs in this release, one square each
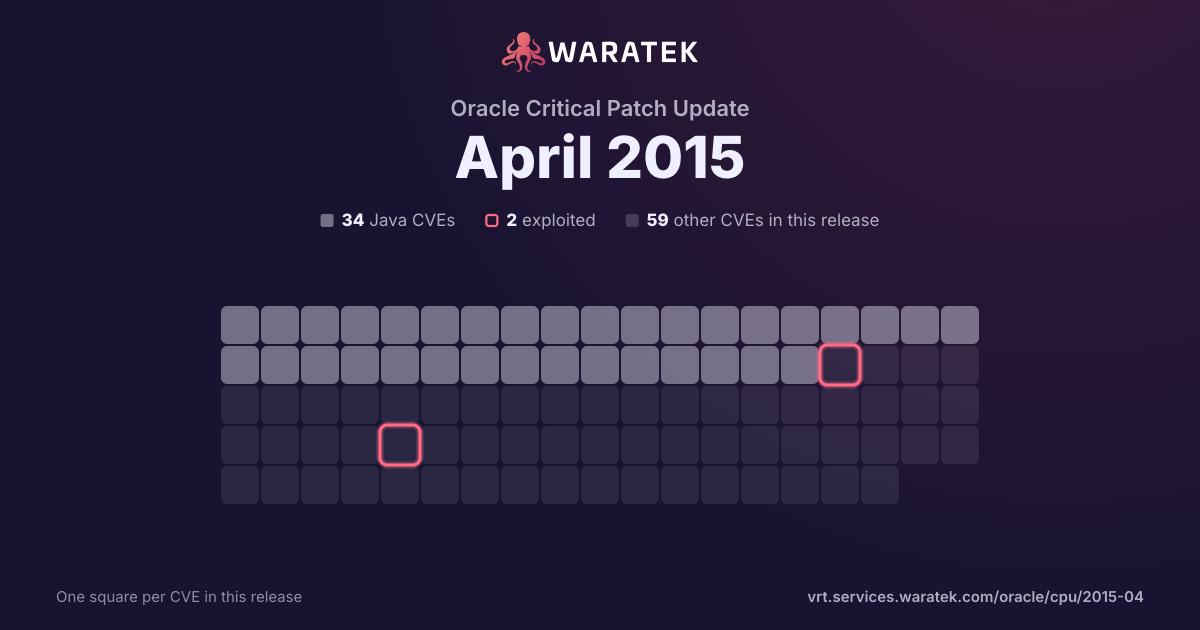
By status
3Mitigation candidate31No exploit published27Outside Waratek scope32Not applicable
2Exploited, marked by the ring
No exploit published. For 29 of them, Oracle's security advisory is the source of public detail.
Overview 8 matches · 3 in Waratek scope · 0 protected · 2 exploited · 0 CISA KEV · 5 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
3
37.5%
No exploit published
0
0.0%
Outside Waratek scope
3
37.5%
Not applicable
2
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
8
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
25.0%
Working exploit published
5
62.5%
Proof of concept only
1
12.5%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 3 / month
Apr 142
Mitigation candidate1
Outside Waratek scope1
High2
not blocked2
Exploited1
Working exploit published1
May 140
Jun 140
Jul 140
Aug 140
Sep 140
Oct 141
Outside Waratek scope1
Low1
not blocked1
Proof of concept only1
Nov 140
Dec 140
Jan 152
Outside Waratek scope1
Not applicable1
High1
Medium1
not blocked2
Exploited1
Working exploit published1
Feb 150
Mar 150
Apr 153
Mitigation candidate2
Not applicable1
Medium1
Low2
not blocked3
Working exploit published3
Apr 14Jun 14Aug 14Oct 14Dec 14Feb 15Apr 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-2572 | Medium | 2015-04-16 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle Hyperion Smart View for Office component in Oracle Hyperion 11.1.2.5.216 and earlier, when running on Windows, allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core. |
| CVE-2015-0493 | Low | 2015-04-16 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.1, 8.5.0, and 8.5.1 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-0474. |
| CVE-2015-0474 | Low | 2015-04-16 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.1, 8.5.0, and 8.5.1 allows local users to affect availability via unknown vectors related to Outside In Filters, a different vulnerability than CVE-2015-0493. |
| CVE-2015-0235 | High | 2015-01-28 | Outside Waratek scope | Working exploit published | Heap-based buffer overflow in the __nss_hostname_digits_dots function in glibc 2.2, and other 2.x versions before 2.18, allows context-dependent attackers to execute arbitrary code via vectors related to the (1) gethostbyname or (2) gethostbyname2 function, aka "GHOST." |
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |
| CVE-2014-3566 | Low | 2014-10-15 | Outside Waratek scope | Proof of concept only | The SSL protocol 3.0, as used in OpenSSL through 1.0.1i and other products, uses nondeterministic CBC padding, which makes it easier for man-in-the-middle attackers to obtain cleartext data via a padding-oracle attack, aka the "POODLE" issue. |
| CVE-2014-0112 | High | 2014-04-29 | Outside Waratek scope | Exploited | ParametersInterceptor in Apache Struts before 2.3.20 does not properly restrict access to the getClass method, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via a crafted request. NOTE: this vulnerability exists because of an incomplete fix for CVE-2014-0094. |
| CVE-2014-0050 | High | 2014-04-01 | Mitigation candidate | Working exploit published | MultipartStream.java in Apache Commons FileUpload before 1.3.1, as used in Apache Tomcat, JBoss Web, and other products, allows remote attackers to cause a denial of service (infinite loop and CPU consumption) via a crafted Content-Type header that bypasses a loop's intended exit conditions. |