
Oracle Critical Patch Update April 2015
Released April 2015 · Oracle's advisory ↗ · ← Critical Patch Update, January 2015 · Critical Patch Update, July 2015 →
93 CVEs in this release, one square each
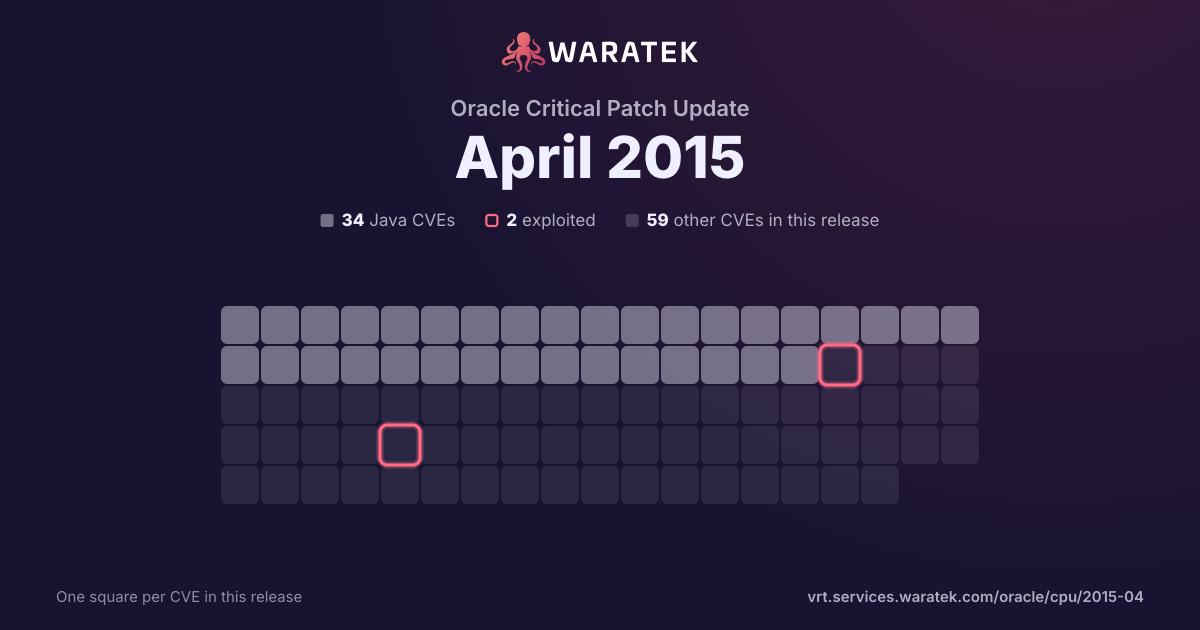
By status
4Mitigation candidate40No exploit published16Outside Waratek scope33Not applicable
2Exploited, marked by the ring
No exploit published. For 35 of them, Oracle's security advisory is the source of public detail.
Overview 3 matches · 0 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 2 EPSS ≥ 0.5
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
2
66.7%
No exploit published
1
33.3%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
3
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
33.3%
Working exploit published
1
33.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
1
33.3%
split by
peak 2 / month
Feb 14Mar 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0112 | High | 2014-04-29 | Mitigation candidate | Exploited | ParametersInterceptor in Apache Struts before 2.3.20 does not properly restrict access to the getClass method, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via a crafted request. NOTE: this vulnerability exists because of an incomplete fix for CVE-2014-0094. |
| CVE-2014-0050 | High | 2014-04-01 | Mitigation candidate | Working exploit published | MultipartStream.java in Apache Commons FileUpload before 1.3.1, as used in Apache Tomcat, JBoss Web, and other products, allows remote attackers to cause a denial of service (infinite loop and CPU consumption) via a crafted Content-Type header that bypasses a loop's intended exit conditions. |
| CVE-2013-4286 | Medium | 2014-02-26 | No exploit published | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |