
Oracle Critical Patch Update April 2015
Released April 2015 · Oracle's advisory ↗ · ← Critical Patch Update, January 2015 · Critical Patch Update, July 2015 →
93 CVEs in this release, one square each
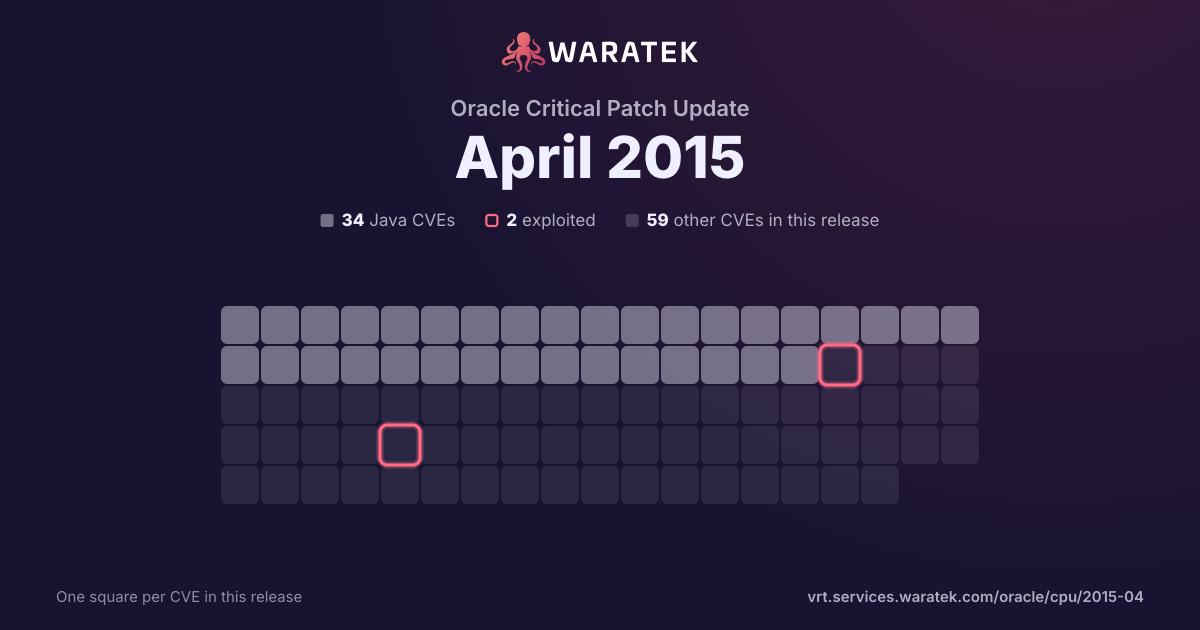
By status
3Mitigation candidate31No exploit published27Outside Waratek scope32Not applicable
2Exploited, marked by the ring
No exploit published. For 29 of them, Oracle's security advisory is the source of public detail.
Overview 2 matches · 0 in Waratek scope · 0 protected · 0 CISA KEV
2matches
0in Waratek scope0.0%
0protected0.0%
0CISA KEV0.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
50.0%
Not applicable
1
50.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
2
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
100.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
0
0.0%
split by
peak 1 / month
Apr 14May 14Jun 14Jul 14Aug 14Sep 14Oct 14Nov 14Dec 14Jan 15
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2015-0204 | Medium | 2015-01-09 | Not applicable | Exploited | The ssl3_get_key_exchange function in s3_clnt.c in OpenSSL before 0.9.8zd, 1.0.0 before 1.0.0p, and 1.0.1 before 1.0.1k allows remote SSL servers to conduct RSA-to-EXPORT_RSA downgrade attacks and facilitate brute-force decryption by offering a weak ephemeral RSA key in a noncompliant role, related to the "FREAK" issue. NOTE: the scope of this CVE is only client code based on OpenSSL, not EXPORT_RSA issues associated with servers or other TLS implementations. |
| CVE-2014-0112 | High | 2014-04-29 | Outside Waratek scope | Exploited | ParametersInterceptor in Apache Struts before 2.3.20 does not properly restrict access to the getClass method, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via a crafted request. NOTE: this vulnerability exists because of an incomplete fix for CVE-2014-0094. |