
Oracle Critical Patch Update October 2014
Released October 2014 · Oracle's advisory ↗ · ← Critical Patch Update, July 2014 · Critical Patch Update, January 2015 →
137 CVEs in this release, one square each
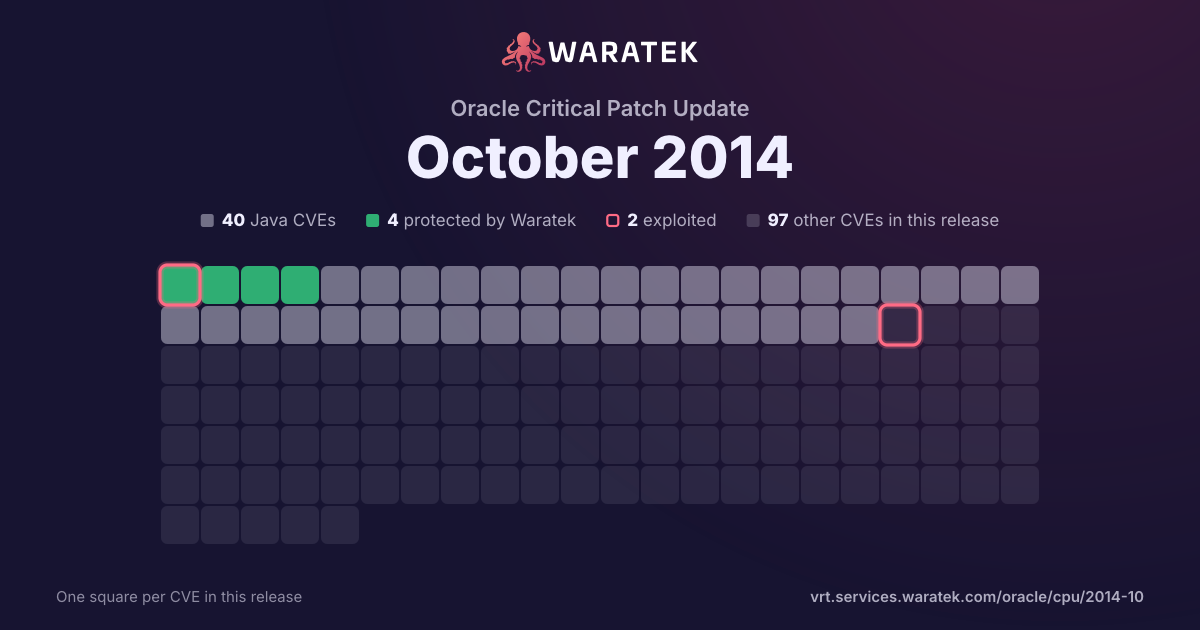
By status
4Protected by Waratek1Mitigation candidate35No exploit published60Outside Waratek scope37Not applicable
2Exploited, marked by the ring
No exploit published. For 32 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 31 matches · 3 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
3
9.7%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
28
90.3%
blocked by ARMR today
3
9.7%
partly blocked
0
0.0%
not blocked
28
90.3%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
1
3.2%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
30
96.8%
split by
peak 29 / month
Apr 141
Protected by Waratek1
Medium1
blocked by ARMR today1
Working exploit published1
May 141
Protected by Waratek1
Medium1
blocked by ARMR today1
No public exploit1
Jun 140
Jul 140
Aug 140
Sep 140
Oct 1429
Protected by Waratek1
No exploit published28
Medium29
blocked by ARMR today1
not blocked28
No public exploit29
Apr 14May 14Jun 14Jul 14Aug 14Sep 14Oct 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-6561 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Payments component in Oracle E-Business Suite 12.0.4, 12.0.6, 12.1.1, 12.1.2, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect confidentiality via unknown vectors related to Separate Remittance Advice. |
| CVE-2014-6557 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Application Performance Management component in Oracle Enterprise Manager Grid Control before 12.1.0.6.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to End User Experience Management. |
| CVE-2014-6554 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.2.1 and 11.1.2.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Admin Console. |
| CVE-2014-6553 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5 and 11.1.1.7 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Admin Console. |
| CVE-2014-6552 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5, 11.1.1.7, 11.1.2.1, and 11.1.2.2 allows remote attackers to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-6550 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Object Library component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect integrity via unknown vectors related to iHelp. |
| CVE-2014-6539 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via vectors related to LOV, a different vulnerability than CVE-2014-6472. |
| CVE-2014-6535 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52, 8.53, and 8.54 allows remote attackers to affect confidentiality and integrity via vectors related to SECURITY. |
| CVE-2014-6534 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, 12.1.2.0, and 12.1.3.0 allows remote authenticated users to affect integrity via vectors related to WLS Console. |
| CVE-2014-6533 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1 and 6.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security. |
| CVE-2014-6523 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote authenticated users to affect confidentiality via vectors related to REST Interface. |
| CVE-2014-6522 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7, 11.1.2.4, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect integrity via vectors related to ADF Faces. |
| CVE-2014-6517 | Medium | 2014-10-15 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 6u81, 7u67, and 8u20; Java SE Embedded 7u60; and Jrockit R27.8.3 and R28.3.3 allows remote attackers to affect confidentiality via vectors related to JAXP. |
| CVE-2014-6516 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the JD Edwards EnterpriseOne Tools component in Oracle JD Edwards Products 8.98 allows local users to affect confidentiality, integrity, and availability via vectors related to Installation SEC. |
| CVE-2014-6512 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u71, 6u81, 7u67, and 8u20; Java SE Embedded 7u60; and JRockit R27.8.3 and R28.3.3 allows remote attackers to affect integrity via unknown vectors related to Libraries. |
| CVE-2014-6499 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, 12.1.2.0, and 12.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to WebLogic Tuxedo Connector. |
| CVE-2014-6498 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, 6.3, 6.3.1, 6.3.2, 6.3.3, 6.3.4, and 6.3.5 allows remote attackers to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-6486 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HRMS component in Oracle PeopleSoft Products 9.2 allows remote authenticated users to affect integrity via unknown vectors related to Talent Acquisition Manager - Security. |
| CVE-2014-6482 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.53 and 8.54 allows remote authenticated users to affect integrity via unknown vectors related to Updates Change Assistant. |
| CVE-2014-6479 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology component in Oracle E-Business Suite 11.5.10.2, 12.0.6, and 12.1.3 allows remote authenticated users to affect confidentiality via vectors related to OC4J Configuration. |
| CVE-2014-6472 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via vectors related to LOV, a different vulnerability than CVE-2014-6539. |
| CVE-2014-6471 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via vectors related to OAM Diagnostics. |
| CVE-2014-6468 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 8u20 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-6465 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Communications Session Border Controller component in Oracle Communications Applications SCX640m5 allows remote authenticated users to affect availability via unknown vectors related to Lawful Intercept. |
| CVE-2014-6462 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.2.1 and 11.1.2.2 allows remote attackers to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-6461 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Agile PLM component in Oracle Supply Chain Products Suite 9.3.1.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Roles & Privileges. |
| CVE-2014-6460 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52, 8.53, and 8.54 allows remote authenticated users to affect confidentiality and integrity via vectors related to QUERY. |
| CVE-2014-4285 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Technology component in Oracle E-Business Suite 11.5.10.2 allows remote attackers to affect integrity via unknown vectors related to Reports Configuration. |
| CVE-2014-4281 | Medium | 2014-10-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Framework component in Oracle E-Business Suite 12.1.3, 12.2.2, 12.2.3, and 12.2.4 allows remote attackers to affect integrity via unknown vectors related to Portal Integration. |
| CVE-2014-0119 | Medium | 2014-05-31 | Protected by Waratek | No public exploit | Apache Tomcat before 6.0.40, 7.x before 7.0.54, and 8.x before 8.0.6 does not properly constrain the class loader that accesses the XML parser used with an XSLT stylesheet, which allows remote attackers to (1) read arbitrary files via a crafted web application that provides an XML external entity declaration in conjunction with an entity reference, related to an XML External Entity (XXE) issue, or (2) read files associated with different web applications on a single Tomcat instance via a crafted web application. |
| CVE-2014-2880 | Medium | 2014-04-17 | Protected by Waratek | Working exploit published | Open redirect vulnerability in the Oracle Identity Manager component in Oracle Fusion Middleware 11.1.1.5, 11.1.1.7, 11.1.2.1, and 11.1.2.2 allows remote attackers to redirect users to arbitrary web sites and conduct phishing attacks via a URL in the backUrl parameter in a changepwd action to identity/faces/firstlogin. |