
Oracle Critical Patch Update July 2014
Released July 2014 · Oracle's advisory ↗ · ← Critical Patch Update, April 2014 · Critical Patch Update, October 2014 →
103 CVEs in this release, one square each
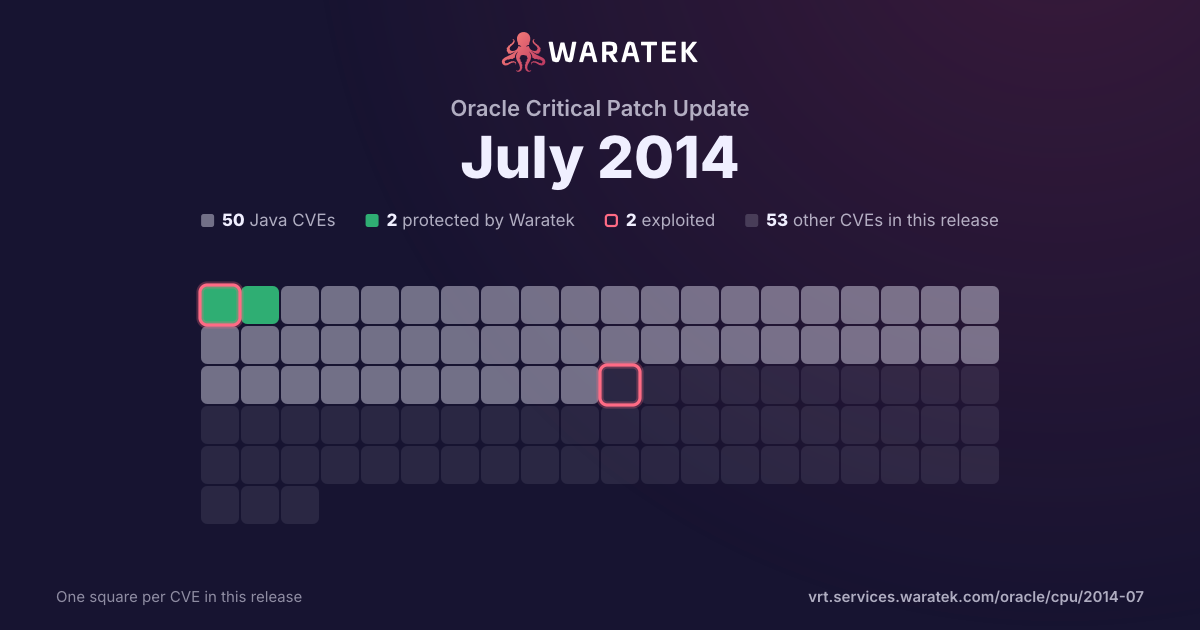
By status
2Protected by Waratek1Mitigation candidate47No exploit published27Outside Waratek scope26Not applicable
2Exploited, marked by the ring
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 18 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
18matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
18
100.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
18
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
18
100.0%
split by
peak 16 / month
Feb 131
Not applicable1
Medium1
not blocked1
No public exploit1
Mar 130
Apr 130
May 130
Jun 130
Jul 130
Aug 130
Sep 130
Oct 130
Nov 130
Dec 130
Jan 140
Feb 140
Mar 141
Not applicable1
Medium1
not blocked1
No public exploit1
Apr 140
May 140
Jun 140
Jul 1416
Not applicable16
Medium16
not blocked16
No public exploit16
Mar 13May 13Jul 13Sep 13Nov 13Jan 14Mar 14May 14Jul 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-4261 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.14 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-2487. |
| CVE-2014-4260 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier, and 5.6.17 and earlier, allows remote authenticated users to affect integrity and availability via vectors related to SRCHAR. |
| CVE-2014-4258 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier and 5.6.17 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to SRINFOSC. |
| CVE-2014-4239 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8, 9, 10, and 11.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Common Agent Container (Cacao). |
| CVE-2014-4238 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect availability via vectors related to SROPTZR. |
| CVE-2014-4233 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect availability via vectors related to SRREP. |
| CVE-2014-4232 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop (SGD) component in Oracle Virtualization 4.63, 4.71, 5.0, and 5.1 allows remote attackers to affect integrity via unknown vectors related to Workspace Web Application, a different vulnerability than CVE-2014-2463. |
| CVE-2014-4228 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 4.1.34, 4.2.26, and 4.3.12 allows local users to affect confidentiality, integrity, and availability via vectors related to Graphics driver (WDDM) for Windows guests. |
| CVE-2014-4225 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Patch installation scripts. |
| CVE-2014-4224 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8, 9, 10, and 11.1 allows local users to affect availability via unknown vectors related to sockfs. |
| CVE-2014-4215 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via vectors related to CPU performance counters (CPC) drivers, a different vulnerability than CVE-2013-5862. |
| CVE-2014-4207 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier allows remote authenticated users to affect availability via vectors related to SROPTZR. |
| CVE-2014-2494 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier allows remote authenticated users to affect availability via vectors related to ENARC. |
| CVE-2014-2489 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.12 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core. |
| CVE-2014-2487 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.14, when running on Windows, allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-4261. |
| CVE-2014-2484 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to SRFTS. |
| CVE-2014-0098 | Medium | 2014-03-18 | Not applicable | No public exploit | The log_cookie function in mod_log_config.c in the mod_log_config module in the Apache HTTP Server before 2.4.8 allows remote attackers to cause a denial of service (segmentation fault and daemon crash) via a crafted cookie that is not properly handled during truncation. |
| CVE-2013-1620 | Medium | 2013-02-08 | Not applicable | No public exploit | The TLS implementation in Mozilla Network Security Services (NSS) does not properly consider timing side-channel attacks on a noncompliant MAC check operation during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, a related issue to CVE-2013-0169. |