
Oracle Critical Patch Update April 2014
Released April 2014 · Oracle's advisory ↗ · ← Critical Patch Update, January 2014 · Critical Patch Update, July 2014 →
104 CVEs in this release, one square each
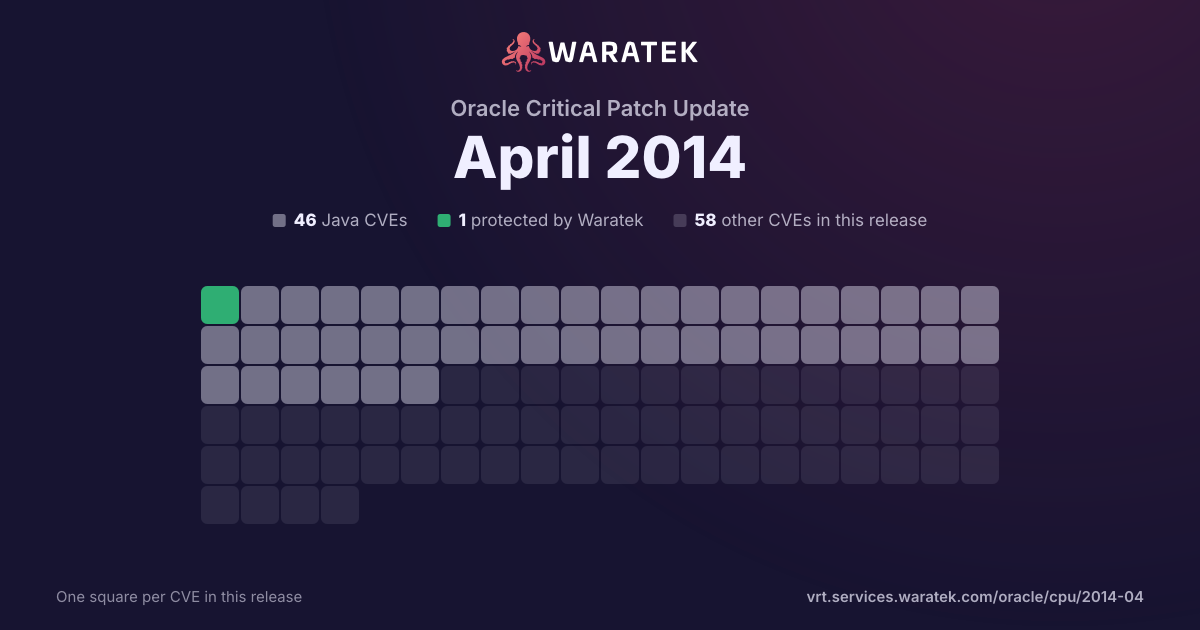
By status
1Protected by Waratek2Mitigation candidate43No exploit published33Outside Waratek scope25Not applicable
No exploit published. For 41 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 46 matches · 1 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 0 EPSS ≥ 0.5
Protected by Waratek
1
2.2%
Rule in development
0
0.0%
Mitigation candidate
2
4.3%
No exploit published
43
93.5%
blocked by ARMR today
1
2.2%
partly blocked
0
0.0%
not blocked
45
97.8%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
4.3%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
44
95.7%
split by
peak 45 / month
Feb 14Mar 14Apr 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-2471 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iLearning component in Oracle iLearning 6.0 and 6.1 allows remote attackers to affect integrity via unknown vectors related to Learner Pages. |
| CVE-2014-2470 | High | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Security. |
| CVE-2014-2468 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote attackers to affect integrity via vectors related to Open_UI, a different vulnerability than CVE-2014-4230. |
| CVE-2014-2467 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2014-2445. |
| CVE-2014-2466 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-2465 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3 allows remote attackers to affect integrity via unknown vectors related to Security. |
| CVE-2014-2464 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-2461 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 5.5.06, 6.0, 6.1, 6.2, 6.3, 6.3.1, 6.3.2, and 6.3.3 allows remote attackers to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-2460 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 5.5.06, 6.0, 6.1, 6.2, 6.3, 6.3.1, 6.3.2, and 6.3.3 allows remote authenticated users to affect confidentiality via vectors related to CSV Management. |
| CVE-2014-2459 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.3.2 and 6.3.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Security. |
| CVE-2014-2458 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Lifecycle component in Oracle Supply Chain Products Suite 6.1.0.3 and 6.1.1.3 allows remote attackers to affect integrity via unknown vectors related to Install. |
| CVE-2014-2457 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Lifecycle component in Oracle Supply Chain Products Suite 6.0 and 6.1.0 allows remote attackers to affect integrity via unknown vectors related to Install. |
| CVE-2014-2455 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Admin component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to User Interface. |
| CVE-2014-2454 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Admin component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote attackers to affect confidentiality via unknown vectors related to User Interface. |
| CVE-2014-2453 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Admin component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote attackers to affect integrity via unknown vectors related to User Interface. |
| CVE-2014-2452 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5 allows remote authenticated users to affect availability via unknown vectors related to Webserver Plugin. |
| CVE-2014-2449 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HRMS Talent Acquisition Manager component in Oracle PeopleSoft Products 9.0, 9.1, and 9.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-2448 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect confidentiality via unknown vectors related to Install and Packaging. |
| CVE-2014-2447 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect confidentiality via unknown vectors related to Integration Broker, a different vulnerability than CVE-2014-2437. |
| CVE-2014-2446 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote authenticated users to affect confidentiality via vectors related to QAS. |
| CVE-2014-2445 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile PLM Framework component in Oracle Supply Chain Products Suite 9.3.3 allows remote authenticated users to affect integrity via unknown vectors related to Security, a different vulnerability than CVE-2014-2467. |
| CVE-2014-2443 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect integrity via vectors related to PIA Core Technology. |
| CVE-2014-2437 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect confidentiality via unknown vectors related to Integration Broker, a different vulnerability than CVE-2014-2447. |
| CVE-2014-2433 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote attackers to affect availability via unknown vectors related to Integration Broker. |
| CVE-2014-2429 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise CS Campus Self Service component in Oracle PeopleSoft Products 9.0 allows remote authenticated users to affect confidentiality via unknown vectors related to Campus Mobile. |
| CVE-2014-2426 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle OpenSSO component in Oracle Fusion Middleware 8.0 Update 2 Patch 5 allows remote authenticated users to affect integrity and availability via unknown vectors related to Admin Console. |
| CVE-2014-2425 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle OpenSSO component in Oracle Fusion Middleware 8.0 Update 2 Patch 5 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-2424 | Medium | 2014-04-16 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Event Processing component in Oracle Fusion Middleware 11.1.1.7.0 allows remote authenticated users to affect integrity via vectors related to CEP system. |
| CVE-2014-2418 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality, a different vulnerability than CVE-2014-2407, CVE-2014-2415, CVE-2014-2416, and CVE-2014-2417. |
| CVE-2014-2417 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality, a different vulnerability than CVE-2014-2407, CVE-2014-2415, CVE-2014-2416, and CVE-2014-2418. |
| CVE-2014-2416 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality, a different vulnerability than CVE-2014-2407, CVE-2014-2415, CVE-2014-2417, and CVE-2014-2418. |
| CVE-2014-2415 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality, a different vulnerability than CVE-2014-2407, CVE-2014-2416, CVE-2014-2417, and CVE-2014-2418. |
| CVE-2014-2411 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Analytics component in Oracle Fusion Middleware Oracle Identity Analytics 11.1.1.5 and Sun Role Manager 5.0 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Security. |
| CVE-2014-2407 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Data Integrator component in Oracle Fusion Middleware 11.1.1.3.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Data Quality, a different vulnerability than CVE-2014-2415, CVE-2014-2416, CVE-2014-2417, and CVE-2014-2418. |
| CVE-2014-2404 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 10.1.4.3, 11.1.1.3.0, 11.1.1.5.0, 11.1.1.7.0, 11.1.2.0.0, 11.1.2.1.0, and 11.1.2.2.0 allows remote authenticated users to affect confidentiality via unknown vectors related to WebGate. |
| CVE-2014-2400 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Endeca Server component in Oracle Fusion Middleware 2.2.2 allows remote attackers to affect integrity via unknown vectors related to Oracle Endeca Information Discovery (Formerly Latitude), a different vulnerability than CVE-2014-2399. |
| CVE-2014-2399 | Medium | 2014-04-16 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Endeca Server component in Oracle Fusion Middleware 2.2.2 allows remote attackers to affect integrity via unknown vectors related to Oracle Endeca Information Discovery (Formerly Latitude), a different vulnerability than CVE-2014-2400. |
| CVE-2014-2398 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u61, 6u71, 7u51, and 8; JavaFX 2.2.51; and JRockit R27.8.1 and R28.3.1 allows remote authenticated users to affect integrity via unknown vectors related to Javadoc. |
| CVE-2014-0465 | Low | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle OpenSSO component in Oracle Fusion Middleware 8.0 Update 2 Patch 5 allows remote authenticated users to affect integrity via unknown vectors related to Admin Console. |
| CVE-2014-0460 | Medium | 2014-04-16 | Protected by Waratek | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u61, 6u71, 7u51, and 8; JRockit R27.8.1 and R28.3.1; and Java SE Embedded 7u51 allows remote attackers to affect confidentiality and integrity via vectors related to JNDI. |
| CVE-2014-0450 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7 and 11.1.1.8 allows remote attackers to affect confidentiality via unknown vectors related to People Connection. |
| CVE-2014-0429 | High | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u61, 6u71, 7u51, and 8; JRockit R27.8.1 and R28.3.1; and Java SE Embedded 7u51 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2014-0426 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Containers for J2EE component in Oracle Fusion Middleware 10.1.3.5 allows remote attackers to affect integrity via vectors related to HTTP Request Handling, a different vulnerability than CVE-2014-0413. |
| CVE-2014-0414 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Containers for J2EE component in Oracle Fusion Middleware 10.1.3.5 allows remote attackers to affect confidentiality via vectors related to HTTP Request Handling. |
| CVE-2014-0413 | Medium | 2014-04-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Containers for J2EE component in Oracle Fusion Middleware 10.1.3.5 allows remote attackers to affect integrity via vectors related to HTTP Request Handling, a different vulnerability than CVE-2014-0426. |
| CVE-2014-1876 | Medium | 2014-02-10 | No exploit published | No public exploit | The unpacker::redirect_stdio function in unpack.cpp in unpack200 in OpenJDK 6, 7, and 8; Oracle Java SE 5.0u61, 6u71, 7u51, and 8; JRockit R27.8.1 and R28.3.1; and Java SE Embedded 7u51 does not securely create temporary files when a log file cannot be opened, which allows local users to overwrite arbitrary files via a symlink attack on /tmp/unpack.log. |