
Oracle Critical Patch Update July 2014
Released July 2014 · Oracle's advisory ↗ · ← Critical Patch Update, April 2014 · Critical Patch Update, October 2014 →
103 CVEs in this release, one square each
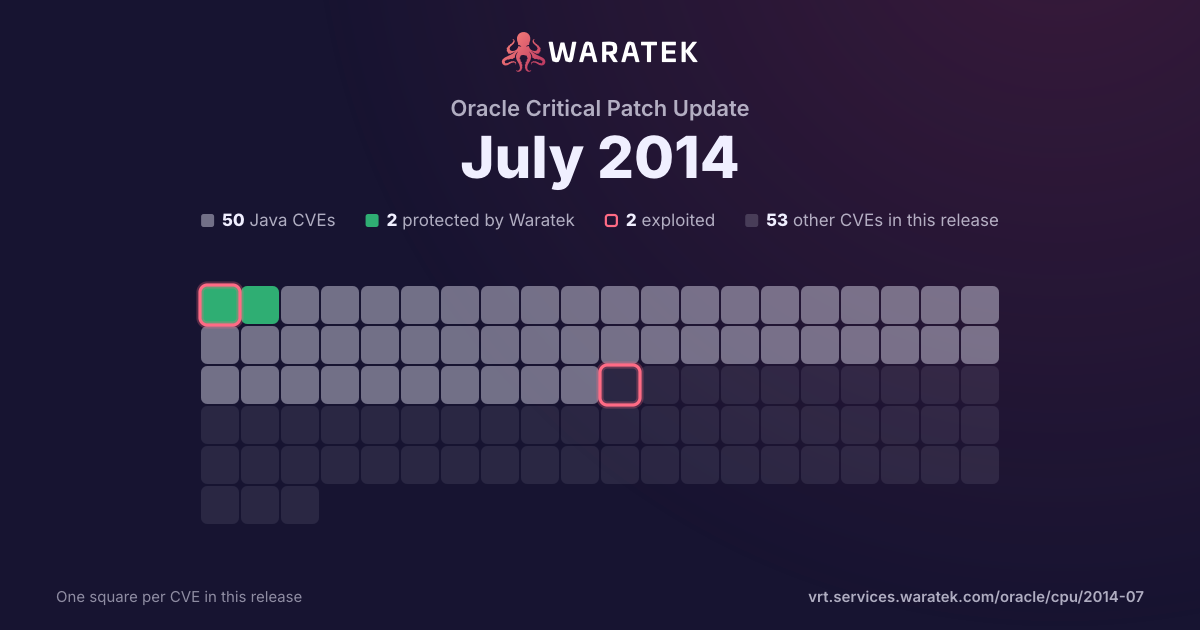
By status
2Protected by Waratek1Mitigation candidate47No exploit published27Outside Waratek scope26Not applicable
2Exploited, marked by the ring
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 11 matches · 0 in Waratek scope · 0 protected · 1 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
11matches
0in Waratek scope0.0%
0protected0.0%
1exploited9.1%
0CISA KEV0.0%
1public PoC9.1%
1EPSS ≥ 0.59.1%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
11
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
11
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
9.1%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
10
90.9%
split by
peak 8 / month
Jul 13Sep 13Nov 13Jan 14Mar 14May 14Jul 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-4262 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-4247 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to JavaFX. |
| CVE-2014-4227 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2014-4223 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-2483. |
| CVE-2014-4219 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-4216 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-2490 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE 7u60 and SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-2483 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE Java SE 7u60 and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-4223. NOTE: the previous information is from the July 2014 CPU. Oracle has not commented on another vendor's claim that the issue is related to improper restriction of the "use of privileged annotations." |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2013-3774 | High | 2013-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Network Layer component in Oracle Database Server 10.2.0.4, 10.2.0.5, 11.1.0.7, 11.2.0.2, 11.2.0.3, and 12.1.0.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2013-3751 | High | 2013-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the XML Parser component in Oracle Database Server 11.2.0.2, 11.2.0.3, and 12.1.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |