
Oracle Critical Patch Update July 2014
Released July 2014 · Oracle's advisory ↗ · ← Critical Patch Update, April 2014 · Critical Patch Update, October 2014 →
103 CVEs in this release, one square each
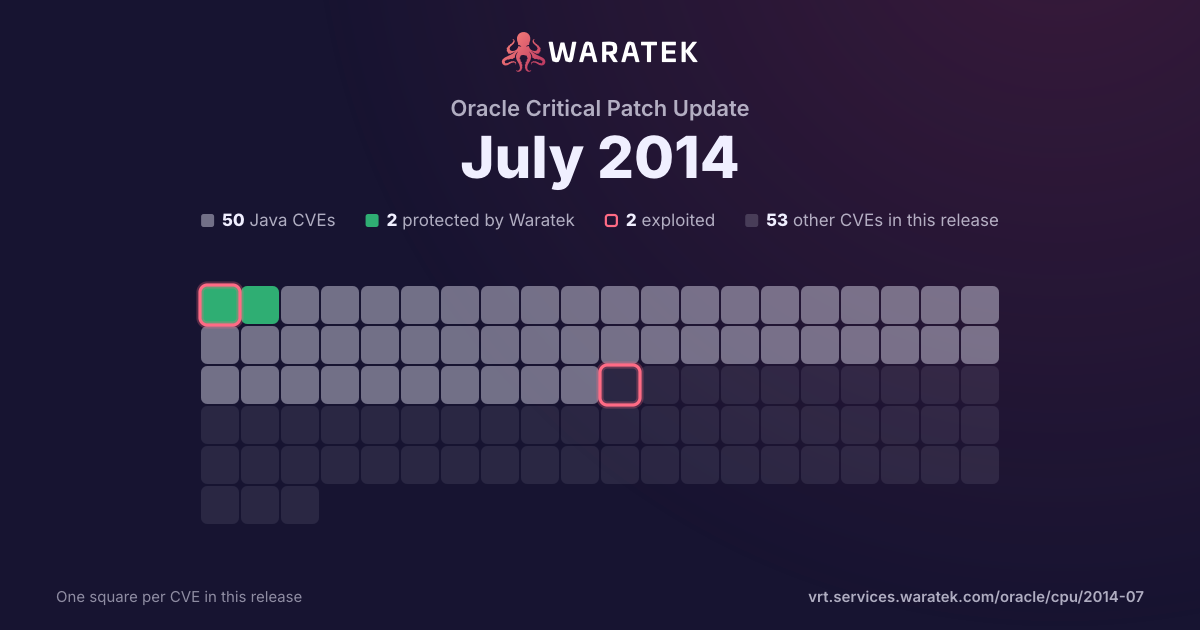
By status
2Protected by Waratek1Mitigation candidate47No exploit published27Outside Waratek scope26Not applicable
2Exploited, marked by the ring
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 1 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
1in Waratek scope11.1%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
1
11.1%
Outside Waratek scope
8
88.9%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 9 / month
Jul 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-4262 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-4257 | High | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.8.0 allows remote attackers to affect confidentiality via unknown vectors related to Portlet Services. |
| CVE-2014-4247 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to JavaFX. |
| CVE-2014-4227 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2014-4223 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-2483. |
| CVE-2014-4219 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-4216 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-2490 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE 7u60 and SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-2483 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE Java SE 7u60 and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-4223. NOTE: the previous information is from the July 2014 CPU. Oracle has not commented on another vendor's claim that the issue is related to improper restriction of the "use of privileged annotations." |