
Oracle Critical Patch Update July 2014
Released July 2014 · Oracle's advisory ↗ · ← Critical Patch Update, April 2014 · Critical Patch Update, October 2014 →
103 CVEs in this release, one square each
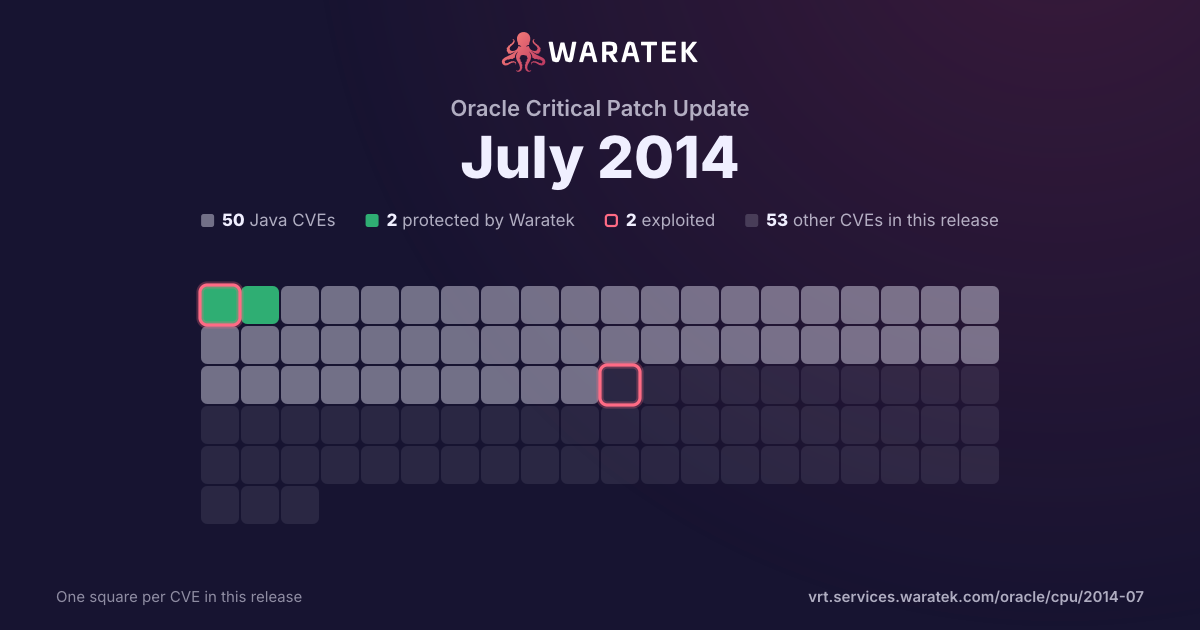
By status
2Protected by Waratek1Mitigation candidate47No exploit published27Outside Waratek scope26Not applicable
2Exploited, marked by the ring
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 96 matches · 50 in Waratek scope · 2 protected · 2 exploited · 0 CISA KEV · 4 public PoC · 2 EPSS ≥ 0.5
96matches
50in Waratek scope52.1%
2protected2.1%
2exploited2.1%
0CISA KEV0.0%
4public PoC4.2%
2EPSS ≥ 0.52.1%
Protected by Waratek
2
2.1%
Rule in development
0
0.0%
Mitigation candidate
1
1.0%
No exploit published
47
49.0%
Outside Waratek scope
22
22.9%
Not applicable
24
25.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
2
2.1%
partly blocked
0
0.0%
not blocked
94
97.9%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
2.1%
Working exploit published
2
2.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
92
95.8%
split by
peak 92 / month
Mar 141
Not applicable1
Medium1
not blocked1
No public exploit1
Apr 141
Protected by Waratek1
High1
blocked by ARMR today1
Exploited1
May 141
Not applicable1
High1
not blocked1
No public exploit1
Jun 141
Outside Waratek scope1
High1
not blocked1
Exploited1
Jul 1492
Protected by Waratek1
Mitigation candidate1
No exploit published47
Outside Waratek scope21
Not applicable22
High9
Medium65
Low18
blocked by ARMR today1
not blocked91
Working exploit published2
No public exploit90
Mar 14Apr 14May 14Jun 14Jul 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-4271 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Essbase component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote attackers to affect availability via unknown vectors related to Agent. |
| CVE-2014-4270 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Admin component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect confidentiality via unknown vectors related to User Interface, a different vulnerability than CVE-2014-4269. |
| CVE-2014-4269 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Common Admin component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect confidentiality via unknown vectors related to User Interface, a different vulnerability than CVE-2014-4270. |
| CVE-2014-4268 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality via unknown vectors related to Swing. |
| CVE-2014-4267 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components. |
| CVE-2014-4266 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 and 8u5 allows remote attackers to affect integrity via unknown vectors related to Serviceability. |
| CVE-2014-4265 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect integrity via unknown vectors related to Deployment. |
| CVE-2014-4264 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 and 8u5 allows remote attackers to affect availability via unknown vectors related to Security. |
| CVE-2014-4263 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5, and JRockit R27.8.2 and R28.3.2, allows remote attackers to affect confidentiality and integrity via unknown vectors related to "Diffie-Hellman key agreement." |
| CVE-2014-4262 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. |
| CVE-2014-4261 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.14 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-2487. |
| CVE-2014-4260 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier, and 5.6.17 and earlier, allows remote authenticated users to affect integrity and availability via vectors related to SRCHAR. |
| CVE-2014-4258 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier and 5.6.17 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to SRINFOSC. |
| CVE-2014-4257 | High | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.8.0 allows remote attackers to affect confidentiality via unknown vectors related to Portlet Services. |
| CVE-2014-4256 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality and integrity via vectors related to WLS - Deployment. |
| CVE-2014-4255 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Security and Policy. |
| CVE-2014-4254 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Web Services. |
| CVE-2014-4253 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WebLogic Server JVM. |
| CVE-2014-4252 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality via unknown vectors related to Security. |
| CVE-2014-4251 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0 and 12.1.2.0 allows remote authenticated users to affect integrity via vectors related to plugin 1.1. |
| CVE-2014-4250 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - Server OM Frwks component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Object Manager. |
| CVE-2014-4249 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Mobile Service. |
| CVE-2014-4248 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, and 12.2.3 allows local users to affect confidentiality via unknown vectors related to Logging. |
| CVE-2014-4247 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to JavaFX. |
| CVE-2014-4246 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Analytic Provider Services component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote authenticated users to affect confidentiality via vectors related to SVP. |
| CVE-2014-4245 | Low | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Core component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-4244 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5, and JRockit R27.8.2 and JRockit R28.3.2, allows remote attackers to affect confidentiality and integrity via unknown vectors related to Security. |
| CVE-2014-4243 | Low | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.35 and earlier and 5.6.15 and earlier allows remote authenticated users to affect availability via vectors related to ENFED. |
| CVE-2014-4242 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect integrity via unknown vectors related to Console. |
| CVE-2014-4241 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0 and 10.3.6.0 allows remote attackers to affect integrity via vectors related to WLS - Web Services. |
| CVE-2014-4240 | Low | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows local users to affect confidentiality and integrity via vectors related to SRREP. |
| CVE-2014-4239 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8, 9, 10, and 11.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Common Agent Container (Cacao). |
| CVE-2014-4238 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect availability via vectors related to SROPTZR. |
| CVE-2014-4237 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Core component in Oracle Database Server 11.2.0.4 and 12.1.0.1 allows remote authenticated users to affect confidentiality via unknown vectors. |
| CVE-2014-4236 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the RDBMS Core component in Oracle Database Server 11.2.0.4 and 12.1.0.1 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-4235 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iStore component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, 12.2.2, and 12.2.3 allows remote authenticated users to affect integrity via unknown vectors. |
| CVE-2014-4234 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.1, 6.2, 6.3, 6.3.1, 6.3.2, 6.3.3, and 6.3.4 allows remote attackers to affect confidentiality via unknown vectors related to Data, Domain & Function Security. |
| CVE-2014-4233 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect availability via vectors related to SRREP. |
| CVE-2014-4232 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop (SGD) component in Oracle Virtualization 4.63, 4.71, 5.0, and 5.1 allows remote attackers to affect integrity via unknown vectors related to Workspace Web Application, a different vulnerability than CVE-2014-2463. |
| CVE-2014-4231 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Travel & Transportation component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote attackers to affect integrity via unknown vectors related to Diary. |
| CVE-2014-4230 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote attackers to affect integrity via vectors related to Open_UI, a different vulnerability than CVE-2014-2468. |
| CVE-2014-4229 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Transportation Management component in Oracle Supply Chain Products Suite 6.2, 6.3, 6.3.1, 6.3.2, 6.3.3, and 6.3.4 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Data, Domain, and Function Security. |
| CVE-2014-4228 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 4.1.34, 4.2.26, and 4.3.12 allows local users to affect confidentiality, integrity, and availability via vectors related to Graphics driver (WDDM) for Windows guests. |
| CVE-2014-4227 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2014-4226 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise FIN Install component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-4225 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 10 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Patch installation scripts. |
| CVE-2014-4224 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Sun Solaris 8, 9, 10, and 11.1 allows local users to affect availability via unknown vectors related to sockfs. |
| CVE-2014-4223 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-2483. |
| CVE-2014-4222 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0 and 12.1.2.0 allows remote authenticated users to affect confidentiality via vectors related to plugin 1.1. |
| CVE-2014-4221 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 and 8u5 allows remote attackers to affect confidentiality via unknown vectors related to Libraries. |
| CVE-2014-4220 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u60 and 8u5 allows remote attackers to affect integrity via unknown vectors related to Deployment, a different vulnerability than CVE-2014-4208. |
| CVE-2014-4219 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-4218 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect integrity via unknown vectors related to Libraries. |
| CVE-2014-4217 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, and 12.1.1.0 allows remote attackers to affect integrity via vectors related to WLS - Web Services. |
| CVE-2014-4216 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-4215 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via vectors related to CPU performance counters (CPC) drivers, a different vulnerability than CVE-2013-5862. |
| CVE-2014-4214 | Low | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect availability via vectors related to SRSP. |
| CVE-2014-4213 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Applications Manager component in Oracle E-Business Suite 12.0.6, 12.1.3, 12.2.2, and 12.2.3 allows remote attackers to affect integrity via unknown vectors. |
| CVE-2014-4212 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Fusion Middleware component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Process Mgmt and Notification. |
| CVE-2014-4211 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7 and 11.1.1.8 allows remote attackers to affect integrity via unknown vectors related to Portlet Services. |
| CVE-2014-4210 | Medium | 2014-07-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0 and 10.3.6.0 allows remote attackers to affect confidentiality via vectors related to WLS - Web Services. |
| CVE-2014-4209 | Medium | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u65, 6u75, 7u60, and 8u5 allows remote attackers to affect confidentiality and integrity via vectors related to JMX. |
| CVE-2014-4208 | Low | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE 7u60 and 8u5 allows remote attackers to affect integrity via unknown vectors related to Deployment, a different vulnerability than CVE-2014-4220. |
| CVE-2014-4207 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier allows remote authenticated users to affect availability via vectors related to SROPTZR. |
| CVE-2014-4206 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows local users to affect integrity and availability via unknown vectors related to Data Synchronizer. |
| CVE-2014-4205 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote attackers to affect integrity via unknown vectors related to Portal Framework, a different vulnerability than CVE-2014-2491. |
| CVE-2014-4204 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.53 allows remote authenticated users to affect integrity via vectors related to PIA Core Technology. |
| CVE-2014-4203 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Enterprise Performance Management Architect component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Property Editing. |
| CVE-2014-4202 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WLS - Web Services. |
| CVE-2014-4201 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WLS - Web Services. |
| CVE-2014-2496 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PT PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Test Framework. |
| CVE-2014-2495 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise SCM Purchasing component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality via unknown vectors related to Purchasing. |
| CVE-2014-2494 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.37 and earlier allows remote authenticated users to affect availability via vectors related to ENARC. |
| CVE-2014-2493 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.2.4.0, and 12.1.2.0.0 allows remote attackers to affect confidentiality and availability via vectors related to ADF Faces. |
| CVE-2014-2492 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Agile Product Collaboration component in Oracle Supply Chain Products Suite 9.3.3 allows remote attackers to affect integrity via unknown vectors related to Web client (PC). |
| CVE-2014-2491 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel UI Framework component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote attackers to affect integrity via unknown vectors related to Portal Framework, a different vulnerability than CVE-2014-4205. |
| CVE-2014-2490 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE 7u60 and SE 8u5 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-2489 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.12 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core. |
| CVE-2014-2488 | Low | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.12 allows local users to affect confidentiality via unknown vectors related to Core. |
| CVE-2014-2487 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.14, when running on Windows, allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-4261. |
| CVE-2014-2486 | Low | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.12 allows local users to affect integrity and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-2477. |
| CVE-2014-2485 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Core - EAI component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows local users to affect confidentiality via unknown vectors related to Integration Business Services. |
| CVE-2014-2484 | Medium | 2014-07-17 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.17 and earlier allows remote authenticated users to affect confidentiality, integrity, and availability via vectors related to SRFTS. |
| CVE-2014-2483 | High | 2014-07-17 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE Java SE 7u60 and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries, a different vulnerability than CVE-2014-4223. NOTE: the previous information is from the July 2014 CPU. Oracle has not commented on another vendor's claim that the issue is related to improper restriction of the "use of privileged annotations." |
| CVE-2014-2482 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Concurrent Processing component in Oracle E-Business Suite 12.1.3, 12.2.2, and 12.2.3 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2014-2481 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2014-2480. |
| CVE-2014-2480 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2014-2481. |
| CVE-2014-2479 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Web Services. |
| CVE-2014-2477 | Low | 2014-07-17 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox before 3.2.24, 4.0.26, 4.1.34, 4.2.26, and 4.3.12 allows local users to affect integrity and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-2486. |
| CVE-2014-2456 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise ELS Enterprise Learning Management component in Oracle PeopleSoft Products 9.1 and 9.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors. |
| CVE-2014-0436 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion BI+ component in Oracle Hyperion 11.1.2.2 and 11.1.2.3 allows remote attackers to affect integrity via unknown vectors related to Web Analysis. |
| CVE-2013-5855 | Medium | 2014-07-17 | Protected by Waratek | No public exploit | Oracle Mojarra 2.2.x before 2.2.6 and 2.1.x before 2.1.28 does not perform appropriate encoding when a (1) <h:outputText> tag or (2) EL expression is used after a scriptor style block, which allows remote attackers to conduct cross-site scripting (XSS) attacks via application-specific vectors. |
| CVE-2014-0224 | High | 2014-06-05 | Outside Waratek scope | Exploited | OpenSSL before 0.9.8za, 1.0.0 before 1.0.0m, and 1.0.1 before 1.0.1h does not properly restrict processing of ChangeCipherSpec messages, which allows man-in-the-middle attackers to trigger use of a zero-length master key in certain OpenSSL-to-OpenSSL communications, and consequently hijack sessions or obtain sensitive information, via a crafted TLS handshake, aka the "CCS Injection" vulnerability. |
| CVE-2014-0211 | High | 2014-05-15 | Not applicable | No public exploit | Multiple integer overflows in the (1) fs_get_reply, (2) fs_alloc_glyphs, and (3) fs_read_extent_info functions in X.Org libXfont before 1.4.8 and 1.4.9x before 1.4.99.901 allow remote font servers to execute arbitrary code via a crafted xfs reply, which triggers a buffer overflow. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2014-0098 | Medium | 2014-03-18 | Not applicable | No public exploit | The log_cookie function in mod_log_config.c in the mod_log_config module in the Apache HTTP Server before 2.4.8 allows remote attackers to cause a denial of service (segmentation fault and daemon crash) via a crafted cookie that is not properly handled during truncation. |