
Oracle Critical Patch Update July 2014
Released July 2014 · Oracle's advisory ↗ · ← Critical Patch Update, April 2014 · Critical Patch Update, October 2014 →
103 CVEs in this release, one square each
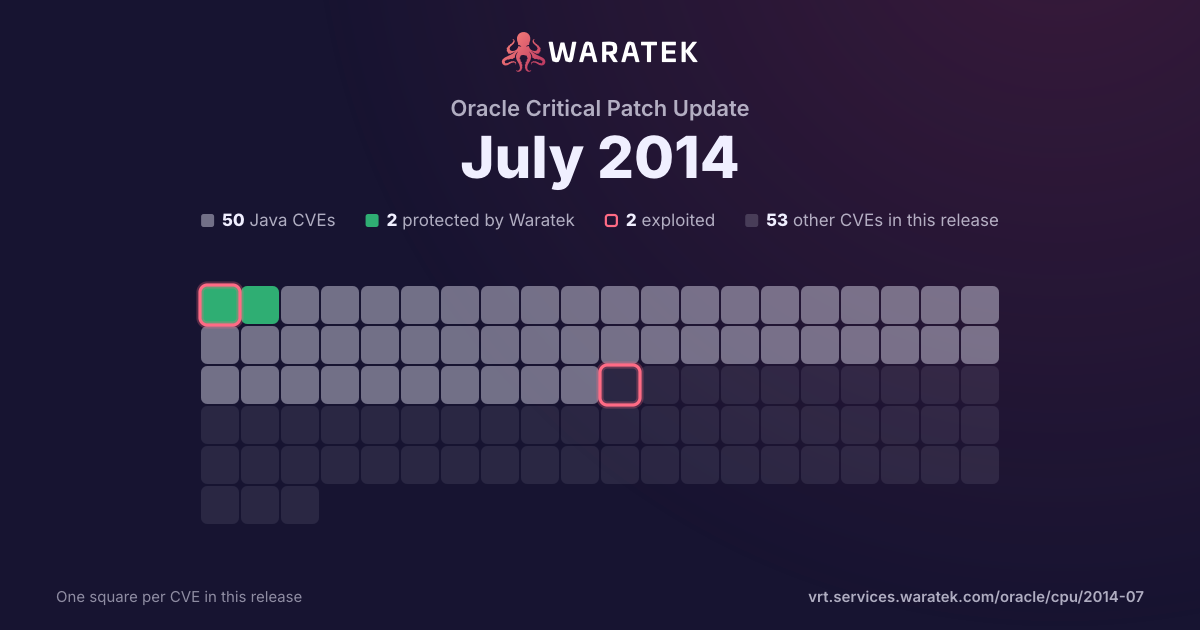
By status
2Protected by Waratek1Mitigation candidate51No exploit published22Outside Waratek scope27Not applicable
2Exploited, marked by the ring
No exploit published. For 46 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 24 matches · 2 protected · 1 exploited · 0 CISA KEV · 2 public PoC · 1 EPSS ≥ 0.5
Protected by Waratek
2
8.3%
Rule in development
0
0.0%
Mitigation candidate
1
4.2%
No exploit published
21
87.5%
blocked by ARMR today
2
8.3%
partly blocked
0
0.0%
not blocked
22
91.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
1
4.2%
Working exploit published
1
4.2%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
22
91.7%
split by
peak 22 / month
Feb 141
No exploit published1
Medium1
not blocked1
No public exploit1
Mar 140
Apr 141
Protected by Waratek1
High1
blocked by ARMR today1
Exploited1
May 140
Jun 140
Jul 1422
Protected by Waratek1
Mitigation candidate1
No exploit published20
High1
Medium19
Low2
blocked by ARMR today1
not blocked21
Working exploit published1
No public exploit21
Feb 14Mar 14Apr 14May 14Jun 14Jul 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-4267 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS Core Components. |
| CVE-2014-4257 | High | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7.0 and 11.1.1.8.0 allows remote attackers to affect confidentiality via unknown vectors related to Portlet Services. |
| CVE-2014-4256 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality and integrity via vectors related to WLS - Deployment. |
| CVE-2014-4255 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Security and Policy. |
| CVE-2014-4254 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Web Services. |
| CVE-2014-4253 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WebLogic Server JVM. |
| CVE-2014-4251 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0 and 12.1.2.0 allows remote authenticated users to affect integrity via vectors related to plugin 1.1. |
| CVE-2014-4249 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the BI Publisher component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Mobile Service. |
| CVE-2014-4242 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect integrity via unknown vectors related to Console. |
| CVE-2014-4241 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0 and 10.3.6.0 allows remote attackers to affect integrity via vectors related to WLS - Web Services. |
| CVE-2014-4222 | Low | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle HTTP Server component in Oracle Fusion Middleware 11.1.1.7.0 and 12.1.2.0 allows remote authenticated users to affect confidentiality via vectors related to plugin 1.1. |
| CVE-2014-4217 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, and 12.1.1.0 allows remote attackers to affect integrity via vectors related to WLS - Web Services. |
| CVE-2014-4212 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Fusion Middleware component in Oracle Fusion Middleware 11.1.1.7 allows remote attackers to affect confidentiality via unknown vectors related to Process Mgmt and Notification. |
| CVE-2014-4211 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.7 and 11.1.1.8 allows remote attackers to affect integrity via unknown vectors related to Portlet Services. |
| CVE-2014-4210 | Medium | 2014-07-17 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0 and 10.3.6.0 allows remote attackers to affect confidentiality via vectors related to WLS - Web Services. |
| CVE-2014-4202 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WLS - Web Services. |
| CVE-2014-4201 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect availability via vectors related to WLS - Web Services. |
| CVE-2014-2493 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.1.7.0, 11.1.2.4.0, and 12.1.2.0.0 allows remote attackers to affect confidentiality and availability via vectors related to ADF Faces. |
| CVE-2014-2481 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2014-2480. |
| CVE-2014-2480 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors, a different vulnerability than CVE-2014-2481. |
| CVE-2014-2479 | Medium | 2014-07-17 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebLogic Server component in Oracle Fusion Middleware 10.0.2.0, 10.3.6.0, 12.1.1.0, and 12.1.2.0 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to WLS - Web Services. |
| CVE-2013-5855 | Medium | 2014-07-17 | Protected by Waratek | No public exploit | Oracle Mojarra 2.2.x before 2.2.6 and 2.1.x before 2.1.28 does not perform appropriate encoding when a (1) <h:outputText> tag or (2) EL expression is used after a scriptor style block, which allows remote attackers to conduct cross-site scripting (XSS) attacks via application-specific vectors. |
| CVE-2014-0114 | High | 2014-04-30 | Protected by Waratek | Exploited | Apache Commons BeanUtils, as distributed in lib/commons-beanutils-1.8.0.jar in Apache Struts 1.x through 1.3.10 and in other products requiring commons-beanutils through 1.9.2, does not suppress the class property, which allows remote attackers to "manipulate" the ClassLoader and execute arbitrary code via the class parameter, as demonstrated by the passing of this parameter to the getClass method of the ActionForm object in Struts 1. |
| CVE-2013-4286 | Medium | 2014-02-26 | No exploit published | No public exploit | Apache Tomcat before 6.0.39, 7.x before 7.0.47, and 8.x before 8.0.0-RC3, when an HTTP connector or AJP connector is used, does not properly handle certain inconsistent HTTP request headers, which allows remote attackers to trigger incorrect identification of a request's length and conduct request-smuggling attacks via (1) multiple Content-Length headers or (2) a Content-Length header and a "Transfer-Encoding: chunked" header. NOTE: this vulnerability exists because of an incomplete fix for CVE-2005-2090. |