
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
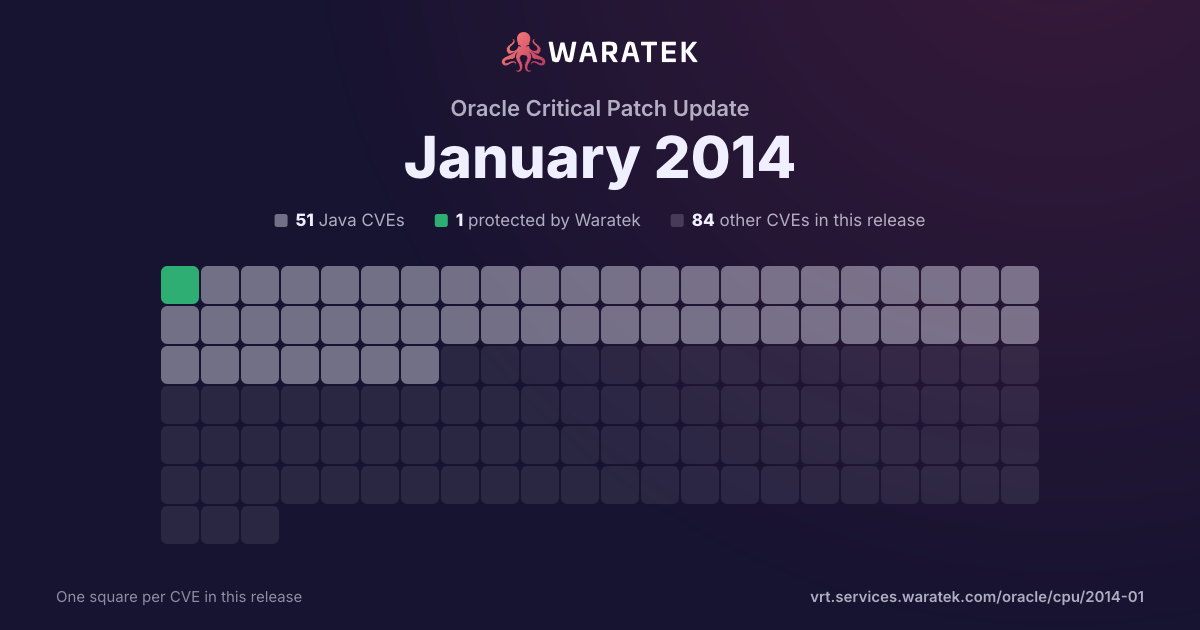
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 27 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
27matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
27
100.0%
Not applicable
0
0.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
27
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
27
100.0%
split by
peak 25 / month
Jun 13Jul 13Aug 13Sep 13Oct 13Nov 13Dec 13Jan 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0418 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5889, CVE-2013-5902, CVE-2014-0410, CVE-2014-0415, and CVE-2014-0424. |
| CVE-2014-0416 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect integrity via vectors related to JAAS. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to how principals are set for the Subject class, which allows attackers to escape the sandbox using deserialization of a crafted Subject instance. |
| CVE-2014-0411 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; JRockit R27.7.7 and R28.2.9; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect confidentiality and integrity via vectors related to JSSE. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that this issue allows remote attackers to obtain sensitive information about encryption keys via a timing discrepancy during the TLS/SSL handshake. |
| CVE-2014-0403 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5898 and CVE-2014-0375. |
| CVE-2014-0382 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 and JavaFX 2.2.45 allows remote attackers to affect availability via unknown vectors related to JavaFX. |
| CVE-2014-0378 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Spatial component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows local users to affect confidentiality, integrity, and availability via unknown vectors. |
| CVE-2014-0377 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect confidentiality via vectors related to SYS tables. |
| CVE-2014-0376 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect integrity via vectors related to JAXP. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to an improper check for "code permissions when creating document builder factories." |
| CVE-2014-0375 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5898 and CVE-2014-0403. |
| CVE-2014-0368 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45, and Java SE Embedded 7u45, allows remote attackers to affect confidentiality via unknown vectors related to Networking. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to incorrect permission checks when listening on a socket, which allows attackers to escape the sandbox. |
| CVE-2013-5910 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45, Java SE Embedded 7u45, and OpenJDK 7 allows remote attackers to affect integrity via unknown vectors related to Security. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that CanonicalizerBase.java in the XML canonicalizer allows untrusted code to access mutable byte arrays. |
| CVE-2013-5906 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Install, a different vulnerability than CVE-2013-5905. |
| CVE-2013-5905 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Install, a different vulnerability than CVE-2013-5906. |
| CVE-2013-5904 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2013-5902 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5889, CVE-2014-0410, CVE-2014-0415, CVE-2014-0418, and CVE-2014-0424. |
| CVE-2013-5899 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality via unknown vectors related to Deployment. |
| CVE-2013-5898 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality and integrity via unknown vectors related to Deployment, a different vulnerability than CVE-2014-0375 and CVE-2014-0403. |
| CVE-2013-5896 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect availability via vectors related to CORBA. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that com.sun.corba.se and its sub-packages are not included on the restricted package list. |
| CVE-2013-5895 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 and JavaFX 2.2.45 allows remote attackers to affect confidentiality via unknown vectors related to JavaFX. |
| CVE-2013-5888 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45, when running with GNOME, allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2013-5887 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect availability via unknown vectors related to Deployment. |
| CVE-2013-5884 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect confidentiality via vectors related to CORBA. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to an incorrect check for code permissions by CORBA stub factories. |
| CVE-2013-5870 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 and JavaFX 2.2.45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to JavaFX. |
| CVE-2013-5858 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2015-0370. |
| CVE-2013-5853 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2013-2067 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/authenticator/FormAuthenticator.java in the form authentication feature in Apache Tomcat 6.0.21 through 6.0.36 and 7.x before 7.0.33 does not properly handle the relationships between authentication requirements and sessions, which allows remote attackers to inject a request into a session by sending this request during completion of the login form, a variant of a session fixation attack. |
| CVE-2012-3544 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | Apache Tomcat 6.x before 6.0.37 and 7.x before 7.0.30 does not properly handle chunk extensions in chunked transfer coding, which allows remote attackers to cause a denial of service by streaming data. |