
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
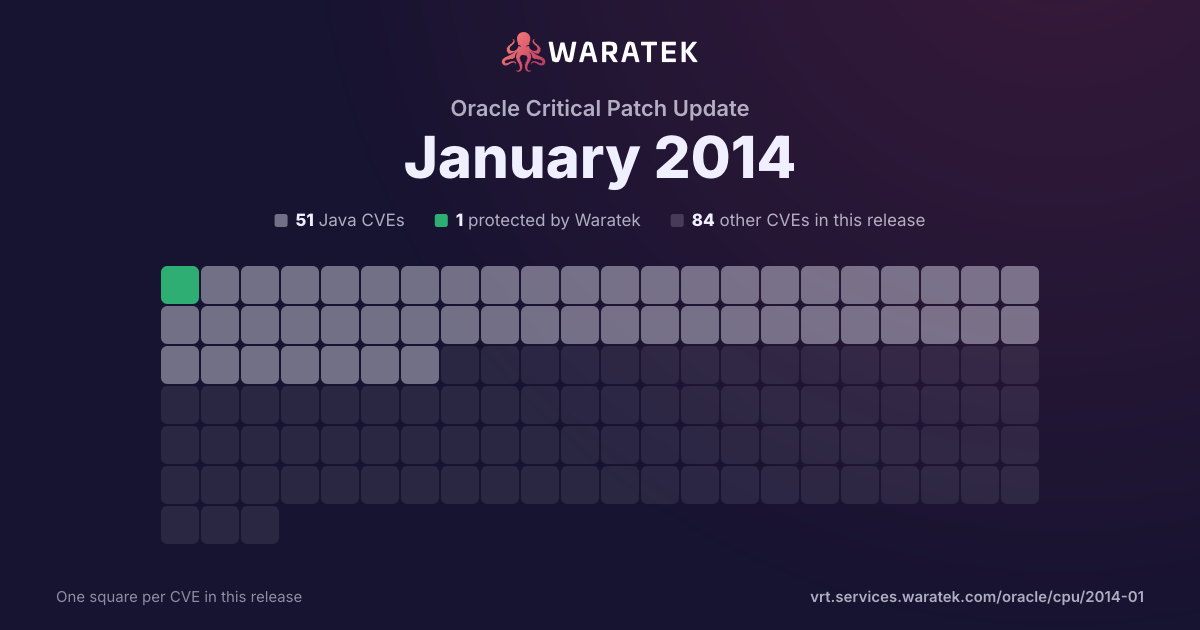
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 28 matches · 9 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 0 EPSS ≥ 0.5
28matches
9in Waratek scope32.1%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC3.6%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
9
32.1%
Outside Waratek scope
3
10.7%
Not applicable
16
57.1%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
28
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
3.6%
Forecast only
0
0.0%
No public exploit
27
96.4%
split by
peak 26 / year
20072008200920102011201220132014
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0444 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle AutoVue Electro-Mechanical Professional component in Oracle Supply Chain Products Suite 20.1.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Web General, a different vulnerability than CVE-2013-5868 and CVE-2013-5871. |
| CVE-2014-0437 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.72 and earlier, 5.5.34 and earlier, and 5.6.14 and earlier allows remote authenticated users to affect availability via unknown vectors related to Optimizer. |
| CVE-2014-0431 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.14 and earlier allows remote authenticated users to affect availability via unknown vectors related to InnoDB, a different vulnerability than CVE-2013-5881. |
| CVE-2014-0430 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.13 and earlier allows remote authenticated users to affect availability via unknown vectors related to Performance Schema. |
| CVE-2014-0427 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.13 and earlier allows remote authenticated users to affect availability via vectors related to FTS. |
| CVE-2014-0420 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.5.34 and earlier, and 5.6.14 and earlier, allows remote authenticated users to affect availability via unknown vectors related to Replication. |
| CVE-2014-0407 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.20, 4.0.22, 4.1.30, 4.2.20, and 4.3.4 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-0405. |
| CVE-2014-0406 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.20, 4.0.22, 4.1.30, 4.2.20, and 4.3.4 allows local users to affect integrity and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-0404. |
| CVE-2014-0405 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.20, 4.0.22, 4.1.30, 4.2.20, and 4.3.4 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-0407. |
| CVE-2014-0404 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.20, 4.0.22, 4.1.30, 4.2.20, and 4.3.4 allows local users to affect integrity and availability via unknown vectors related to Core, a different vulnerability than CVE-2014-0406. |
| CVE-2014-0393 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.71 and earlier, 5.5.33 and earlier, and 5.6.13 and earlier allows remote authenticated users to affect integrity via unknown vectors related to InnoDB. |
| CVE-2014-0383 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Identity Manager component in Oracle Fusion Middleware 11.1.2.0 and 11.1.2.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Identity Console. |
| CVE-2014-0381 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect integrity via vectors related to PIA Core Technology, a different vulnerability than CVE-2014-0445. |
| CVE-2014-0371 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Demantra Demand Management component in Oracle Supply Chain Products Suite 7.2.0.3 SQL-Server, 7.3.0.x, 7.3.1.x, 12.2.0, 12.2.1, and 12.2.2 allows remote authenticated users to affect integrity via unknown vectors related to DM Others. |
| CVE-2014-0370 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Life Sciences component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect availability via unknown vectors related to Clinical Trip Report. |
| CVE-2013-5908 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.1.72 and earlier, 5.5.34 and earlier, and 5.6.14 and earlier allows remote attackers to affect availability via unknown vectors related to Error Handling. |
| CVE-2013-5892 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.20, 4.0.22, 4.1.30, 4.2.22, and 4.3.6 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to Core. |
| CVE-2013-5885 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11.1 allows local users to affect integrity via unknown vectors related to Audit. |
| CVE-2013-5883 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8 allows local users to affect integrity and availability via unknown vectors related to Kernel. |
| CVE-2013-5875 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11.1 allows local users to affect integrity and availability via vectors related to Role Based Access Control (RBAC). |
| CVE-2013-5874 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, and 12.2.2 allows local users to affect confidentiality via unknown vectors related to Logging. |
| CVE-2013-5872 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via vectors related to Name Service Cache Daemon (NSCD). |
| CVE-2013-5871 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle AutoVue Electro-Mechanical Professional component in Oracle Supply Chain Products Suite 20.1.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Web General, a different vulnerability than CVE-2013-5868 and CVE-2014-0444. |
| CVE-2013-5868 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle AutoVue Electro-Mechanical Professional component in Oracle Supply Chain Products Suite 20.1.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Web General, a different vulnerability than CVE-2013-5871 and CVE-2014-0444. |
| CVE-2013-5808 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iPlanet Web Proxy Server component in Oracle Fusion Middleware 4.0 allows remote attackers to affect confidentiality via unknown vectors related to Administration. |
| CVE-2013-5764 | Low | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2013-2071 | Low | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/core/AsyncContextImpl.java in Apache Tomcat 7.x before 7.0.40 does not properly handle the throwing of a RuntimeException in an AsyncListener in an application, which allows context-dependent attackers to obtain sensitive request information intended for other applications in opportunistic circumstances via an application that records the requests that it processes. |
| CVE-2007-1858 | Low | 2007-05-10 | Outside Waratek scope | Proof of concept only | The default SSL cipher configuration in Apache Tomcat 4.1.28 through 4.1.31, 5.0.0 through 5.0.30, and 5.5.0 through 5.5.17 uses certain insecure ciphers, including the anonymous cipher, which allows remote attackers to obtain sensitive information or have other, unspecified impacts. |