
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
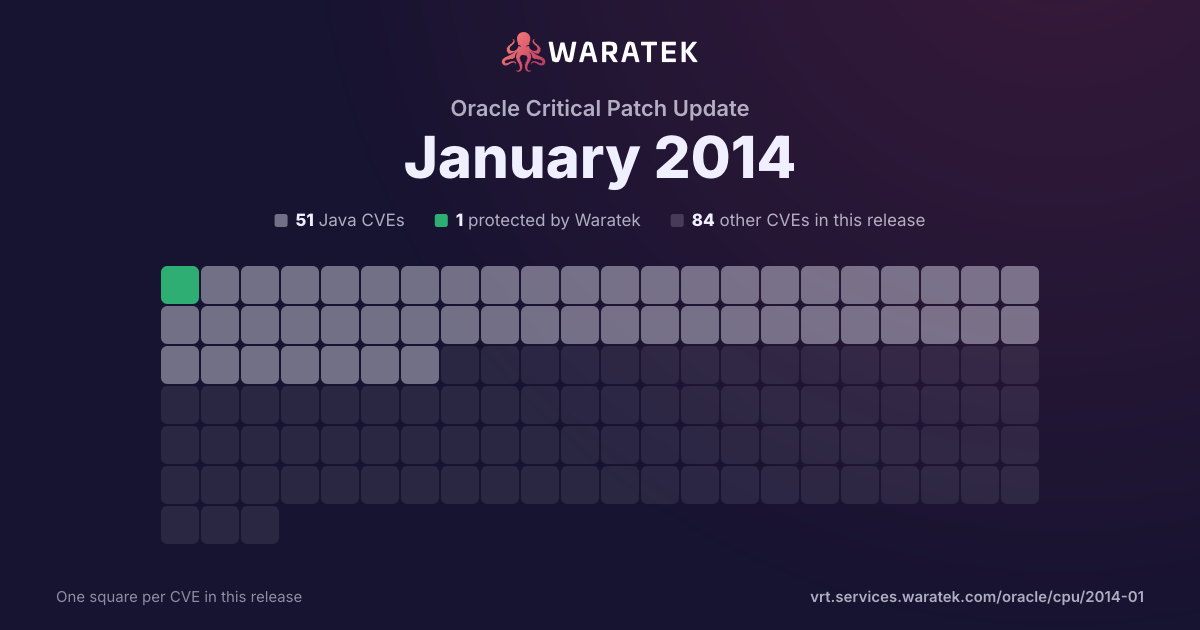
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 124 matches · 51 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 5 public PoC · 3 EPSS ≥ 0.5
124matches
51in Waratek scope41.1%
1protected0.8%
0exploited0.0%
0CISA KEV0.0%
5public PoC4.0%
3EPSS ≥ 0.52.4%
Protected by Waratek
1
0.8%
Rule in development
0
0.0%
Mitigation candidate
5
4.0%
No exploit published
45
36.3%
Outside Waratek scope
40
32.3%
Not applicable
33
26.6%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
0.8%
partly blocked
0
0.0%
not blocked
123
99.2%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
5
4.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
119
96.0%
split by
peak 122 / month
Sep 131
Outside Waratek scope1
High1
not blocked1
No public exploit1
Oct 131
Not applicable1
High1
not blocked1
No public exploit1
Nov 130
Dec 130
Jan 14122
Protected by Waratek1
Mitigation candidate5
No exploit published45
Outside Waratek scope39
Not applicable32
High16
Medium80
Low26
blocked by ARMR today1
not blocked121
Working exploit published5
No public exploit117
Sep 13Oct 13Nov 13Dec 13Jan 14
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-5878 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45, Java SE Embedded 7u45, and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the Security component does not properly handle null XML namespace (xmlns) attributes during XML document canonicalization, which allows attackers to escape the sandbox. |
| CVE-2013-5877 | Medium | 2014-01-15 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Demantra Demand Management component in Oracle Supply Chain Products Suite 7.2.0.3 SQL-Server, 7.3.0, 7.3.1, 12.2.0, and 12.2.1 allows remote attackers to affect confidentiality via unknown vectors related to DM Others. |
| CVE-2013-5876 | Medium | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via unknown vectors related to Kernel, a different vulnerability than CVE-2014-0447. |
| CVE-2013-5875 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11.1 allows local users to affect integrity and availability via vectors related to Role Based Access Control (RBAC). |
| CVE-2013-5874 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Application Object Library component in Oracle E-Business Suite 11.5.10.2, 12.0.6, 12.1.3, and 12.2.2 allows local users to affect confidentiality via unknown vectors related to Logging. |
| CVE-2013-5873 | Medium | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.52 and 8.53 allows remote attackers to affect confidentiality via unknown vectors related to Integration Broker. |
| CVE-2013-5872 | Low | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows local users to affect availability via vectors related to Name Service Cache Daemon (NSCD). |
| CVE-2013-5871 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle AutoVue Electro-Mechanical Professional component in Oracle Supply Chain Products Suite 20.1.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Web General, a different vulnerability than CVE-2013-5868 and CVE-2014-0444. |
| CVE-2013-5870 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 and JavaFX 2.2.45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to JavaFX. |
| CVE-2013-5869 | Medium | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle WebCenter Portal component in Oracle Fusion Middleware 11.1.1.6.0, 11.1.1.7.0, and 11.1.1.8.0 allows remote attackers to affect confidentiality via unknown vectors related to Page Service. |
| CVE-2013-5868 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle AutoVue Electro-Mechanical Professional component in Oracle Supply Chain Products Suite 20.1.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Web General, a different vulnerability than CVE-2013-5871 and CVE-2014-0444. |
| CVE-2013-5860 | Medium | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.14 and earlier allows remote authenticated users to affect availability via vectors related to GIS. |
| CVE-2013-5858 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, 11.2.0.4, and 12.1.0.1 allows remote authenticated users to affect integrity via unknown vectors, a different vulnerability than CVE-2015-0370. |
| CVE-2013-5853 | Medium | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote attackers to affect availability via unknown vectors. |
| CVE-2013-5834 | Medium | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8 allows local users to affect confidentiality, integrity, and availability via unknown vectors related to ps. |
| CVE-2013-5833 | Medium | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8 and 9 allows local users to affect availability via unknown vectors related to Filesystem. |
| CVE-2013-5821 | Medium | 2014-01-15 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 8, 9, 10, and 11.1 allows local users to affect confidentiality, integrity, and availability via vectors related to RPC. |
| CVE-2013-5808 | Low | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle iPlanet Web Proxy Server component in Oracle Fusion Middleware 4.0 allows remote attackers to affect confidentiality via unknown vectors related to Administration. |
| CVE-2013-5795 | Medium | 2014-01-15 | Mitigation candidate | Working exploit published | Unspecified vulnerability in the Oracle Demantra Demand Management component in Oracle Supply Chain Products Suite 7.2.0.3 SQL-Server, 7.3.0, 7.3.1, 12.2.1, 12.2.2, and 12.2.3 allows remote attackers to affect confidentiality via unknown vectors related to DM Others. |
| CVE-2013-5785 | High | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Reports Developer component in Oracle Fusion Middleware 11.1.1.6, 11.1.1.7, and 11.1.2.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security and Authentication. |
| CVE-2013-5764 | Low | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.3, and 12.1.0.1 allows remote authenticated users to affect availability via unknown vectors. |
| CVE-2013-3830 | High | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Strategic Finance component in Oracle Hyperion 11.1.2.1 and 11.1.2.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Server. |
| CVE-2013-2924 | High | 2013-10-02 | Not applicable | No public exploit | Use-after-free vulnerability in International Components for Unicode (ICU), as used in Google Chrome before 30.0.1599.66 and other products, allows remote attackers to cause a denial of service or possibly have unspecified other impact via unknown vectors. |
| CVE-2013-4316 | High | 2013-09-30 | Outside Waratek scope | No public exploit | Apache Struts 2.0.0 through 2.3.15.1 enables Dynamic Method Invocation by default, which has unknown impact and attack vectors. |