
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
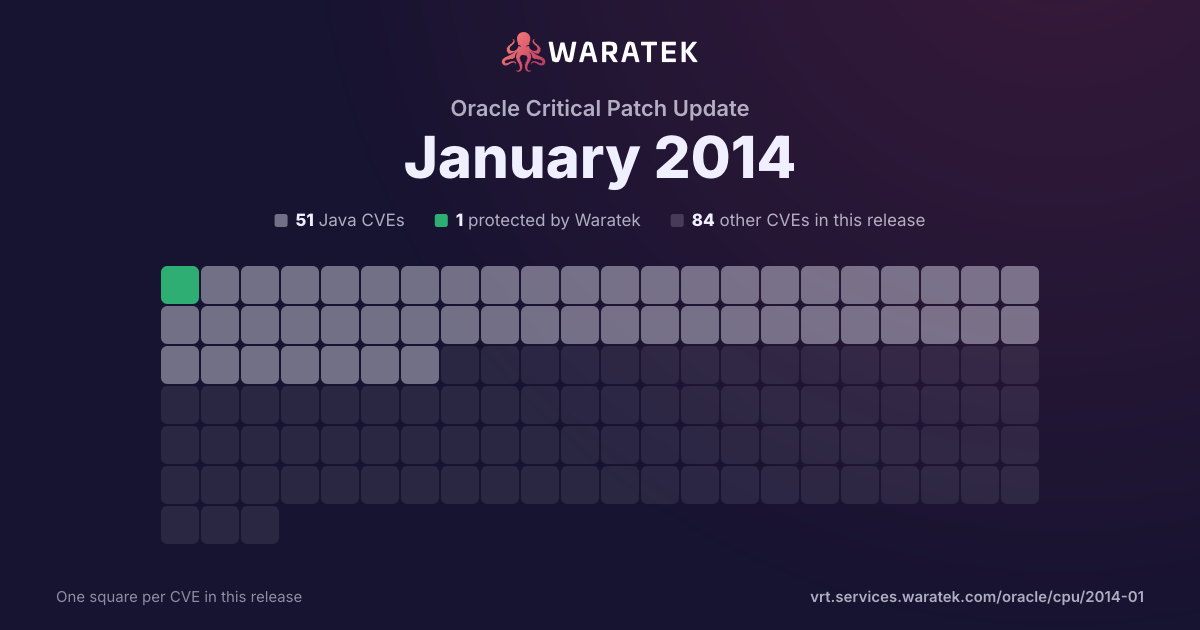
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 19 matches · 3 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
19matches
3in Waratek scope15.8%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
3
15.8%
Outside Waratek scope
14
73.7%
Not applicable
2
10.5%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
19
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
19
100.0%
split by
peak 16 / year
200320042005200620072008200920102011201220132014
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2014-0428 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to CORBA. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to "insufficient security checks in IIOP streams," which allows attackers to escape the sandbox. |
| CVE-2014-0424 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5889, CVE-2013-5902, CVE-2014-0410, CVE-2014-0415, and CVE-2014-0418. |
| CVE-2014-0422 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via vectors related to JNDI. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to missing package access checks in the Naming / JNDI component, which allows attackers to escape the sandbox. |
| CVE-2014-0417 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; JavaFX 2.2.45; and Java SE Embedded 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. |
| CVE-2014-0415 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5889, CVE-2013-5902, CVE-2014-0410, CVE-2014-0418, and CVE-2014-0424. |
| CVE-2014-0410 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5889, CVE-2013-5902, CVE-2014-0415, CVE-2014-0418, and CVE-2014-0424. |
| CVE-2014-0408 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45, when running on OS X, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Hotspot. |
| CVE-2014-0387 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and Java SE 7u45, when running on Firefox, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment. |
| CVE-2014-0385 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45, when installing on OS X, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Install. |
| CVE-2014-0373 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45, and OpenJDK 7, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Serviceability. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to throwing of an incorrect exception when SnmpStatusException should have been used in the SNMP implementation, which allows attackers to escape the sandbox. |
| CVE-2013-5907 | High | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 5.0u55, 6u65, and 7u45; JRockit R27.7.7 and R28.2.9; Java SE Embedded 7u45; and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to 2D. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is due to incorrect input validation in LookupProcessor.cpp in the ICU Layout Engine, which allows attackers to cause a denial of service (crash) or possibly execute arbitrary code via a crafted font file. |
| CVE-2013-5893 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u45 and Java SE Embedded 7u45, and OpenJDK 7, allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Libraries. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the issue is related to improper handling of methods in MethodHandles in HotSpot JVM, which allows attackers to escape the sandbox. |
| CVE-2013-5889 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Deployment, a different vulnerability than CVE-2013-5902, CVE-2014-0410, CVE-2014-0415, CVE-2014-0418, and CVE-2014-0424. |
| CVE-2013-5878 | High | 2014-01-15 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 6u65 and 7u45, Java SE Embedded 7u45, and OpenJDK 7 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security. NOTE: the previous information is from the January 2014 CPU. Oracle has not commented on third-party claims that the Security component does not properly handle null XML namespace (xmlns) attributes during XML document canonicalization, which allows attackers to escape the sandbox. |
| CVE-2013-5785 | High | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Reports Developer component in Oracle Fusion Middleware 11.1.1.6, 11.1.1.7, and 11.1.2.1 allows remote attackers to affect confidentiality, integrity, and availability via unknown vectors related to Security and Authentication. |
| CVE-2013-3830 | High | 2014-01-15 | No exploit published | No public exploit | Unspecified vulnerability in the Hyperion Strategic Finance component in Oracle Hyperion 11.1.2.1 and 11.1.2.2 allows remote authenticated users to affect confidentiality, integrity, and availability via unknown vectors related to Server. |
| CVE-2013-2924 | High | 2013-10-02 | Not applicable | No public exploit | Use-after-free vulnerability in International Components for Unicode (ICU), as used in Google Chrome before 30.0.1599.66 and other products, allows remote attackers to cause a denial of service or possibly have unspecified other impact via unknown vectors. |
| CVE-2013-4316 | High | 2013-09-30 | Outside Waratek scope | No public exploit | Apache Struts 2.0.0 through 2.3.15.1 enables Dynamic Method Invocation by default, which has unknown impact and attack vectors. |
| CVE-2003-1067 | High | 2003-06-19 | Not applicable | No public exploit | Multiple buffer overflows in the (1) dbm_open function, as used in ndbm and dbm, and the (2) dbminit function in Solaris 2.6 through 9 allow local users to gain root privileges via long arguments to Xsun or other programs that use these functions. |