
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
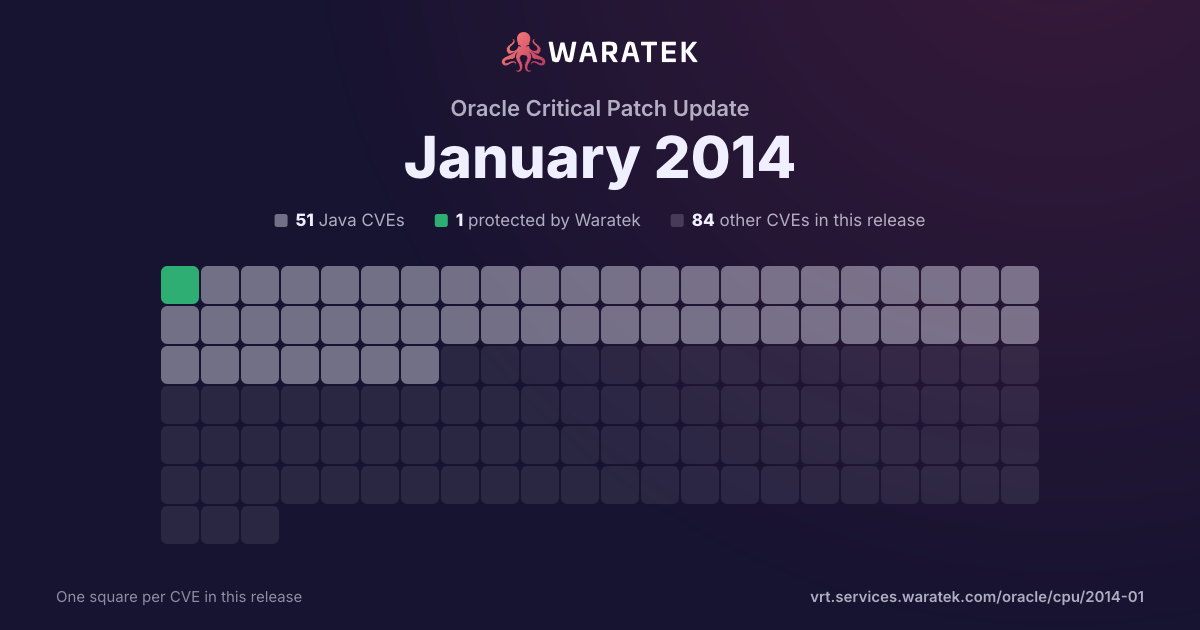
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 9 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 0 public PoC · 0 EPSS ≥ 0.5
9matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
0public PoC0.0%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
3
33.3%
Not applicable
6
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
9
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
9
100.0%
split by
peak 7 / year
20032004200520062007200820092010201120122013
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-1862 | Medium | 2013-06-10 | Not applicable | No public exploit | mod_rewrite.c in the mod_rewrite module in the Apache HTTP Server 2.2.x before 2.2.25 writes data to a log file without sanitizing non-printable characters, which might allow remote attackers to execute arbitrary commands via an HTTP request containing an escape sequence for a terminal emulator. |
| CVE-2013-2071 | Low | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/core/AsyncContextImpl.java in Apache Tomcat 7.x before 7.0.40 does not properly handle the throwing of a RuntimeException in an AsyncListener in an application, which allows context-dependent attackers to obtain sensitive request information intended for other applications in opportunistic circumstances via an application that records the requests that it processes. |
| CVE-2013-2067 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | java/org/apache/catalina/authenticator/FormAuthenticator.java in the form authentication feature in Apache Tomcat 6.0.21 through 6.0.36 and 7.x before 7.0.33 does not properly handle the relationships between authentication requirements and sessions, which allows remote attackers to inject a request into a session by sending this request during completion of the login form, a variant of a session fixation attack. |
| CVE-2012-3544 | Medium | 2013-06-01 | Outside Waratek scope | No public exploit | Apache Tomcat 6.x before 6.0.37 and 7.x before 7.0.30 does not properly handle chunk extensions in chunked transfer coding, which allows remote attackers to cause a denial of service by streaming data. |
| CVE-2013-1654 | Medium | 2013-03-20 | Not applicable | No public exploit | Puppet 2.7.x before 2.7.21 and 3.1.x before 3.1.1, and Puppet Enterprise 2.7.x before 2.7.2, does not properly negotiate the SSL protocol between client and master, which allows remote attackers to conduct SSLv2 downgrade attacks against SSLv3 sessions via unspecified vectors. |
| CVE-2012-3499 | Medium | 2013-02-26 | Not applicable | No public exploit | Multiple cross-site scripting (XSS) vulnerabilities in the Apache HTTP Server 2.2.x before 2.2.24-dev and 2.4.x before 2.4.4 allow remote attackers to inject arbitrary web script or HTML via vectors involving hostnames and URIs in the (1) mod_imagemap, (2) mod_info, (3) mod_ldap, (4) mod_proxy_ftp, and (5) mod_status modules. |
| CVE-2013-1620 | Medium | 2013-02-08 | Not applicable | No public exploit | The TLS implementation in Mozilla Network Security Services (NSS) does not properly consider timing side-channel attacks on a noncompliant MAC check operation during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, a related issue to CVE-2013-0169. |
| CVE-2012-4605 | Medium | 2012-08-23 | Not applicable | No public exploit | The default configuration of the SMTP component in Websense Email Security 6.1 through 7.3 enables weak SSL ciphers in the "SurfControl plc\SuperScout Email Filter\SMTP" registry key, which makes it easier for remote attackers to obtain sensitive information by sniffing the network and then conducting a brute-force attack against encrypted session data. |
| CVE-2003-1067 | High | 2003-06-19 | Not applicable | No public exploit | Multiple buffer overflows in the (1) dbm_open function, as used in ndbm and dbm, and the (2) dbminit function in Solaris 2.6 through 9 allow local users to gain root privileges via long arguments to Xsun or other programs that use these functions. |