
Oracle Critical Patch Update January 2014
Released January 2014 · Oracle's advisory ↗ · ← Critical Patch Update, October 2013 · Critical Patch Update, April 2014 →
135 CVEs in this release, one square each
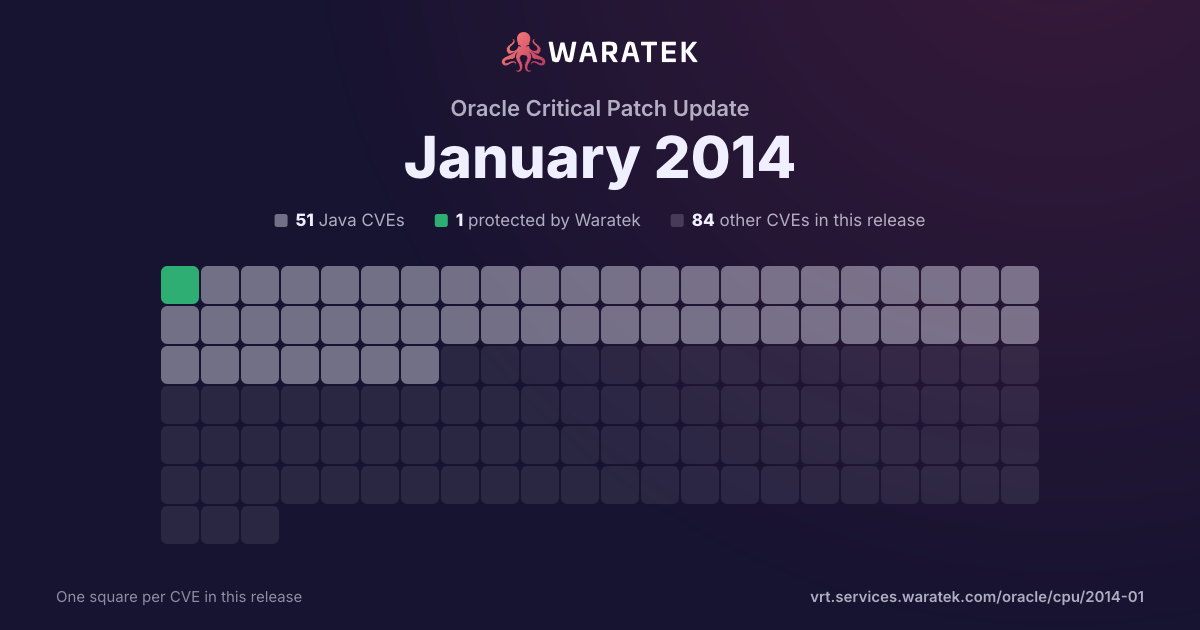
By status
1Protected by Waratek5Mitigation candidate45No exploit published44Outside Waratek scope40Not applicable
No exploit published. For 45 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 4 matches · 0 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
4matches
0in Waratek scope0.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
1public PoC25.0%
1EPSS ≥ 0.525.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
1
25.0%
Not applicable
3
75.0%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
4
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
25.0%
Forecast only
1
25.0%
No public exploit
2
50.0%
split by
peak 2 / year
2003200420052006200720082009201020112012
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2012-4605 | Medium | 2012-08-23 | Not applicable | No public exploit | The default configuration of the SMTP component in Websense Email Security 6.1 through 7.3 enables weak SSL ciphers in the "SurfControl plc\SuperScout Email Filter\SMTP" registry key, which makes it easier for remote attackers to obtain sensitive information by sniffing the network and then conducting a brute-force attack against encrypted session data. |
| CVE-2007-1858 | Low | 2007-05-10 | Outside Waratek scope | Proof of concept only | The default SSL cipher configuration in Apache Tomcat 4.1.28 through 4.1.31, 5.0.0 through 5.0.30, and 5.5.0 through 5.5.17 uses certain insecure ciphers, including the anonymous cipher, which allows remote attackers to obtain sensitive information or have other, unspecified impacts. |
| CVE-2007-0009 | Medium | 2007-02-26 | Not applicable | Forecast only | Stack-based buffer overflow in the SSLv2 support in Mozilla Network Security Services (NSS) before 3.11.5, as used by Firefox before 1.5.0.10 and 2.x before 2.0.0.2, Thunderbird before 1.5.0.10, SeaMonkey before 1.0.8, and certain Sun Java System server products before 20070611, allows remote attackers to execute arbitrary code via invalid "Client Master Key" length values. |
| CVE-2003-1067 | High | 2003-06-19 | Not applicable | No public exploit | Multiple buffer overflows in the (1) dbm_open function, as used in ndbm and dbm, and the (2) dbminit function in Solaris 2.6 through 9 allow local users to gain root privileges via long arguments to Xsun or other programs that use these functions. |