
Oracle Critical Patch Update October 2013
Released October 2013 · Oracle's advisory ↗ · ← Critical Patch Update, July 2013 · Critical Patch Update, January 2014 →
124 CVEs in this release, one square each
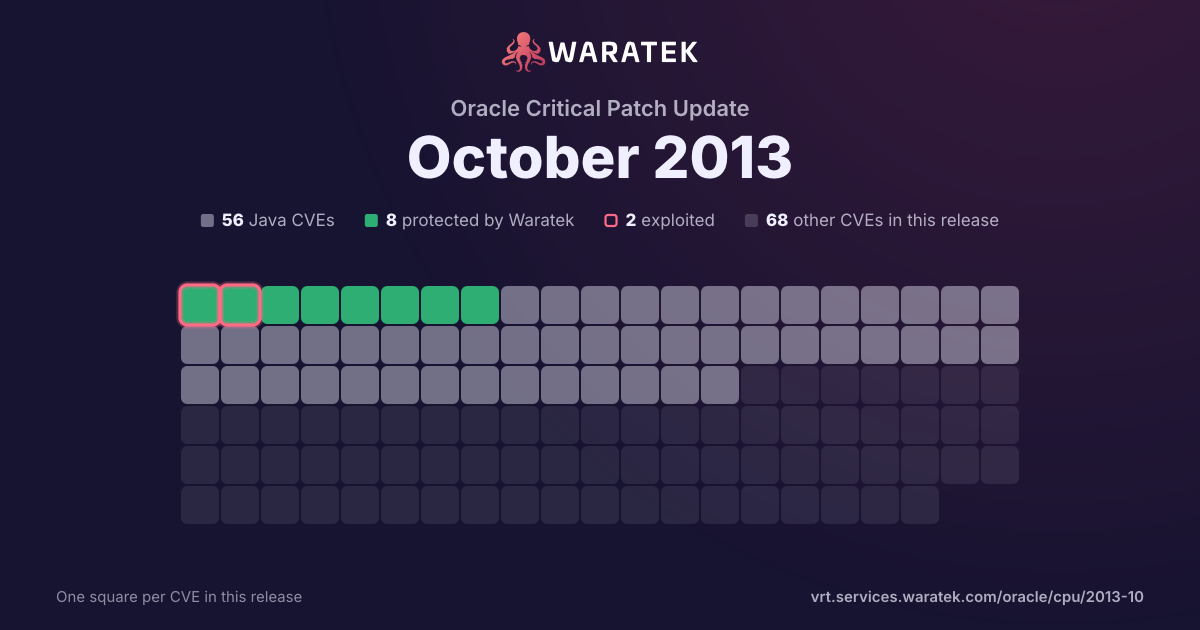
By status
8Protected by Waratek48No exploit published44Outside Waratek scope24Not applicable
2Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 18 matches · 9 in Waratek scope · 0 protected · 0 exploited · 0 CISA KEV · 2 public PoC · 0 EPSS ≥ 0.5
18matches
9in Waratek scope50.0%
0protected0.0%
0exploited0.0%
0CISA KEV0.0%
2public PoC11.1%
0EPSS ≥ 0.50.0%
Protected by Waratek
0
0.0%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
9
50.0%
Outside Waratek scope
3
16.7%
Not applicable
6
33.3%
Withdrawn CVE
0
0.0%
blocked by ARMR today
0
0.0%
partly blocked
0
0.0%
not blocked
18
100.0%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
2
11.1%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
16
88.9%
split by
peak 16 / month
Feb 131
Outside Waratek scope1
Low1
not blocked1
No public exploit1
Mar 130
Apr 130
May 130
Jun 130
Jul 130
Aug 130
Sep 130
Oct 1316
No exploit published8
Outside Waratek scope2
Not applicable6
Low16
not blocked16
Working exploit published2
No public exploit14
Nov 130
Dec 131
No exploit published1
Low1
not blocked1
No public exploit1
Feb 13Mar 13Apr 13May 13Jun 13Jul 13Aug 13Sep 13Oct 13Nov 13Dec 13
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-5763 | Low | 2013-12-12 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 allows context-dependent attackers to affect availability via unknown vectors related to Outside In Maintenance. NOTE: the original disclosure of this issue erroneously mapped it to CVE-2013-3624. |
| CVE-2013-5865 | Low | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 11.1 allows local users to affect availability via unknown vectors related to Utility/User administration. |
| CVE-2013-5857 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Health Sciences InForm component in Oracle Industry Applications 4.5 SP3, 4.5 SP3a-k, 4.6 SP0, 4.6 SP0a-c, 4.6 SP1, 4.6 SP1a-c, 4.6 SP2, 4.6 SP2a-c, 5.0 SP0, 5.0 SP0a, 5.0 SP1, and 5.0 SP1a-b allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Web. |
| CVE-2013-5856 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Health Sciences InForm component in Oracle Industry Applications 4.5 SP3, 4.5 SP3a-k, 4.6 SP0, 4.6 SP0a-c, 4.6 SP1, 4.6 SP1a-c, 4.6 SP2, 4.6 SP2a-c, 5.0 SP0, 5.0 SP0a, 5.0 SP1, 5.0 SP1a-b, 5.5 SP0, 5.5 SP0b, 5.5.1, and 6.0.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Web. |
| CVE-2013-5854 | Low | 2013-10-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u40 and earlier and JavaFX 2.2.40 and earlier allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2013-5837 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Health Sciences InForm component in Oracle Industry Applications 4.6 SP0, 4.6 SP0a-c, 4.6 SP1, 4.6 SP1a-c, 4.6 SP2, 4.6 SP2a-c, 5.0 SP0, 5.0 SP0a, 5.0 SP1, 5.0 SP1a-b, 5.0.3, and 5.0.4 allows remote authenticated users to affect confidentiality via unknown vectors related to Cognos. |
| CVE-2013-5811 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Health Sciences InForm component in Oracle Industry Applications 4.5 SP3, 4.5 SP3a-k, 4.6 SP0, 4.6 SP0a-c, 4.6 SP1, 4.6 SP1a-c, 4.6 SP2, 4.6 SP2a-c, 5.0 SP0, 5.0 SP0a, 5.0 SP1, and 5.0 SP1a-b allows remote authenticated users to affect confidentiality via unknown vectors related to Web. |
| CVE-2013-5803 | Low | 2013-10-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in Oracle Java SE 7u40 and earlier, Java SE 6u60 and earlier, Java SE 5.0u51 and earlier, JRockit R28.2.8 and earlier, JRockit R27.7.6 and earlier, and Java SE Embedded 7u40 and earlier allows remote attackers to affect availability via vectors related to JGSS. |
| CVE-2013-5797 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in Oracle Java SE 7u40 and earlier, Java SE 6u60 and earlier, Java SE 5.0u51 and earlier, JRockit R28.2.8 and earlier, JRockit R27.7.6 and earlier, and JavaFX 2.2.40 and earlier allows remote authenticated users to affect integrity via unknown vectors related to Javadoc. |
| CVE-2013-5793 | Low | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle MySQL Server 5.6.12 and earlier allows remote authenticated users to affect availability via unknown vectors related to InnoDB, a different vulnerability than CVE-2013-5786. |
| CVE-2013-5791 | Low | 2013-10-16 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle Outside In Technology component in Oracle Fusion Middleware 8.4.0 and 8.4.1 allows context-dependent attackers to affect availability via unknown vectors related to Outside In Filters. NOTE: the previous information is from the October 2013 CPU. Oracle has not commented on claims from a third party that the issue is a stack-based buffer overflow in the Microsoft Access 1.x parser in vsacs.dll before 8.4.0.108 and before 8.4.1.52, which allows attackers to execute arbitrary code via a long field (aka column) name. |
| CVE-2013-5772 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Java SE component in Oracle Java SE Java SE 7u40 and earlier and Java SE 6u60 and earlier allows remote attackers to affect integrity via unknown vectors related to jhat. |
| CVE-2013-5770 | Low | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in the MySQL Server component in Oracle MySQL 5.6.11 and earlier allows remote authenticated users to affect availability via unknown vectors related to Locking. |
| CVE-2013-5762 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Siebel CTMS component in Oracle Industry Applications 8.1.1.x allows local users to affect confidentiality and availability via unknown vectors related to SC-OC Integration. |
| CVE-2013-3842 | Low | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability Oracle Solaris 10 allows local users to affect confidentiality via vectors related to Oracle Configuration Manager (OCM). |
| CVE-2013-3836 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Cache component in Oracle Fusion Middleware 11.1.1.6 and 11.1.1.7 allows remote authenticated users to affect confidentiality via vectors related to ESI/Partial Page Caching. |
| CVE-2013-3792 | Low | 2013-10-16 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.18, 4.0.20, 4.1.28, and 4.2.18 allows local users to affect availability via unknown vectors related to Core. |
| CVE-2013-0169 | Low | 2013-02-08 | Outside Waratek scope | No public exploit | The TLS protocol 1.1 and 1.2 and the DTLS protocol 1.0 and 1.2, as used in OpenSSL, OpenJDK, PolarSSL, and other products, do not properly consider timing side-channel attacks on a MAC check requirement during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, aka the "Lucky Thirteen" issue. |