
Oracle Critical Patch Update October 2013
Released October 2013 · Oracle's advisory ↗ · ← Critical Patch Update, July 2013 · Critical Patch Update, January 2014 →
124 CVEs in this release, one square each
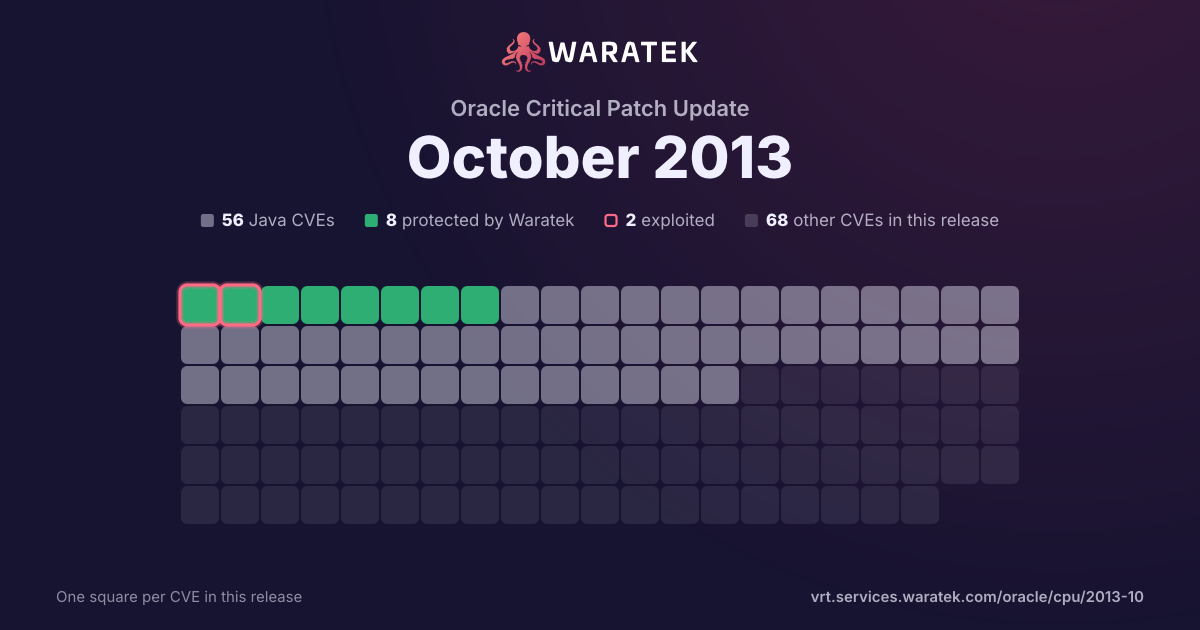
By status
8Protected by Waratek48No exploit published44Outside Waratek scope24Not applicable
2Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 3 matches · 1 in Waratek scope · 1 protected · 0 exploited · 0 CISA KEV · 1 public PoC · 1 EPSS ≥ 0.5
3matches
1in Waratek scope33.3%
1protected33.3%
0exploited0.0%
0CISA KEV0.0%
1public PoC33.3%
1EPSS ≥ 0.533.3%
Protected by Waratek
1
33.3%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
0
0.0%
Outside Waratek scope
0
0.0%
Not applicable
2
66.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
1
33.3%
partly blocked
0
0.0%
not blocked
2
66.7%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
0
0.0%
Working exploit published
0
0.0%
Proof of concept only
1
33.3%
Forecast only
0
0.0%
No public exploit
2
66.7%
split by
peak 2 / quarter
Q3 11Q4 11Q1 12Q2 12Q3 12Q4 12Q1 13Q2 13Q3 13
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-2172 | Medium | 2013-08-20 | Protected by Waratek | No public exploit | jcp/xml/dsig/internal/dom/DOMCanonicalizationMethod.java in Apache Santuario XML Security for Java 1.4.x before 1.4.8 and 1.5.x before 1.5.5 allows context-dependent attackers to spoof an XML Signature by using the CanonicalizationMethod parameter to specify an arbitrary weak "canonicalization algorithm to apply to the SignedInfo part of the Signature." |
| CVE-2013-0149 | Medium | 2013-08-05 | Not applicable | No public exploit | The OSPF implementation in Cisco IOS 12.0 through 12.4 and 15.0 through 15.3, IOS-XE 2.x through 3.9.xS, ASA and PIX 7.x through 9.1, FWSM, NX-OS, and StarOS before 14.0.50488 does not properly validate Link State Advertisement (LSA) type 1 packets before performing operations on the LSA database, which allows remote attackers to cause a denial of service (routing disruption) or obtain sensitive packet information via a (1) unicast or (2) multicast packet, aka Bug IDs CSCug34485, CSCug34469, CSCug39762, CSCug63304, and CSCug39795. |
| CVE-2011-3389 | Medium | 2011-09-06 | Not applicable | Proof of concept only | The SSL protocol, as used in certain configurations in Microsoft Windows and Microsoft Internet Explorer, Mozilla Firefox, Google Chrome, Opera, and other products, encrypts data by using CBC mode with chained initialization vectors, which allows man-in-the-middle attackers to obtain plaintext HTTP headers via a blockwise chosen-boundary attack (BCBA) on an HTTPS session, in conjunction with JavaScript code that uses (1) the HTML5 WebSocket API, (2) the Java URLConnection API, or (3) the Silverlight WebClient API, aka a "BEAST" attack. |