
Oracle Critical Patch Update October 2013
Released October 2013 · Oracle's advisory ↗ · ← Critical Patch Update, July 2013 · Critical Patch Update, January 2014 →
124 CVEs in this release, one square each
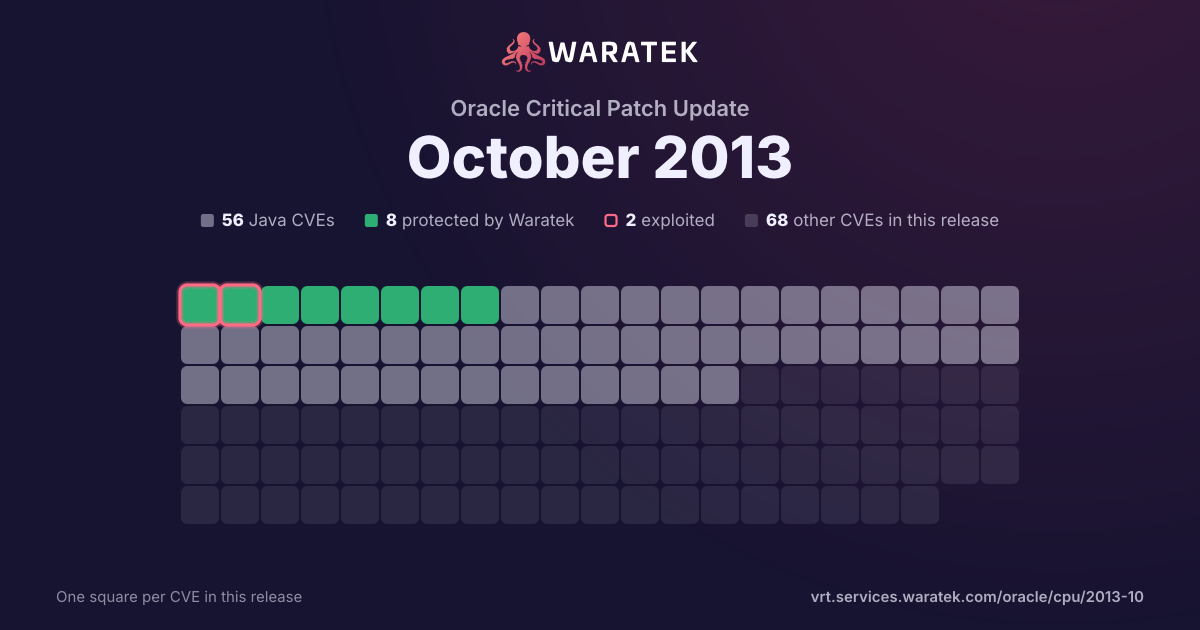
By status
8Protected by Waratek48No exploit published44Outside Waratek scope24Not applicable
2Exploited, marked by the ring
No exploit published. For 43 of them, Oracle's security advisory is the source of public detail.
Protected by Waratek. Waratek RASP can block exploitation of these on systems that have not applied the patch yet.
Overview 123 matches · 56 in Waratek scope · 8 protected · 2 exploited · 1 CISA KEV · 4 public PoC · 1 EPSS ≥ 0.5
123matches
56in Waratek scope45.5%
8protected6.5%
2exploited1.6%
1CISA KEV0.8%
4public PoC3.3%
1EPSS ≥ 0.50.8%
Protected by Waratek
8
6.5%
Rule in development
0
0.0%
Mitigation candidate
0
0.0%
No exploit published
48
39.0%
Outside Waratek scope
44
35.8%
Not applicable
23
18.7%
Withdrawn CVE
0
0.0%
blocked by ARMR today
8
6.5%
partly blocked
0
0.0%
not blocked
115
93.5%
not established
0
0.0%
unrecorded
0
0.0%
Exploited
2
1.6%
Working exploit published
2
1.6%
Proof of concept only
0
0.0%
Forecast only
0
0.0%
No public exploit
119
96.7%
split by
peak 116 / month
Aug 121
Not applicable1
High1
not blocked1
No public exploit1
Sep 120
Oct 120
Nov 120
Dec 120
Jan 130
Feb 131
Outside Waratek scope1
Low1
not blocked1
No public exploit1
Mar 130
Apr 130
May 130
Jun 130
Jul 132
Protected by Waratek2
Critical1
High1
blocked by ARMR today2
Exploited1
No public exploit1
Aug 132
Protected by Waratek1
Not applicable1
Medium2
blocked by ARMR today1
not blocked1
No public exploit2
Sep 130
Oct 13116
Protected by Waratek5
No exploit published47
Outside Waratek scope43
Not applicable21
High25
Medium75
Low16
blocked by ARMR today5
not blocked111
Exploited1
Working exploit published2
No public exploit113
Nov 130
Dec 131
No exploit published1
Low1
not blocked1
No public exploit1
Aug 12Oct 12Dec 12Feb 13Apr 13Jun 13Aug 13Oct 13Dec 13
| CVE | Severity | Published▾ | Status | Exploitation | Description |
|---|---|---|---|---|---|
| CVE-2013-3838 | Medium | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle SPARC Enterprise T & M Series Servers running Sun System Firmware before 6.7.13 for SPARC T1, 7.4.6.c for SPARC T2, 8.3.0.b for SPARC T3 & T4, 9.0.0.d for SPARC T5 and 9.0.1.e for SPARC M5 allows local users to affect availability via unknown vectors related to Sun System Firmware/Hypervisor. |
| CVE-2013-3837 | Medium | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in Oracle Solaris 10 and 11.1 allows remote attackers to affect availability via unknown vectors related to Cacao. |
| CVE-2013-3836 | Low | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Cache component in Oracle Fusion Middleware 11.1.1.6 and 11.1.1.7 allows remote authenticated users to affect confidentiality via vectors related to ESI/Partial Page Caching. |
| CVE-2013-3835 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise PeopleTools component in Oracle PeopleSoft Products 8.51, 8.52, and 8.53 allows remote attackers to affect confidentiality via unknown vectors related to Integration Broker. |
| CVE-2013-3834 | Medium | 2013-10-16 | Not applicable | No public exploit | Unspecified vulnerability in the Oracle Secure Global Desktop component in Oracle Virtualization 5 allows remote attackers to affect availability via unknown vectors related to ttaauxserv. |
| CVE-2013-3833 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Access Manager component in Oracle Fusion Middleware 11.1.1.5.0 and 11.1.2.0.0 allows remote attackers to affect integrity via unknown vectors related to Authentication Engine. |
| CVE-2013-3832 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Siebel Server Remote component in Oracle Siebel CRM 8.1.1 and 8.2.2 allows remote authenticated users to affect integrity via unknown vectors related to File System Management. |
| CVE-2013-3831 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Portal component in Oracle Fusion Middleware 11.1.1.6.0 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to Demos. |
| CVE-2013-3829 | Medium | 2013-10-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Java SE, Java SE Embedded component in Oracle Java SE Java SE 7u40 and earlier, Java SE 6u60 and earlier, Java SE 5.0u51 and earlier, and Java SE Embedded 7u40 and earlier allows remote attackers to affect confidentiality and integrity via unknown vectors related to Libraries. |
| CVE-2013-3828 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Web Services component in Oracle Fusion Middleware 10.1.3.5.0 and 11.1.1.6.0 allows remote attackers to affect confidentiality via unknown vectors related to Test Page. |
| CVE-2013-3827 | Medium | 2013-10-16 | Protected by Waratek | Exploited | Unspecified vulnerability in the Oracle GlassFish Server component in Oracle Fusion Middleware 2.1.1, 3.0.1, and 3.1.2; the Oracle JDeveloper component in Oracle Fusion Middleware 11.1.2.3.0, 11.1.2.4.0, and 12.1.2.0.0; and the Oracle WebLogic Server component in Oracle Fusion Middleware 10.3.6.0 and 12.1.1 allows remote attackers to affect confidentiality via unknown vectors related to Java Server Faces or Web Container. |
| CVE-2013-3826 | Medium | 2013-10-16 | Outside Waratek scope | No public exploit | Unspecified vulnerability in the Core RDBMS component in Oracle Database Server 11.1.0.7, 11.2.0.2, 11.2.0.3, and 12.1.0.1 allows remote attackers to affect confidentiality via unknown vectors. |
| CVE-2013-3814 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Oracle Retail Invoice Matching component in Oracle Industry Applications 10.2, 11.0, 12.0, 12.0IN, 12.1, 13.0, 13.1, and 13.2 allows remote authenticated users to affect confidentiality and integrity via unknown vectors related to System Administration. |
| CVE-2013-3792 | Low | 2013-10-16 | Not applicable | Working exploit published | Unspecified vulnerability in the Oracle VM VirtualBox component in Oracle Virtualization VirtualBox prior to 3.2.18, 4.0.20, 4.1.28, and 4.2.18 allows local users to affect availability via unknown vectors related to Core. |
| CVE-2013-3785 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the PeopleSoft Enterprise HRMS component in Oracle PeopleSoft Products 9.1 allows remote authenticated users to affect confidentiality via unknown vectors related to Career's Home. |
| CVE-2013-3766 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Primavera P6 Enterprise Project Portfolio Management component in Oracle Primavera Products Suite 8.1, 8.2, and 8.3 allows remote authenticated users to affect integrity via unknown vectors related to Web Access. |
| CVE-2013-3762 | Medium | 2013-10-16 | No exploit published | No public exploit | Unspecified vulnerability in the Enterprise Manager Base Platform component in Oracle Enterprise Manager Grid Control EM Base Platform 10.2.0.5 and 11.1.0.1; EM DB Control 11.1.0.7, 11.2.0.2, and 11.2.0.3; and EM Plugin for DB 12.1.0.2, 12.1.0.3, and 12.1.0.4 allows remote attackers to affect integrity via unknown vectors related to Schema Management. |
| CVE-2013-2172 | Medium | 2013-08-20 | Protected by Waratek | No public exploit | jcp/xml/dsig/internal/dom/DOMCanonicalizationMethod.java in Apache Santuario XML Security for Java 1.4.x before 1.4.8 and 1.5.x before 1.5.5 allows context-dependent attackers to spoof an XML Signature by using the CanonicalizationMethod parameter to specify an arbitrary weak "canonicalization algorithm to apply to the SignedInfo part of the Signature." |
| CVE-2013-0149 | Medium | 2013-08-05 | Not applicable | No public exploit | The OSPF implementation in Cisco IOS 12.0 through 12.4 and 15.0 through 15.3, IOS-XE 2.x through 3.9.xS, ASA and PIX 7.x through 9.1, FWSM, NX-OS, and StarOS before 14.0.50488 does not properly validate Link State Advertisement (LSA) type 1 packets before performing operations on the LSA database, which allows remote attackers to cause a denial of service (routing disruption) or obtain sensitive packet information via a (1) unicast or (2) multicast packet, aka Bug IDs CSCug34485, CSCug34469, CSCug39762, CSCug63304, and CSCug39795. |
| CVE-2013-4002 | High | 2013-07-23 | Protected by Waratek | No public exploit | XMLscanner.java in Apache Xerces2 Java Parser before 2.12.0, as used in the Java Runtime Environment (JRE) in IBM Java 5.0 before 5.0 SR16-FP3, 6 before 6 SR14, 6.0.1 before 6.0.1 SR6, and 7 before 7 SR5 as well as Oracle Java SE 7u40 and earlier, Java SE 6u60 and earlier, Java SE 5.0u51 and earlier, JRockit R28.2.8 and earlier, JRockit R27.7.6 and earlier, Java SE Embedded 7u40 and earlier, and possibly other products allows remote attackers to cause a denial of service via vectors related to XML attribute names. |
| CVE-2013-2251 | Critical | 2013-07-20 | Protected by Waratek | Exploited | Apache Struts 2.0.0 through 2.3.15 allows remote attackers to execute arbitrary OGNL expressions via a parameter with a crafted (1) action:, (2) redirect:, or (3) redirectAction: prefix. |
| CVE-2013-0169 | Low | 2013-02-08 | Outside Waratek scope | No public exploit | The TLS protocol 1.1 and 1.2 and the DTLS protocol 1.0 and 1.2, as used in OpenSSL, OpenJDK, PolarSSL, and other products, do not properly consider timing side-channel attacks on a MAC check requirement during the processing of malformed CBC padding, which allows remote attackers to conduct distinguishing attacks and plaintext-recovery attacks via statistical analysis of timing data for crafted packets, aka the "Lucky Thirteen" issue. |
| CVE-2012-2750 | High | 2012-08-17 | Not applicable | No public exploit | Unspecified vulnerability in MySQL 5.5.x before 5.5.23 has unknown impact and attack vectors related to a "Security Fix", aka Bug #59533. NOTE: this might be a duplicate of CVE-2012-1689, but as of 20120816, Oracle has not commented on this possibility. |